Search results for tag #mastoadmin

#mastoadmin moessingen.social hat das Sicherheitsupdate auf Mastodon 4.7.6 erhalten. Viel Spaß im Fediverse!
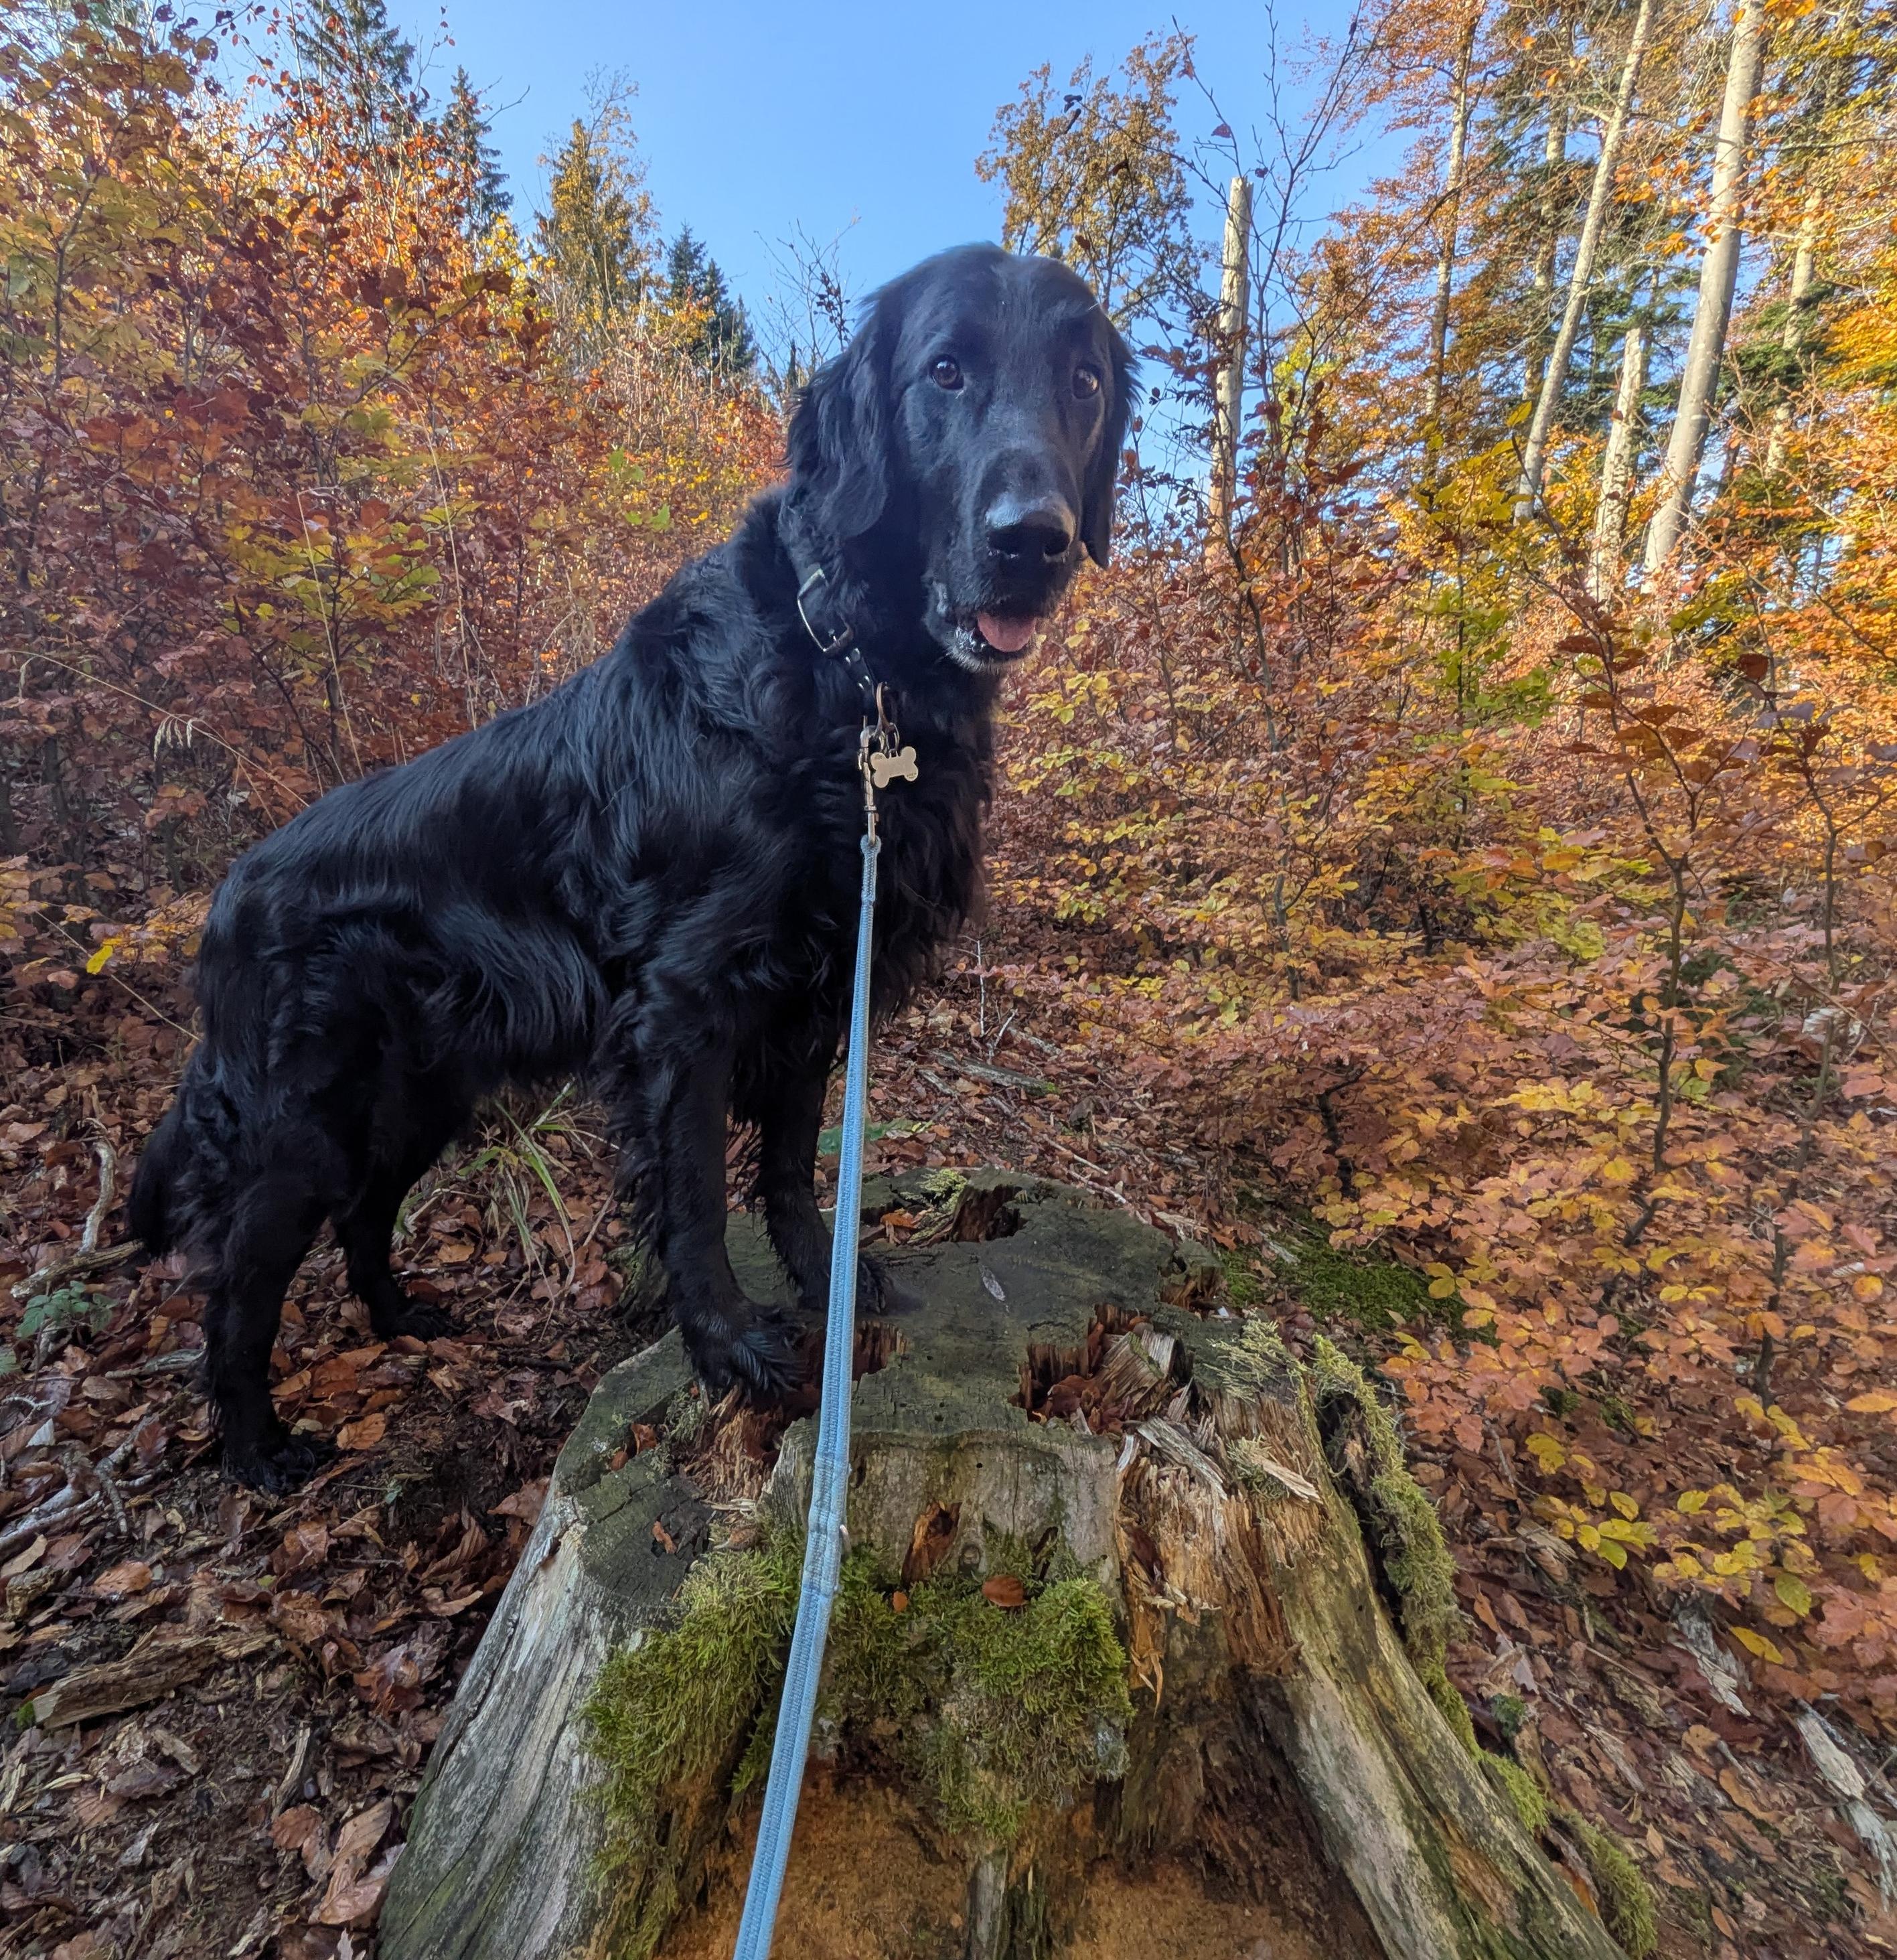
Edit: Update-Hund nachgeliefert.
#mastodogs #dogsofmastodon #dogs
Alt...
Emil steht mit den Vorderfüßen auf einem Baumstumpf
The second beta for Mastodon 5.0 is available!
It contains many improvements to the new user interface based on the feedback we received, the security fixes from our latest release, a number of bug fixes and a few new features.
We expect to have a Release Candidate version ready next week, and the final release the week after.
As usual, for servers administrators who want to test it, you can find the detailed released notes and upgrades instructions here: https://github.com/mastodon/mastodon/releases/tag/v5.0.0-beta.2

We need a rule: if you open an account and don't post something -- anything, even an hello world -- in the first 2 months, you account is deleted.
That would save admins a lot of grief.

Fedi Block the domain: letschatnow.me
Why?
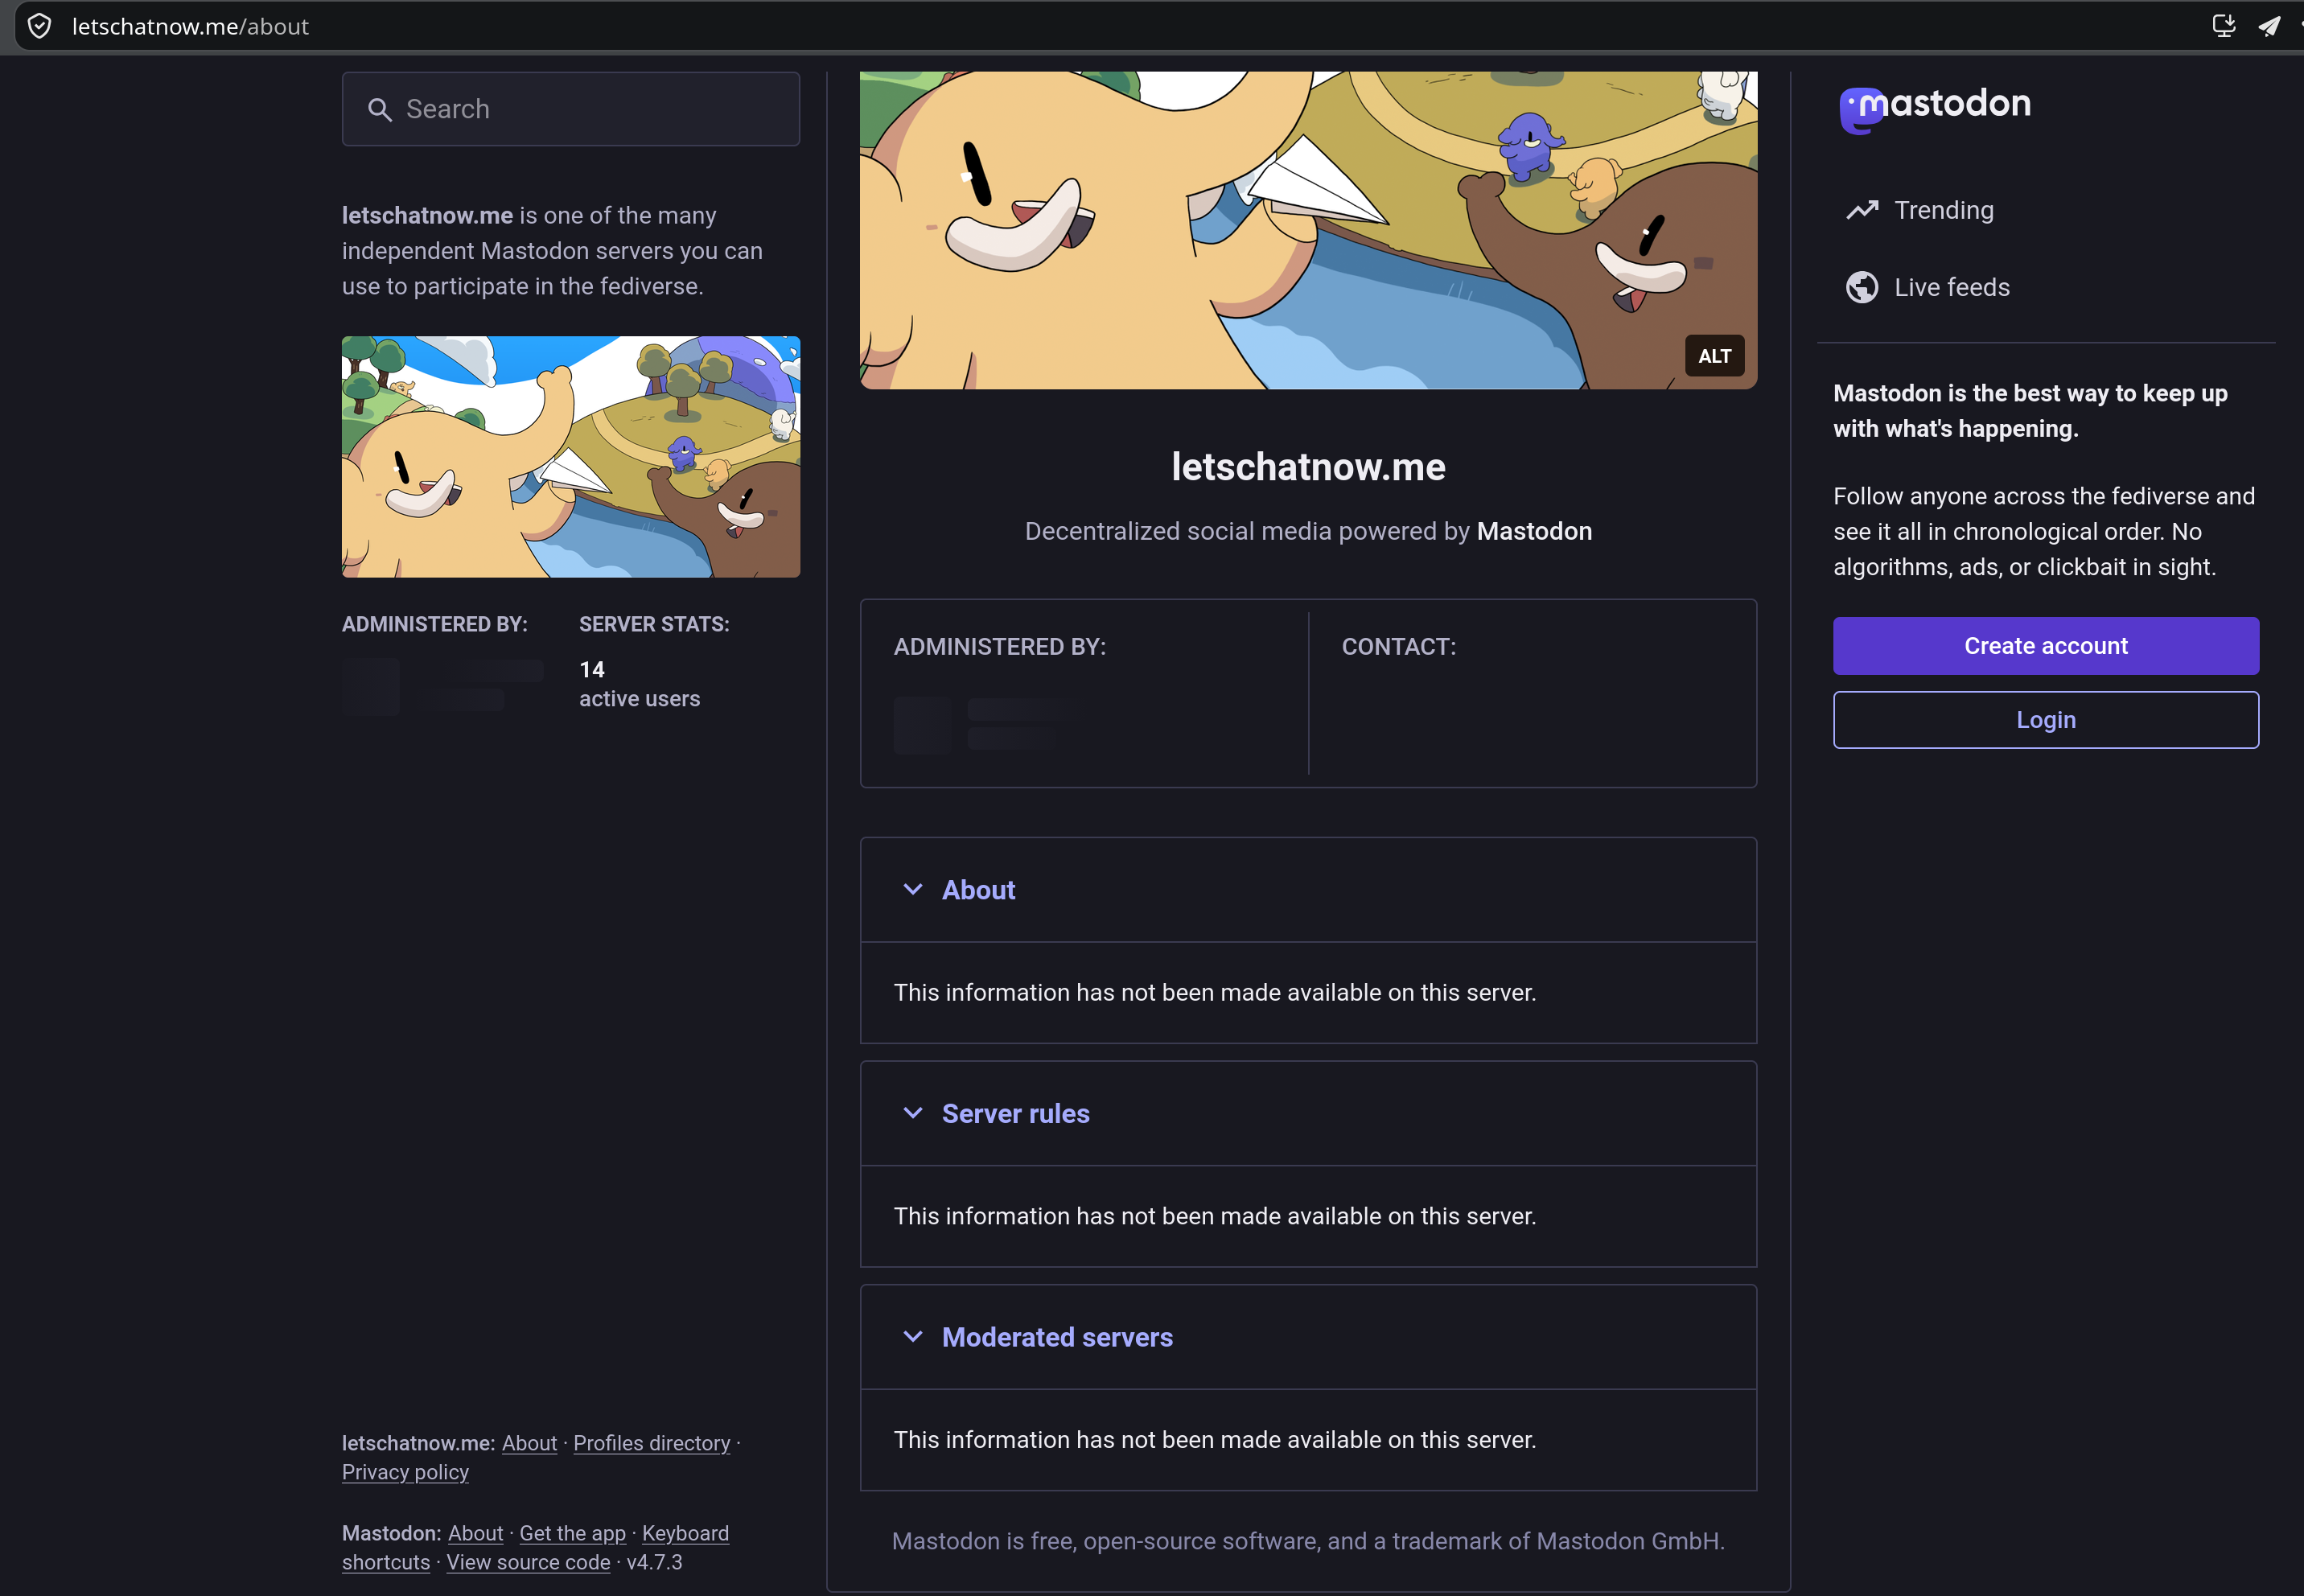
All 14 users are the same person promoting their adult content OnlyFans.
In fact, if you visit their about page, there is no admin, no contact information, no about page details, no rules, etc. It has all been nullified. https://letschatnow.me/about
If you want to see their public timeline, I caution you that it contains adult content with links to their OnlyFans. NSFW: https://letschatnow.me/public/local
#FediBlock #MastoAdmin #FediAdmin #Spam
Alt...
A sceenshot shows their about page with no admin listed, no rules, no terms, no details, no contact information. It has all been nullified.
 GLITCH-SOC Release Watcher » 🤖 🌐
@glitch_soc_release_watcher@mastodon.kodesumber.com
v5.0.0-beta.2
WarningThis is a pre-release! This has not been as widely tested as regular releases, although it is still tested on mastodon.social and some other servers. If you update to this release, you will not be able to safely downgrade to the existing...
https://github.com/glitch-soc/mastodon/releases/tag/v5.0.0-beta.2
Oh neat!
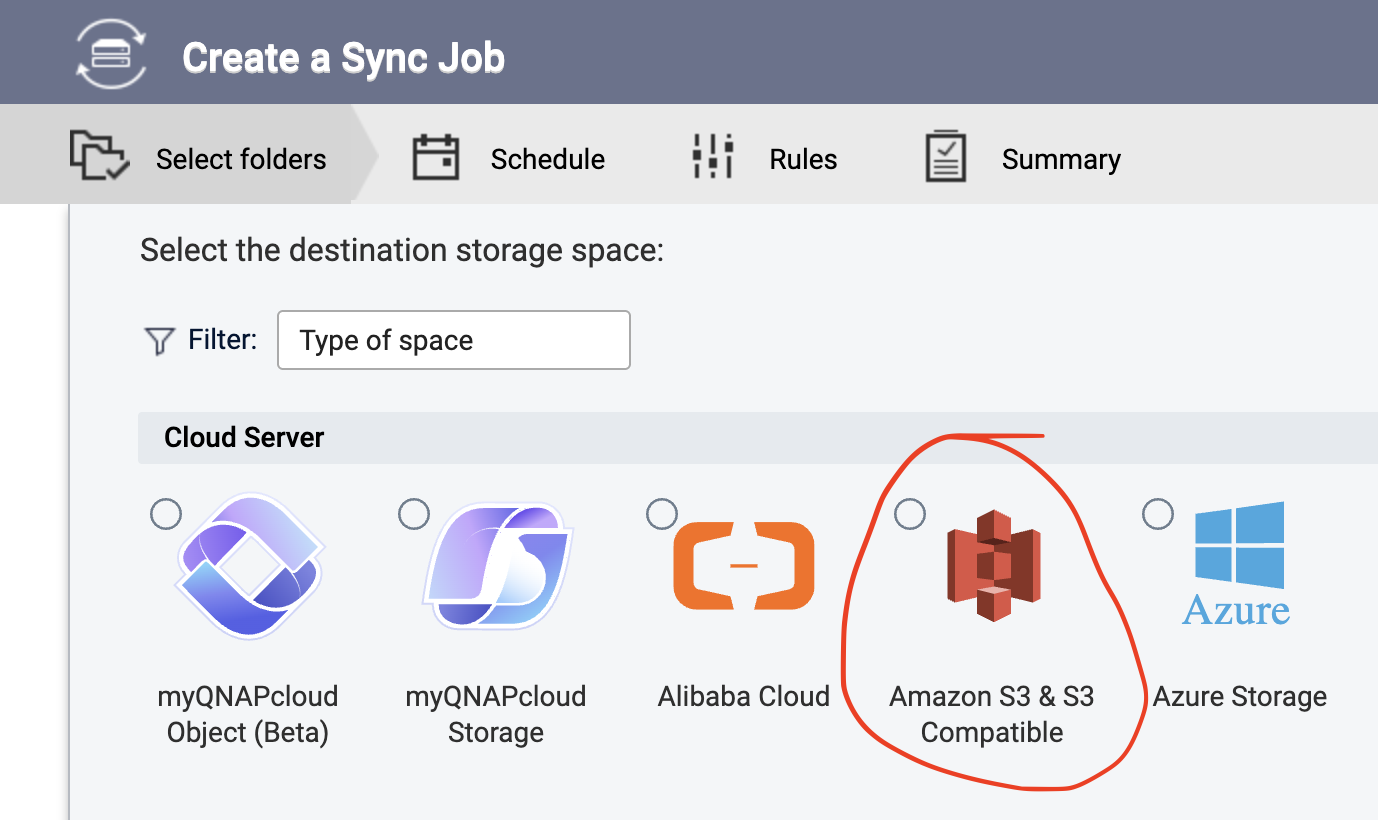
#QNAP NAS could sync data from S3-compatible object storage. This is a solution to #GlitchySocial's Mastodon media storage that I was searching for! I'll have a single-node #Garage server that will store objects on a 500GB 2.5" HDD I suddenly found in my stash. And my NAS will sync that data to itself for backups! Yeah, let's do this!
#homelab #selfhosting #selfhosted #selfhost #MastoAdmin #Mastodon
We released Mastodon v4.7.6, v4.6.12, v4.5.22 and v4.4.29.
These versions update Ruby to address multiple critical security issues. Regardless of how you run Mastodon, make sure to use Ruby 4.0.10, 3.4.13 or 3.3.14.
If you are using a nightly or 5.0.0-beta.1, update to nightly.2026-11-20-security. A proper beta 2 version will be released later today.
Full release notes and update instructions are available on the GitHub releases page.
 Mastodon Release Watcher » 🤖 🌐
@mstdn_release_watcher@mastodon.kodesumber.com
v4.7.6
This release is made primarily to update Ruby in our docker container images to fix multiple critical security issues. It is critical to update if you use our docker container images. If you are not using our docker container images, please make...

⚠️ Today's internet apocalypse means you should update the ruby (of your mastodon instance):
GLITCH-SOC Release Watcher » 🤖 🌐
@glitch_soc_release_watcher@mastodon.kodesumber.com
v4.6.12
This release is made primarily to update Ruby in our docker container images to fix multiple critical security issues. It is critical to update if you use our docker container images. If you are not using our docker container images, please make...
GLITCH-SOC Release Watcher » 🤖 🌐
@glitch_soc_release_watcher@mastodon.kodesumber.com
v4.5.22
WarningWhile we do our best to support Mastodon 4.5 until 2027-02-20, there are known security issues in some of the dependencies we use. We recommend administrators to update to a newer Mastodon version when they can, especially if you use...
GLITCH-SOC Release Watcher » 🤖 🌐
@glitch_soc_release_watcher@mastodon.kodesumber.com
v4.7.6
This release is made primarily to update Ruby in our docker container images to fix multiple critical security issues. It is critical to update if you use our docker container images. If you are not using our docker container images, please make...
 v4.7.6

RE: https://ruby.social/@mame/117640254153433278
Update your Ruby asap. This is really bad especially if it serves HTTP.
Updated Mastodon container images are coming soon.

Question for #Garage #zfs #sysadmin #FreeBSD #MastoAdmin peeps:
Our S3 MinIO replacement for #Mastodon is Garage. We can set a block size (default is 1M) that is much closer to average file size, let’s say we set it to 32k.
We can either add compression in Garage (the default) or at ZFS.
Questions:
- Which is better for compression? Garage managing the compression before writing the 32k blocks, or ZFS compressing the 32k block down to something else?
- Is there anything to tune on ZFS like setting g recordsize=32k to match block size?
Searching is not revealing anything useful. 🙏

Critical Nginx vulnerability:https://nginx2root.com/
Appears default Mastodon installations are affected because they enable HTTP2. Just fixed for bayes.club. (h/t @drwho)
#MastoAdmin #Nginx
Just in case, we dropped http2 from #mementomori for time being until nginx is fixed. Tell us if there are problems.
New research from ACM: The Everyday Work of Managing Misogyny Online: How Community Managers, Moderators and Administrators Govern Gendered Harms
This resource has some excellent guidance and actionable suggestions for moderators, community managers, administrators and platform developers.
https://www.australiancommunitymanagers.com.au/blog/report-managing-misogyny-online
#Moderation #FediMod #FediAdmin #MastoMod #MastoAdmin

Alt...
All respondents and interview subjects spoke to the lack of understanding of, and respect for, what moderation work actually involves as a compounding factor for the harms they experience and govern on behalf of others.
This extended across organisations and into public discourse. When moderation succeeds, its effects are often invisible: conflicts de-escalate before they become visible, harmful content is removed before members encounter it, and the space continues functioning without disruption.
This invisibility works against practitioners twofold: it leaves the labour underappreciated and under-respected, and it leaves policymakers and researchers focused on platform-level moderation decisions while overlooking the substantial governance work occurring behind the scenes.

Alt...
keyword filters and automated word blocking
removing content and behaviour that breaches guidelines
hiding content from general view without full removal
turning off comments on specific posts or threads to curb damage
account blocking and banning
reporting systems for clear policy breaches
Apparently, #HEIC support was broken in #Mastodon with the migration to #libvips, and the fix will arrive only with 5.0.0.
I was afraid the issue was exclusive to #GlitchySocial

RE: https://oldfriends.live/@hashtaggames/117634942560809896
Tonight's #MigrateAMovie #HashTagGames is inspired by hashtaggames.online ( @hashtaggames ) migrating to a new server. It is still migrating and should be back in the morning after it is done and I flip the switch back on for ActivityPub.
#MastoAdmin, please note, if the instance shows up in your logs or sidekiq as failing, it will resolve itself soon. It's taking a little bit longer to move from host to host with it being an ActivityPub WordPress instance. The Actors folder has so many federated user profiles and it is large.
Time For 9 o'clock #HashTagGames hosted by @paul
How to play: Write something awesome, Use the HashTag, Toot/Post and Repeat!
Tip: HashTagGames.Online's server is still in the process of migrating to a new server. Change titles, characters, plots, etc
There's no wrong way to play or interpret the game. Let's Play!


#DefCon.social is considering changing our rules around Automated Accounts, Bots, and inauthentic chatbot behavior. Looking for feedback:
- If your bot is phishing for engagement / bulk reposting news items and is NOT marked Automated we will SUSPEND it.
- If your bot is phishing for engagement / bulk reposting news items and IS marked as automated we will LIMIT it.
- If your bot is doing something useful, unique, interesting and is marked as Automated then all is good.
#MastoAdmin #Moderation

False Flag! 🙄
kinkycats.org
Adult content: Yes. ✅
Illegal content: No. 🚫
I've been going over the many FediBlock posts, and about 30% of the things people claim we should all supposedly block are just drama.
User1 doesn't like User2 and claims they're the devil or something along those lines. Or they claim User2's site is filled with horrible things because, once again, they dislike User2, who happens to be the admin/mod.
I knew that since the content was considered "adult content," most people would likely take the report at face value and move on without investigating.
But, as some people know, I work for Meta, and I've seen far worse things than most of you will ever imagine. So, it really doesn't faze me to register a random account and see for myself.
I used the account @After_Dark and went back over a week (8 days) through their local timeline. Then I decided to double-check the admin's account, too, just to be sure.
> "What did I find?"
18+ content ranging from straight to gay to bi, along with a wide variety of kinks.
> "What did I NOT find?"
Anything illegal. Everything appeared to involve adults (18+). There was no loli content, no animal abuse content, or anything else that would automatically warrant a FediBlock.
#FediBlock #MastoAdmin #FediAdmin #Abuse #FalseFlag #FlaseFlags
I don't think people are aware of how bad the AI bots have become on Mastodon in the last weeks. I would estimate that, out of 200 signup attempts, 199 are bots now. They are still mostly recognizable, thus blockable, but it's not getting better. #mastoadmin

If you use a temporary email address to sign up for phpc.social, don't; we'll be blocking new account creation requests from those email domains before they even reach a moderator starting soon. We have a wave of bots using these to (attempt to) sign up and it's not a good use of mods' time to look through LLM-generated sign up reasons for the needle in a haystack that is a legitimate account.
If you're another Mastodon admin, DM me for a patch for making this blocking easier. #mastoAdmin

Save as a CSV file, for example, block.csv, import (upload) the file, and merge it with your current block list.
This post should be self-explanatory, but for a more exhaustive outline, see: https://mivatter.com/notes/ary14ll86y
#Spam #Spammer #Scam #Scammer #Fraud #FediBlock #FediAdmin #MastoAdmin #Mastodon #Misskey #Fediverse #ActivityPub #IsraelVerified #GazaVerified
1,654 accounts identified as participating in spam and scam activity — along with accounts that actively promote, defend, or amplify them.
Save as a CSV file, for example, block.csv, import (upload) the file, and merge it with your current block list.
This post should be self-explanatory, but for a more exhaustive outline, see: https://fairy.id/@Linux/117385319051532229
#Spam #Spammer #Scam #Scammer #Fraud #FediBlock #FediAdmin #MastoAdmin #Mastodon #Misskey #Fediverse #ActivityPub #IsraelVerified #GazaVerified
Ok, I’ve now completely blocked all signups from Cloudflare IP addresses on kamloops.social.
Hopefully this puts a stop to all the bots attempting to create accounts on the instance.
Rejecting all these fake accounts is becoming tiresome. 🤨

We are also seeing this. Other domains we've blocked recently include:
onionmail.com
onionmail.org
emltmp.com
sentence.com
2mail.co
2mail.eu
We also have seen a lot of Proton spam signups.
@smattymatty https://socialontario.ca/@smattymatty/117617429787153150

AI agents are signing up to Mastodon instances with @agent.qq.com emails. That domain is Agently Mail, a Tencent service that gives AI agents their own mailbox.
One applied to socialontario.ca today with a polite generic join reason I almost fell for ("a calm corner of the fediverse to share notes about everyday life, books and small projects") and a Hong Kong datacenter IP
I blocked the email domain. Fellow admins may want to check their pending signups for it.

 Shlee is a nervious bean &
#mastoadmin reminder - @postgresql has released a security focused set of releases (52 vulnerabilities and over 140 bugs).
This is the final release of PostgreSQL 14. PostgreSQL 14 is now end-of-life and will no longer receive security and bug fixes.
(I suspect that mastodon will upgrade the docker compose from PG14 to PG19 once it's released next week to prepare for the upcoming 5.0.0 release)
https://www.postgresql.org/about/news/postgresql-187-1712-1616-1520-1425-and-19-rc-2-released-3442/

🇬🇧 STRENGTHENING ACCOUNT MANAGEMENT
In summary:
- Automated assistance for moderators to filter out fake sign-up requests,
- Automated cleanup of ghost accounts,
- Automated deletion of accounts inactive for > 3 years after reminder emails.
Our policies have been updated to reflect these changes!
Fake accounts and bots are a plague. Across the Fediverse—and on Mastodon in particular—we regularly face waves of suspicious sign-ups, yet we are poorly equipped and lack the right tools to deal with them.
We already use Anubis to filter out bots, but that isn't enough.
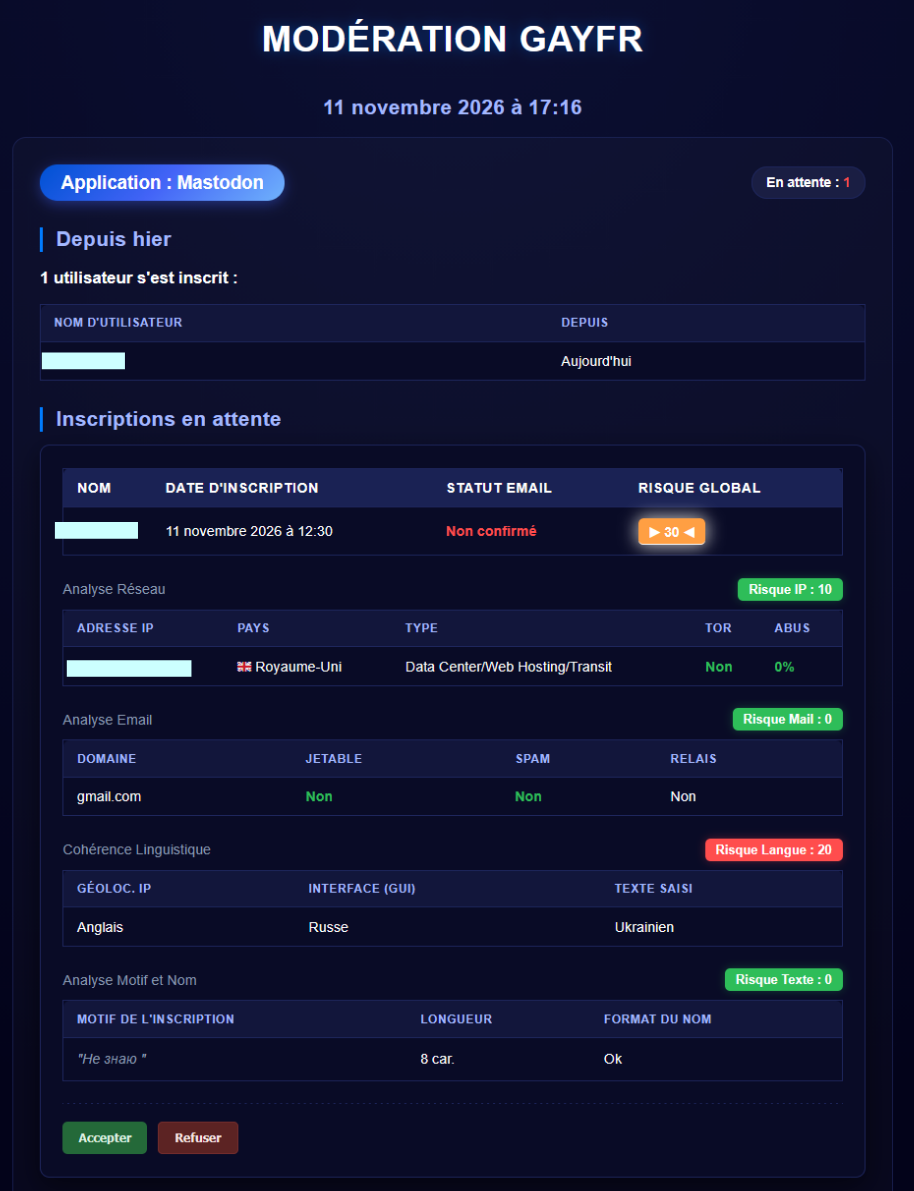
That’s why I built a simple decision-support tool for our moderators: a single web page summarizing all pending sign-up requests. For each request, it provides a risk score based on IP address reputation, email domain risk, language consistency, and a few other indicators. Moderators can review all of this information and approve or reject requests directly from the same page.
This dashboard is now live for Mastodon, and I will gradually add all our other Fediverse applications whenever their APIs allow it.
However, some fake accounts still slip through—or already have. For instance, we see "ghost accounts" that, once registered, have zero activity, no profile information, nothing at all. My tool will now handle them and automatically delete them after one month if they remain inactive. One might think these accounts are harmless, yet they skew our statistics and pose a dormant threat if they turn out to be bots waiting to wake up all at once.
On our instance, roughly 20% of accounts are ghost accounts. Just imagine: the situation is almost certainly the same on other servers, which adds up to a massive number of accounts overall...
Finally, there are accounts that have been abandoned or inactive for three years. These users will receive three reminder emails prompting them to log back in to avoid automatic account deletion. It might serve as a friendly nudge to come back and check us out. Otherwise, this cleanup is good digital hygiene that also supports privacy protection and GDPR compliance.
We have roughly the same percentage of abandoned accounts. Here too, the same likely holds true for most other servers.
For the time being, account deletions are running in dry-run mode, but they will go live in the coming weeks. We want to make sure the system doesn't get carried away, especially since there are a few subtleties in the data returned by Mastodon’s APIs. Be careful if you plan to go down the same path!
These measures will lower our total account count, but they will improve platform hygiene and security for everyone's benefit. I wish all servers would do the same—it would make the Fediverse much more resilient.
I’ll consider open-sourcing the project if there’s interest. In the meantime, here is an (anonymized) screenshot of the moderation dashboard.
Alt...
Screenshot of our new tool to assist moderator decision-making for registration requests.
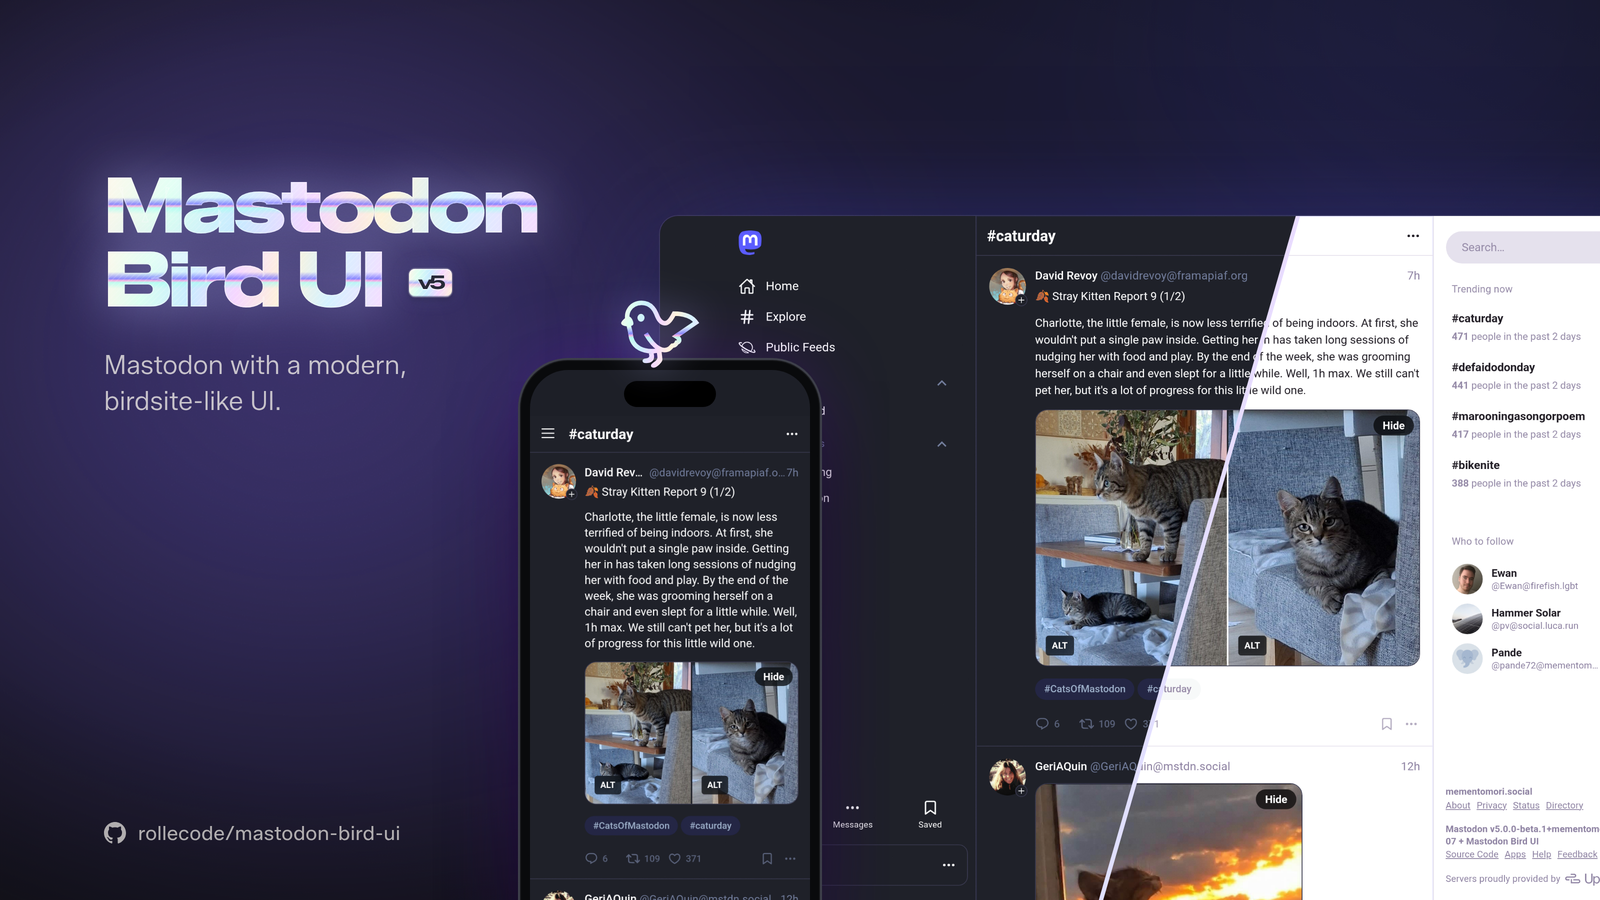
🐦⬛ Mastodon Bird UI 5.0.0-beta.1-2026-11-08 (nightly) is out. This is Bird UI rebuilt for Mastodon 5, the new 5.0 design that is now in beta.
The nightly follows Mastodon 5.0.0-beta.1. If you are on Mastodon 4, stay on 4.7.3-2026-10-11 from the main branch.
New:
- Rewritten from scratch for the Mastodon 5 design
- Micro-interactions, likes and boosts are whimsical
- Notifications, content warnings, link cards and thread lines look like they did on Mastodon 4
- Follows Mastodon's own light, dark and high contrast settings
- A darker, blurred backdrop behind the composer and every popup
- A new install script for Mastodon 5, or paste dist/mastodon-bird-ui.css into Custom CSS
- The star favorite, light and language variants are no longer supported
You can see it live at https://mementomori.social.
Release notes and full changelog: https://github.com/rollecode/mastodon-bird-ui/releases/tag/5.0.0-beta.1-2026-11-08
#MastodonBirdUI #BirdUI #Mastodon #MastoAdmin
Alt...
Mastodon Bird UI v5 screenshot
Lots of nightly updates coming in today!
Most notable bugs:
- When you type a hashtag or at-person, the popout gets in the way
- Ultra Accessible themes for vision impaired have some font size issues
- Some hover states and element proportions, especially padding, have regressions from v5 and the new nightly theme
- Bugs in the advanced view
The latest changes are in the nightly branch, and work is still in progress. You can follow my work here: https://github.com/rollecode/mastodon-bird-ui/tree/nightly
Some of these are core issues and will probably be fixed or changed in Mastodon v5 stable. If not, fixes will go live in our fork.
#MastodonBirdUI #BirdUI #CSS #MastoAdmin #UI #Mastodon #OpenSource
Released 5.0.0-beta.1-2026-11-09 of Mastodon Bird UI: https://github.com/rollecode/mastodon-bird-ui/releases/tag/5.0.0-beta.1-2026-11-09

 [
RE: https://mastodon.social/@pixelfed/117586194168536723
Mastodon Canada just committed to the Digital Platform of Rights and Freedoms with the following:
"Mastodon Canada recognizes the importance of Data Sovereignty and, with this hosting, keeps our community's data on servers in Edmonton, Alberta, that we can physically touch.
We are committed to the Mastodon Covenant and provide safeguards that respect the Canadian Charter of Rights and Freedoms. We are transparent with moderation and administration decisions and remain responsive to cybersecurity events.
We are steadfast in our commitment to working with Project Arachnid in combating CSAM on the fediverse.
Our team actively seeks out equity-seeking members to join our moderation and oversight team and looks forward to continuing to build upon this."
I'm sure it'll be published shortly here: https://respectfulplatforms.org/
#mstdnca #fediverse #mastoadmin #mastodon
We, the architects and stewards of digital platforms, recognize the fundamental rights of all users to participate in online spaces that respect their privacy, dignity, and well-being.
https://respectfulplatforms.org
#RespectfulPlatforms #SocialWeb #DigitalPlatformCharterOfRights
If you're running a public Mastodon server, it's really important that you have a plan for closing down gracefully *even if you have no intention of closing down*.
Having a plan in place means your members don't have to worry about your server suddenly disappearing, as they know they will get plenty of warning if it happens.
Here's a step-by-step guide to closing a Mastodon server gracefully (and much of this applies to any Fedi server):
🏡 https://fedi.tips/closing-your-mastodon-server-gracefully/