Search results for tag #selfhosting
Hallo Mastodon! Das hier ist Wachhund, der Wächter für deine Linux-Server: Jede Nacht ein Rundgang mit über 40 Prüfungen, gemeldet wird, was nicht stimmt. Kostenlos für bis zu 10 Server.
Hier erklären wir jeden Montag eine Sache rund um Serversicherheit, in drei Schritten und in klarem Deutsch. Los geht es am 16. November mit der Frage: Warum Schlüssel statt Passwort?
#neuhier #Serversicherheit #Linux #Sysadmin #Selfhosting #Homelab
Alt...
Titelkarte: Das ist Wachhund. Der Wächter für deine Server. Ab jetzt erklären wir hier jede Woche eine Sache.
Alt...
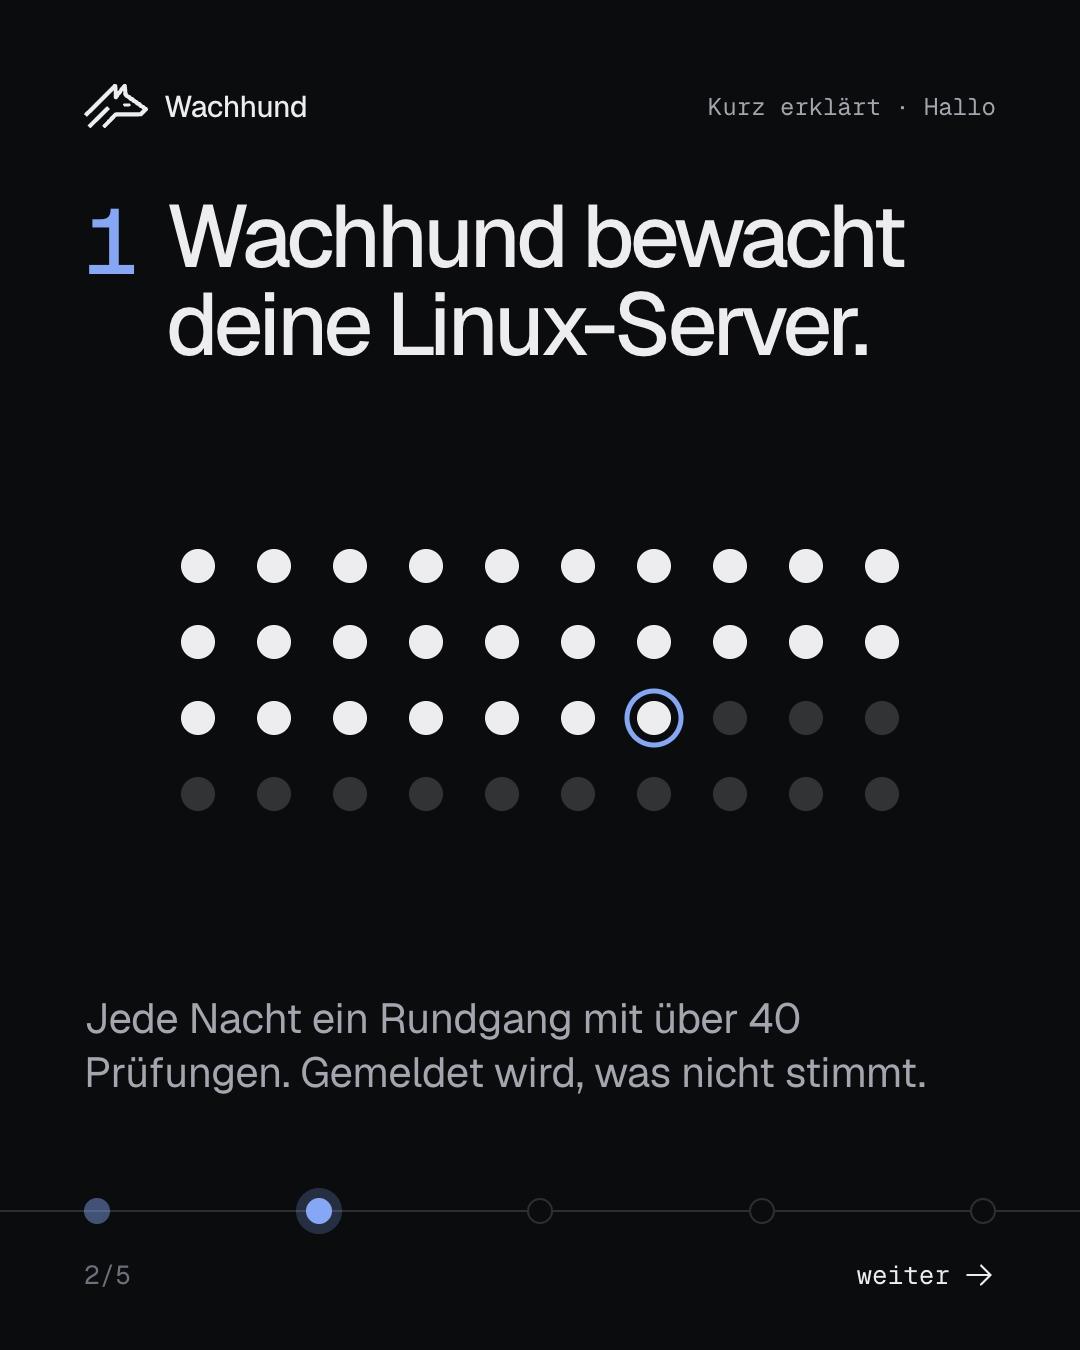
Karte 1: Wachhund bewacht deine Linux-Server. Jede Nacht ein Rundgang mit über 40 Prüfungen. Gemeldet wird, was nicht stimmt. Grafik: Ein Raster aus 40 Punkten, 27 davon sind schon abgehakt, einer wird gerade geprüft.
Alt...
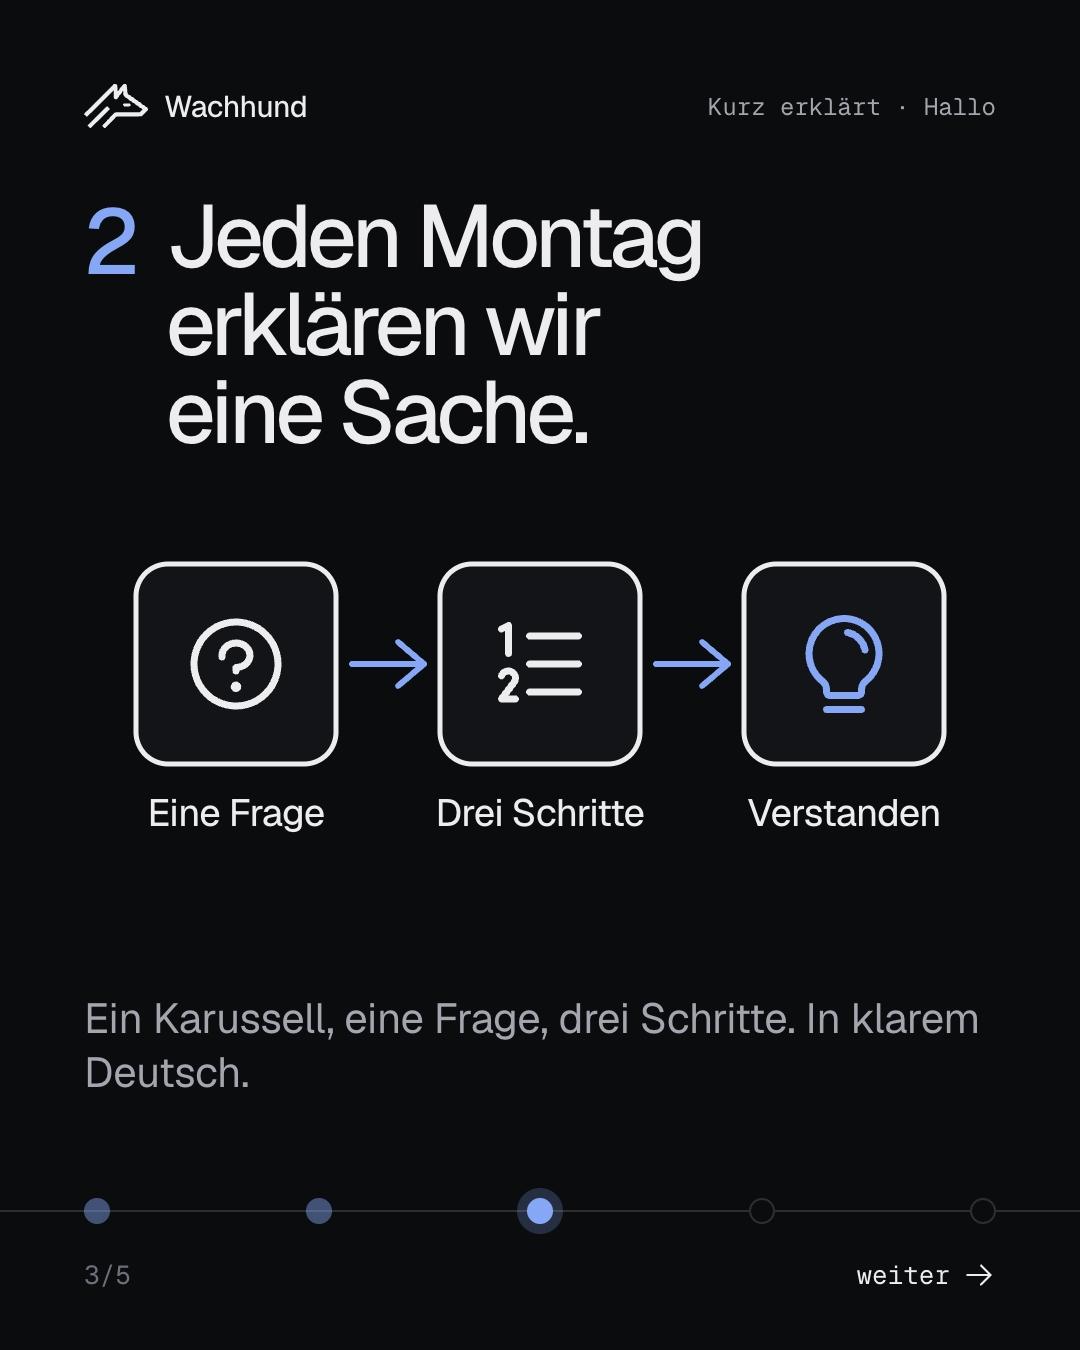
Karte 2: Jeden Montag erklären wir eine Sache. Ein Karussell, eine Frage, drei Schritte. In klarem Deutsch. Grafik: Drei Stationen mit Pfeilen: eine Frage, drei Schritte, verstanden.
Alt...
Karte 3: Es geht um Serversicherheit. SSH-Schlüssel, Firewall, Updates, Backups. Und darum, was Wachhund selbst macht. Grafik: Liste mit vier Themen: SSH und Zugänge, Firewall und Ports, Updates und Backups, Einbruchsspuren erkennen.
Ein Befehl für deinen Server: sudo ss -tlnp
Er zeigt, welche Programme auf Verbindungen warten. 127.0.0.1 heißt nur von innen, 0.0.0.0 heißt alle Adressen, auch die öffentliche. Den Rest regelt die Firewall.
Was stand bei dir, womit du nicht gerechnet hast?
Wachhund lernt, welche Ports bei dir lauschen, und trägt neue in die Bestandsaufnahme ein: https://wachhund.io

🚀 shlinker.app is online!
The website is available, German and English are at the start – and the first visitors are already there.
Once knocked on Google, Bing said, and already half the crawler Internet is at the door. After all.
Let's take a look:
https://shlinker.app
#Shlinker #Webdev #SelfHosting #IndieWeb #BuildInPublic #shlink #opensource

A new build of littleFedi (2026.11.16) is out!
The Little Computer People have been busy, and we're happy to share a new release of littleFedi!
Before reading the long changelog, there's something important we'd like you to know about upgrading.
⚠️ Important: Upgrading littleFedi
This release includes database migrations that run automatically on the first startup. Some of them may take a while, especially on larger databases or slower hardware.
Please read these instructions carefully before upgrading.
-
Stop littleFedi and make a backup.
Back up your database, configuration, and media files. Remember to save any encryption keys stored in the service environment, too.
See
docs/backup-restore.mdfor backup and restore instructions. -
Replace the binary.
Download the new binary for your operating system, CPU architecture, and database/media backend. Replace the old binary and start littleFedi using your existing configuration.
No separate migration command is needed.
-
Allow the database migrations to finish.
littleFedi will automatically perform the necessary migrations on its first startup. One of these rebuilds SQLite indexes and may take considerable time on large databases, particularly when running from an SD card.
Make sure your service manager allows enough time for startup.
Do not stop or restart littleFedi while migrations are running.
-
Check that everything is ready.
Wait for startup to complete, then check the logs and the
/readyzendpoint before using your instance.Subsequent startups will skip migrations that have already completed.
Need to roll back?
Stop littleFedi and restore your pre-upgrade backup before starting the previous binary.
Never run an older binary against a migrated database.
What's new?
As with previous releases, many of the changes come directly from the people who make this project worthwhile: our friends on this instance, those who have started self-hosting littleFedi, and everyone who has taken the time to test, report bugs, suggest improvements, or review our code.
We've continued working on the things that matter to us: keeping littleFedi lightweight, efficient, reliable, and enjoyable to use, without unnecessary complexity.
And yes, we're still very much committed to making the Fediverse accessible even to the smallest computers!
Here's what's changed in this release:
Changelog
-
Account blocks now hide posts in profiles, search, threads, quotes and
streaming, and stop new follows, mentions, replies, favourites, reactions,
poll votes, boosts and direct messages in both directions. Blocked profiles
keep only the account's identity and block/report actions. Existing direct
conversations stay readable, and email and push notifications check for
blocks before sending. Other accounts on the same server remain reachable,
even when they share an inbox. Public posts remain available to anonymous
readers and other instances.
-
Static blog pages now leave out unlisted replies. Only replies with public
visibility are included. Rebuild existing blogs after upgrading to remove
unlisted replies from pages generated by earlier versions.
-
Content warnings now display apostrophes and other HTML entities correctly
in posts and notifications, instead of showing codes such as
'. -
Source builds now require Go 1.27.4. Updated the Go dependencies, bundled
Alpine.js and htmx, and the security tools used in CI. Rebuild existing
binaries to pick up the Go security fixes.
-
With
housekeeping.max_delete_per_run = 0, status pruning now keepsgoing in batches of 500 until no eligible posts remain. Previously, remote
pruning stopped after 500 posts and local pruning after 500 per account.
Positive limits still apply across local and remote posts. Failed deletions
are left for the next run rather than retried in a loop.
-
The inbox no longer fetches a key for an unknown actor's self-delete.
Requests with a Signature header are acknowledged with
202and droppedwhen the actor and deleted object are the same URI and the account is absent
locally. Domain blocks still apply; deletes of known accounts and posts
still need authentication.
-
Incoming HTTP signatures now have their timestamps and body digests checked
before fetching a public key or verifying the signature. Stale requests and
damaged bodies can be rejected without a network request.
-
Public instance counts on
/aboutand the v1/v2 instance APIs are cachedfor 30 seconds, instead of counting the database on every request. The
admin dashboard still reads fresh counts.
-
SQLite reply and quote indexes now leave out NULL entries. This reduces
their size and avoids a slow query plan when loading RSS feeds. Migration
007 rebuilds all four indexes at startup and can be slow on large databases,
especially on SD cards. Allow extra time for the first startup after
upgrading; later starts skip the migration.
-
The interface is now available in Catalan, thanks to Jolupa, who
translated it. It can be picked in the settings like the other languages,
and Catalan is also in the list of languages a post can be tagged with.
Strings added after the translation was made were filled in afterwards and
are the ones most worth a second look.
-
Boosts can be scheduled, to spread them out instead of filling followers'
timelines all at once. Hold the boost button for half a second, or open the
post, and pick a time under "Boost later". A quick press still boosts right
away. Scheduled boosts show up on the Scheduled page next to scheduled
posts and can be moved or cancelled there. If the post is deleted or
becomes impossible to boost before then, the boost is dropped. Mastodon
apps have no notion of a scheduled boost, so the API leaves them out.
-
Scheduled posts can now be edited, not just moved to another time. The
Edit button on the Scheduled page opens the post in the composer with
everything it had, including the time, and saving puts it back on the
schedule. Before, the only way was to cancel it and write it again. A post
that is already being published can no longer be edited.
-
Posts can be saved as drafts. The composer has a "Save draft" button next
to Post, and the new Drafts page lists them, newest first. Opening one
brings back the text, content warning, audience, language, attachments,
poll and expiry, and the post it replies to or quotes. Posting or
scheduling a draft removes it. Everything is a plain form, so it works
without JavaScript and in text browsers. Drafts live on the server and are
not shared with Mastodon apps, which have no API for them.
-
The image viewer can now move between the pictures of a post. Use the
arrows on screen, the left and right keys, or swipe on a phone. Before, each
picture had to be closed and the next one opened by hand. Without
JavaScript nothing changes: each picture still opens on its own.
-
In French the image viewer had no name for screen readers. The apostrophe
in "Visionneuse d'images" broke the expression that sets it. Translated
labels are now read from data attributes, so quotes in a translation can no
longer break the script.
-
The Roost theme works better on phones. Post actions fit on one row, the
back link is a flat row instead of a pill against the screen edge, the
profile banner and avatar no longer fill the first screen, and the bottom
bar marks the current page without a filled block.
-
Unread mentions and direct messages now stand out from the other unread
notifications. In Roost the mention colour was the same blue as the unread
mark, and in every theme their rows took the same background as any unread
row. Herd and Ink also get mention colours further from their accent.
-
Filters set to warn now work on the catch-up page. The filtered posts were
shown in full, without the filter notice. Filters set to hide already
worked there.
-
Direct message notifications have a magenta edge, an envelope icon and their
own label, so they stand apart from public mentions.
-
Boosts from a followed account can now be hidden from the home timeline,
with the "Hide boosts" button on their profile or the matching switch in
Mastodon clients. Their own posts still show up. Boosts already in the
timeline go away too, and come back if boosts are shown again. The
reblogsparameter of the follow API was accepted but ignored until now. -
Push delivery now follows up to three 307/308 redirects within the same
HTTPS origin. The Mastodon app relay redirects endpoints without a trailing
slash; those pushes previously failed after all retries.
-
Pushes for favourites, boosts and federated mentions now carry
notification_id. Those jobs were built before the notification was stored,so the ID was missing, and the official iOS app showed only the relay's
placeholder trumpet instead of the notification.
-
The bookmark button on boosted posts now stays in sync after refreshing
the home timeline. Before, it could appear inactive while the post was still
bookmarked, and clicking it again removed the bookmark.
-
Replies no longer show the previous post as unavailable after it has been
downloaded. Refreshing or reopening the reply now keeps the correct reply
target in timelines, boosted posts and Mastodon clients. The open thread
page also updates its reply label as earlier posts arrive.
-
Redrew the quote icon. The old one, two squared-off hooks side by side,
could be read as "SS". It now looks like a pair of quotation marks.
-
Logging in with toot from the command line now works. toot opens
/oauth/authorize/with a trailing slash, which returned 404. URLs with atrailing slash are now routed like the ones without, as on Mastodon.
-
With
require_approvalon, new accounts were created already approved: theycould sign in at once and never showed up in the approval queue. They now
wait for an administrator. Accounts registered while the bug was present
stay approved; check recent signups if the setting is on.
-
Filter keywords created from a Mastodon client with
whole_wordturned offwere saved with it on. Leaving
whole_wordout still means on, as inMastodon.
-
Mastodon apps no longer show littleFedi's own notification types (follow
accepted, unfollows, blocks, emoji reactions, blog rebuilds and others) as
broken entries, and their unread badge no longer counts them. A client can
still ask for them with
types[], which the notification endpoints nowhonour.
exclude_types[]=pleroma:emoji_reactionnow works too. -
The
user:notificationstream carries only notifications. Before, it alsosent home timeline posts, which some clients (Tuba) showed as empty
notifications.
-
The instance documents report
image_matrix_limitas a pixel count, takenfrom
max_image_pixelsandmax_image_dimension. It was 4096, which clientsread as 4096 pixels in total and used to shrink uploads to a thumbnail. The
video limits Mastodon's iOS app requires are there too.
-
New client API endpoints:
GET /api/v1/accounts?id[]=,
/api/v1/accounts/lookup,/api/v1/accounts/familiar_followersand
/api/v1/notifications/policy. Mastodon for iOS and Tuba call them. -
Push notifications now reach the Mastodon apps (Mastodon for Android and
iOS, Tusky, Ice Cubes, Ivory, Mona). Apps that don't ask for
standard: trueget the olderaesgcmencoding, which is the only oneseveral of them can decrypt, and every push now carries the access token
and a numeric notification ID, without which the apps drop it. Form encoded
subscriptions are accepted, and the subscription ID is a number as the apps
expect. Subscriptions made before this release keep the old behaviour:
turn notifications off and on again in the app, or sign in again.
-
Polls no longer break Mastodon for iOS and Android.
own_votesandemojisare always lists, and
expires_atuses Mastodon's date format. -
Deleting a post from an app returns the deleted post with its source
text,so "delete and redraft" keeps the text. Deleting it twice returns 404.
-
Timeline paging:
min_idreturns the page right after the cursor instead ofjumping to the newest posts, which made apps skip everything in between when
filling a gap. A cursor pointing at a deleted post keeps working, and an
unknown
max_idreturns an empty page instead of the top of the timeline.
min_idandsince_idwork for notifications too. -
Linkheaders are now absolute URLs and keep the other query parameters.Followers, following, blocks, mutes, favourites, bookmarks, lists and list
members send them too, so apps can load more than the first page.
-
Media sizes are reported under
meta.originalas well, and remote mediakeep their blurhash and size. Apps used them to lay out images before they
load.
-
Accounts without an avatar or header point to a placeholder image instead of
an address that returned 404. Accounts also report
uriand
hide_collections, and relationshipsrequested_byandlanguages. -
The default post visibility and language set in the profile are reported to
apps and used when an app leaves them out.
-
/api/v2/instancereports the VAPID key underconfiguration.vapidand
translation.enabled. Mastodon for iOS reads both. -
Loading images, avatars and emoji no longer counts against the rate limit.
Scrolling a busy timeline could hit it, and every API call after that failed.
An API request over the limit now gets a JSON error with
Retry-After, andunknown API routes return JSON 404 and 405 errors instead of HTML.
-
littleFedi now logs a warning when requests come from a local reverse proxy
that is not listed in
http.trusted_proxies. In that case every visitorshares the proxy's rate limit.
-
CORS preflight allows the headers the browser asks for (
Idempotency-Keyamong them) and exposes
LinkandRetry-Afterto web clients. -
Idempotency-Keyis honoured when posting: a retried request returns thepost created the first time instead of a duplicate.
-
Tokens from
client_credentials(the app's own token, before a user signsin) are treated as anonymous on public endpoints instead of being refused.
-
Filters:
keywords_attributesworks when creating and editing a filter, inJSON and form encoding, and the
/api/v2/filters/:id/keywordsand
/api/v2/filters/keywords/:idendpoints are new. -
New endpoints:
GET /api/v1/accounts/search,
/api/v1/statuses/:id/history,/api/v1/timelines/directand
/api/v2/notifications/unread_count. -
The streaming API accepts the token in
Sec-WebSocket-Protocol, as theMastodon web client sends it, and tokens limited to
read:statusesand
read:notifications. -
The "Clear all" button on the notifications page is now called "Delete
all", in every language, since that is what it does.
-
Profile fields: up to four label and value rows on your profile, edited in
Settings or from any Mastodon app, and shown under the bio on the profile
page. They are sent to other servers like Mastodon's, and the ones remote
accounts publish are now shown on their profiles. Remote accounts already
known get theirs the next time their profile is fetched again. Links work;
verified_atis always empty, as littleFedi does not checkrel="me"links.
-
Apps can mute a conversation (
POST /api/v1/statuses/:id/muteand
/unmute). Mentions, likes, boosts, quotes, edits and reactions in thatthread stop notifying you.
-
Apps can keep a private note on an account
(
POST /api/v1/accounts/:id/note). Only you see it. -
Followers can be removed from an app
(
POST /api/v1/accounts/:id/remove_from_followers). A remote follower'sserver gets a Reject of the follow, as from Mastodon.
-
Conversations can be removed from the list from an app
(
DELETE /api/v1/conversations/:id); a new message brings them back.
POST /api/v1/conversations/:id/readworks too. -
Saving the profile from an app with an empty bio or display name now clears
it. Before, empty values were ignored and the old text stayed. The default
post visibility and language set in an app are saved too.
-
MastoBlaster could not read its push subscription: the
alertsobject hadno
updatekey. It is now there, and apps can turn on pushes for editedposts. Renaming a list and changing push alerts from MastoBlaster failed
with 405, because it sends
PATCH; both endpoints now takePATCHas wellas
PUT, like Mastodon. -
Three database migrations run at startup. One adds the
standardand
access_tokencolumns topush_subscriptions. One adds
accounts.fields_jsonand thethread_mutes,account_notesand
hidden_conversationstables. The last adds
push_subscriptions.notify_update. All of them only add, nothing existingis changed, and all can be rolled back.
A big thank you to everyone who has been following this little adventure, testing new builds, sharing feedback, and helping us improve.
littleFedi is still a young project, and there's plenty more to do. But every release brings us a little closer to what we've wanted from the beginning: a federated social platform that's simple to run, easy to maintain, and doesn't require a powerful server just to participate in the Fediverse.
Small computers deserve a place in the Fediverse, too. ❤️
Happy upgrading, happy self-hosting, and stay tuned!
The Little Computer People
#littleFedi #Fediverse #SelfHosting #OpenSource OwnYourData

Rebuilding a server... this is the first time ever that I have considered using something other than #Debian ...
What cloud service did you recently kick to the curb and replace with something on your own hardware? And how long did it actually take to set up? #dataownership #selfhosting #privacy #homelab

@steffen Diesen Beitrag von Steffen möchte ich sehr gern noch einmal weitertragen – auch, weil das Thema digitale Souveränität für uns keine neue Modeerscheinung ist, sondern seit vielen Jahren gelebte Praxis.
Seit Ende 2003 betreiben wir eigene Server und haben uns immer bemüht, möglichst viel selbst zu verstehen, selbst einzurichten und selbst administrieren zu können. Nicht, weil immer alles selbst gemacht werden muss – sondern weil es einen großen Unterschied macht, bewusst entscheiden zu können, welche Technik, welche Dienste und welche Abhängigkeiten man akzeptiert.
Gerade heute, wo digitale Souveränität, Open Source und technologische Abhängigkeiten immer stärker diskutiert werden, finde ich diesen Gedanken wichtiger denn je.
Und vielleicht passt er auch ganz gut zum Fediverse:
Selbstbestimmung entsteht nicht dadurch, dass man keinerlei Infrastruktur nutzt – sondern dadurch, dass man versteht, worauf man sich verlässt und welche Alternativen man hat.
#DigitaleSouveränität #OpenSource #Linux #SelfHosting #Fediverse #Systemadministration
RE: friendica-deutschland.de/objec…
Digitale Souveränität – wir praktizieren sie seit 2003.
Während heute vielerorts darüber diskutiert wird, wie sich digitale Abhängigkeiten verringern lassen, betreiben wir bereits seit Ende 2003 eigene dedizierte Server.
Wir installieren, konfigurieren, administrieren und sichern unsere Systeme vollständig selbst. Dabei setzen wir auf Linux, freie Software und unsere langjährige praktische Erfahrung.
Auch unsere Hardware könnten wir selbst zusammenstellen. Dass wir heute fertige Geräte und die Infrastruktur von Hetzner nutzen, ist eine bewusste Entscheidung.
Unsere Unabhängigkeit beruht jedoch auf einem noch grundsätzlicheren Gedanken:
„Alles, was wir benötigen, richten wir für uns selbst ein. Fehlt uns dafür das notwendige Wissen, versuchen wir, es uns anzueignen. Gelingt uns das nicht, verzichten wir lieber darauf, gehen schwierigere Umwege oder lassen es ganz.“
Denn wer auf eine bestimmte Technologie oder Dienstleistung nicht mehr verzichten kann, verliert einen Teil seiner Entscheidungsfreiheit.
Was das für unsere tägliche Arbeit und die IT-Strukturen unserer Kunden bedeutet, beschreiben wir in unserem neuen Artikel:
Digitale Souveränität – für uns seit 2003 gelebte Praxis
#DigitaleSouveränität #Linux #OpenSource #Systemadministration #SelfHosting

Unraid 7.4.0 bringt mehr Kontrolle über Docker und Dateitransfers
https://linuxnews.de/unraid-7-4-0-bringt-mehr-kontrolle-ueber-docker-und-dateitransfers/ #unraid #docker #selfhosting #linux #linuxnews

Hallo #Fediverse, ich bin es, der ibims. ☺️👋
Meinereiner ist #neuhier auf dieser Instanz und möchte sich kurz vorstellen. Bin schon etwas länger in der Fediverse unterwegs, also nicht gaaanz so neu im Fediverse.
Diese Profil ist mein neues, da ich von meiner alten Instanz auf diese umgezogen bin. Mein altes Profil war dieses hier: social.ddns.wtf/profile/ibims
Bin auf der Suche nach neuen und interessanten Kontakten, mit denen man sich nett austauschen, plaudern, lachen kann. Ab und an kann es aber gerne auch ein etwas ernsterer bzw. tiefgehender Gedankenaustausch sein
Interessen habe ich viele. Hier mal ein paar Dinge, die mich interessieren:
Da ich ein Genießer bin, stehe ich auf so Leckereien, die vom #Grill bzw. #BBQ kommen. Dazu darf es auch gerne einen guten Wein oder Whiskey geben. 🥩🌽🍷
Ich nutze gerne #Linux und interessiere mich für #FOSS / #FLOSS sprich #FreieSoftware, #Opensource. Generell bin ich der Meinung, dass wir uns von den Zwängen der großen Softwaregiganten befreien sollten. Somit ist mir auch die #Datensouveränität wichtig. Deswegen auch #UnplugTrump.
Ein weiteres Thema, das mich begeistert, ist #Selfhosting. So habe ich ein kleines #Homelab daheim, mit dem ich gerne diverse Dinge teste. 🖥️
Ansonsten stehe ich auch auf #Fußball, #Mountainbiken und #Wandern. Und überhaupt #Natur, in der ich mich gerne aufhalte und gut den Kopf freibekomme. Ach ja, und auf so süße, kleine Fellwesen fahre ich auch total ab. 🏔🚵🐿😽️
Wer also neugierig ist und mehr wissen möchte, kann mich gerne anquatschen. Ich beiße nicht. Gaaaaaanz bestimmt nicht. 😋
Location: Fediverse


Moose 0.8.0: Web search and calculations join your chats, OpenRouter joins the provider list, and finding a model gets easier:
https://moooossee.github.io/news/moose-0-8-0/
(Decent timing over there, web search being added was actually a huge deal for me moving to local AI, really great that there's an easy way to achieve it now)
Moose 0.8.5: Create reports, spreadsheets and presentations in your chats, find them in Files and keep copies when you export a conversation:
https://moooossee.github.io/news/moose-0-8-5/
Strata 0.2.13: Strix Halo Launch Fix and Qwen4 Prep for the 125B Consumer-PC LLM Engine:
https://www.linuxcompatible.org/story/strata-0213-strix-halo-launch-fix-and-qwen4-prep-for-the-125b-consumerpc-llm-engine/
Cloudflare Open Sources Kitesurf: Their Web Browser For AI Agents:
https://www.phoronix.com/news/Cloudflare-Kitesurf-Open-Source
Agent Name Service is Now Part of The Linux Foundation:
https://itsfoss.com/news/ans-joins-linux-foundation/
SuperPoD OS and Agentic Infra Take Center Stage at openEuler Summit 2026:
https://itsfoss.com/news/openeuler-summit-2026/
Linkwarden 2.17 rolls out custom link ordering, faster list rendering & other enhancements:
https://alternativeto.net/news/2026/11/linkwarden-2-17-rolls-out-custom-link-ordering-faster-list-rendering-and-other-enhancements/
Wireshark 5.0.0rc2 Released: New Theme System, HTTP/3, and Process Tracking:
https://www.linuxcompatible.org/story/wireshark-500rc2-released-new-theme-system-http-3-and-process-tracking/
Immich 3.4 arrives with JPEG XL support, mobile tagging, workflow improvements, and more:
https://alternativeto.net/news/2026/11/immich-3-4-arrives-with-jpeg-xl-support-mobile-tagging-workflow-improvements-and-more/
Jellyfin 0.20 for Android TV adds support for external video players & improved subtitles:
https://alternativeto.net/news/2026/11/jellyfin-0-20-for-android-tv-adds-support-for-external-video-players-and-improved-subtitles/
Pi-hole patches command-execution flaws and debug-log data leak in FTL v6.9 and Core v6.6:
https://alternativeto.net/news/2026/11/pi-hole-patches-command-execution-flaws-and-debug-log-data-leak-in-ftl-v6-9-and-core-v6-6/
Roundcube Releases 17 Security Fixes in 1.7.6 and 1.6.21:
https://www.linuxcompatible.org/story/roundcube-releases-17-security-fixes-in-176-and-1621/
(Post 7/8)
#WeeklyNews #OpenSource #FOSSNews #FOSS #OpenSourceNews #AI #LLM #AIAgent #AgenticAI #ArtificialIntelligence #Moose #LocalAI #Strata #Kitesurf #AgentNameService #ANS #SuperPoD #openEuler #Linkwarden #Wireshark #Immich #Jellyfin #PiHole #Roundcube #SelfHosting #SelfHosted #FosseryTech

Ich habe eine Subdomain und eine Wildcard subdomain (local.guerda.de und *.local.guerda.de)
auf eine private IP 192.168.178.31 gemappt.
Irgendwie löst aber mein Vodafone-Internet die Daten nicht auf, sodass ich obwohl ich im Netz bin nicht draufkomme. Als Fehler meldet Chrome mir DNS_PROBE_FINISHED_NXDOMAIN, Firefox sagt nur Server nicht erreichbar.
Nslookup.io sieht aber gut aus und löst schön alle Subdomains auf.
Habt ihr Ideen, was ich machen kann?


Typed by hand: Hello, bot
Ask pablomurad.com for a .env file and you get a riddle, a joke or a postcard from the end of the world, signed pmurad. A hundred messages, one nginx split_clients block and the scanners that read them all day.
Fresh from the lab: copyparty in practice, and the site that runs on it
A hands-on copyparty guide: install it from one Python file, set up volumes and permission letters, use up2k, file search, unpost and search, open WebDAV and SFTP, plus a few fun facts and how The Black Cat runs entirely on two copyparty instances.
https://pablomurad.com/copyparty-in-practice/
#SelfHosting #tutorial #OpenSource #tools

Alt...
copyparty in practice, and the site that runs on it

#selfhosting #NetBSD #RAIDframe

Alt...
Photo of NetBSD text console, showing the ETA 200 hours for RAID parity rebuild process.
START SELF-HOSTING TODAY!!!
#fedi #fediverse #selfhosting #selfhosted #libresoftware #freedom #FuckBigTech #Privacy #Security #CyberSecurity #FedoraServer

what the fuck is wrong with my shit
All the traffic in my home network is supposedly coming from my router? Like, okay duh it's what moves the packets around. But- all server logs are showing 192.168.1.1 as the client IP. SSH is showing a successful login from 192.168.1.1 (should be my phone). I try to access Home Assistant or others, and 192.168.1.1 is the client it sees. And coincidentally, websockets also stopped working. Yet somehow HTTPS apparently validated fine... and the arp tables are correct?? Genuinely confused here and slightly concerned(?)? ???
It's a stock AT&T fiber ONT gateway combo unit thingy. Ubuntu Server running a Docker Compose stack with all my stuff in it. Was working perfectly fine until it started doing this with no server-side changes whatsoever (once it's working I don't touch it ever).

Ein eigener Backupserver mit Debian, ZFS und BorgBackup
https://www.moellnitz.de/ein-eigener-backupserver-mit-debian-zfs-und-borgbackup/
#BorgBackup #Backupserver #Debian13 #Linux #ZFS #ZFSMirror #Datensicherung #Backupstrategie #Georedundanz #Datensouveränität #HetznerStoragebox #NAS #WireGuard #RTCWakeup #BackupAutomatisierung #SMARTMonitoring #Selfhosting
Digitale Souveränität – wir praktizieren sie seit 2003.
Während heute vielerorts darüber diskutiert wird, wie sich digitale Abhängigkeiten verringern lassen, betreiben wir bereits seit Ende 2003 eigene dedizierte Server.
Wir installieren, konfigurieren, administrieren und sichern unsere Systeme vollständig selbst. Dabei setzen wir auf Linux, freie Software und unsere langjährige praktische Erfahrung.
Auch unsere Hardware könnten wir selbst zusammenstellen. Dass wir heute fertige Geräte und die Infrastruktur von Hetzner nutzen, ist eine bewusste Entscheidung.
Unsere Unabhängigkeit beruht jedoch auf einem noch grundsätzlicheren Gedanken:
„Alles, was wir benötigen, richten wir für uns selbst ein. Fehlt uns dafür das notwendige Wissen, versuchen wir, es uns anzueignen. Gelingt uns das nicht, verzichten wir lieber darauf, gehen schwierigere Umwege oder lassen es ganz.“
Denn wer auf eine bestimmte Technologie oder Dienstleistung nicht mehr verzichten kann, verliert einen Teil seiner Entscheidungsfreiheit.
Was das für unsere tägliche Arbeit und die IT-Strukturen unserer Kunden bedeutet, beschreiben wir in unserem neuen Artikel:
Digitale Souveränität – für uns seit 2003 gelebte Praxis
#DigitaleSouveränität #Linux #OpenSource #Systemadministration #SelfHosting

Outlook-Störung. Wieder mal.
Anhand von #Microsoft sieht man, warum eine eigene IT (Selfhost oder Hybrid-Cloud) für JEDES Unternehmen wichtig ist:
Wer alles in eine fremde Cloud legt, kann bei Ausfällen nur zuschauen.
Wer seine IT selbst in der Hand hat, arbeitet weiter.
✔ Kontrolle über Ihre Daten
✔ Ausfallsicherheit durch Redundanz
✔ Unabhängigkeit von einzelnen Anbietern
What happened with Outlook will happen again.
Before you jump to another host, consider #selfhosting.
In 2026 you can have a fast and secure mail server of your own, easy to admin & update without a compsci degree. One that is tightly-secured, supports all mail clients, has top delivery & encrypted storage. All under your control, & your domain.
If that sounds interesting, sign up:
https://courses.nikau.io/convoy
We'll pick a date as a group, & I'll guide you all through the build.
Alt...
The title image for the convoy training, featuring Canadian Geese flying against a pale sky above the word convoy in caps.
Libre Linktree killer:
#LibreSoftware #LinkStack #Privacy #Security #CyberSecurity #SelfHosted #SelfHosting #FLOSS #FOSS #OpenSource

Hey guys! A few days ago, I messed up a pfSense update and lost my home Internet connection until I restored the backup I had.
I had thought about cloning the hard drive of the mini-PC I use to run pfSense as a precaution against hardware failures, but I'm wondering what strategy you self-hosters follow and what you recommend.
I’ve just renewed my mTLS certificates for @cloudflare Authenticated Origin Pulls. That turned out to be harder than it should have been (partially because I had lost my signing keys). #selfhosting

While #Microsoft is still dealing with issues with Exchange Online, we’re releasing another release candidate for #b1gMail 7.4.2. Hopefully, this will be the last one before the final version:
https://codeberg.org/b1gMail/b1gMail/releases/tag/7.4.2-rc5
Have fun testing it out and make the most of this time. Many thanks to cburkhard and @mkleger for contributing bug fixes recently.
#opensource #email #mailserver #php #m365 #diday #SelfHosting

Hello again, fediverse! 👋
I’m Alex, a Linux sysadmin in Scotland 🏴. I first joined in 2019, then wandered between servers and took a few breaks along the way, so consider this a fresh start.
I’m now running my own instance on GoToSocial, because I enjoy self-hosting things I probably don’t need to self-host. Outside of work I dabble in music production and plan to start on game development, both strictly as hobbies. Expect a mix of homelab tinkering, Linux war stories, open-source and privacy chat, the odd travel photo, and whatever I’m playing or listening to at the moment. I’ll use content warnings for heavier topics and alt text on images.
Question for you: what’s the best thing you’ve self-hosted that you couldn’t live without now?
#introduction #Scotland #SelfHosting #GoToSocial #Linux #SysAdmin #OpenSource #Privacy #MusicProduction #GameDev

Following many requests, I'm stoked to finally offer a self-paced version of the popular Cloudbreak live training.
15 lessons spanning 38 topics guide you all the way to a beautiful, truly private, post-big-tech & data-sovereign cloud deployment, all of your own. Along the way, you learn best-practices applicable to any self-hosted server build.
And just like the live training, no prior experience is needed.
https://courses.nikau.io/cloudbreak-self-paced
Alt...
Title image for the Cloudbreak Self-paced training, showing those words atop a grey-scale image of a cumulus cloud
That feeling when you are #selfhosting everything to have maximum resilience, but you still can't reach anybody because they are all affected by the global #Microsoft #outage ... 😒

Homelab check in. Proxmox on an old laptop with every service in its own LXC, split across VLANs so nothing can talk to anything it has no reason to. DNS runs through Pi-hole and Unbound. Wazuh and Suricata watch the traffic, OpenVAS runs scans, and Uptime Kuma tells me when something falls over. Everything leaves the network through a Mullvad gateway and I reach it all remotely over Tailscale. SearXNG is the newest piece and it's already the default search on my devices. I'm always in the middle of rebuilding something and the list keeps growing. What's the next service worth adding? I'm curious what you'd run if you were starting over.

I've always appreciated the simplicity of the BSDs. Power, yes, but without unnecessary complexity.
BastilleBSD and vm-bhyve have been my trusted companions for many years. But whenever I used Linux, I missed them.
That's why, years ago, I started putting together a collection of shell scripts (and some Python, although to a much lesser extent) to create something somewhere in between.
A bit of Bastille, a bit of vm-bhyve, a bit of Proxmox: unprivileged Linux system containers and virtual machines, managed from the command line.
Live backups. And live restore: bringing a workload back online before all its data has finished copying from the backup. Multiple storage backends. Encryption at the storage or individual workload level. Different networks. Isolation of each workload (a bit like illumos zones), with additional layers of protection.
Each container has its own UID/GID mapping. VMs run under separate unprivileged identities, with namespaces, seccomp and resource limits adding further layers of protection.
Pull-based backups from external hosts, with different levels and types of encryption. With raw encrypted ZFS replication, the backup server doesn’t even need the decryption keys. Backups are pulled over SSH by an external server. The workload host holds no credentials to log in to that server.
It also runs on a 1 GB Orange Pi PC 2, where I’ve tested both containers and native ARM64 KVM guests. And on a Orange PI One, armv7 and 512MB, it can run some lxc containers without problems, from the SD, using f2fs.
Simple disaster recovery. Because after those 142 servers went up in flames in Strasbourg, disaster recovery became something I care a lot about.
Currently supported and tested on Alpine Linux, Debian 13 and Armbian. On Debian, LXC containers also run under enforcing AppArmor profiles, adding another layer of protection.
Few commands. Lots of power. And it's called "Jail It!"
I'm not going to release it, at least not for now. I need to focus on my other projects, and Jail It! still needs some cleaning up.
But it works. And it does its job very well.
For containers, there's absolutely nothing running in the background. For VMs, just a small Python helper. No continuously running services. You connect via SSH, run your commands, and that's it.
Still, for anyone curious enough to have a look, I've put together a short demo on Asciinema:
https://asciinema.org/a/BbwGs99U9UJDLAzZ
Well, "short" might be a bit of an exaggeration. It's quite long, but I think it's worth watching all the way to the end.
#Linux #LXC #KVM #FreeBSD #Virtualization #OwnYourData #BSD #SelfHosting #Homelab #SysAdmin #DisasterRecovery
Published the results of my '2026 Self-Host User Survey' this morning, which received over 6,200 responses - a 52% increase from last year!
The results are super interesting and there were a ton of questions that surprised me. Check it out and let me know what you think.
https://selfh.st/survey/2026-results/
#selfhost #selfhosting #selfhosted #survey #opensource #foss #homelab #server #ai #jellyfin #smarthome #homeassistant #forgejo #plex #immich #software #sysadmin #devops #formbricks #hardware
🤖 Et si vous pouviez interroger votre wiki en langage naturel depuis votre terminal ?
Wiki.js 3 intègre un serveur MCP. Mon nouveau guide explique comment le connecter à Gemini CLI et OpenCode : jeton d'accès, réglages Nginx Proxy Manager pour le streaming, et astuces pour éviter les blocages de quota.
📖 https://wiki.blablalinux.be/fr/piloter-wiki-js-3-gemini-cli-opencode-mcp
#WikiJs #MCP #GeminiCLI #OpenCode #SelfHosting #Linux #LogicielLibre #BlablaLinux
Rendered and served: Two notebooks: Docs do Murad and Pablo, how?
Two places where the writing that doesn’t fit a blog lives: Docs do Murad, a compendium of recipes in Portuguese for servers, privacy and the web by hand, and Pablo, how?, a digital garden in English of fixes, concepts and lists.
https://pablomurad.com/docs-do-murad-and-pablo-how/
#projects #docs #DigitalGarden #SelfHosting

Alt...
Two notebooks: Docs do Murad and Pablo, how?
I've finally reached the acceptance stage.
My #unicomplex server is too big, too loud, and too overpowered for my #HomeLab. I'll finally listen to @pax0707 and let #NAS do NAS things.
I decided to go with #QNAP TS-664. It has enough power for #Plex and #Immich and nothing more. Also, I'll be happy to finally get rid of the #ZFS administration and optimization crap. Let QNAP handle this for me.
For real, that file system requires a doctor's degree to operate correctly.
I have a question for fellow homelabbers.
Who is streaming #Plex content from an SMB/CIFS mount through a 1 Gbps network? I mean when Plex is on one host and the content is on another. I need honest feedback, especially on 4k movies. Is it buffering sometimes? How is the overall experience?
#FedoraServer is the best server OS for beginners I guess?
#Fedora #Server #Linux #OS #Security #CyberSecurity #SelfHosted #SelfHosting #SelfHost #DIYorDIE
Written to disk: A practical guide to WebFinger
WebFinger is the small protocol that lets a fediverse server find @you@yourdomain. What it is, how a request and its JSON answer look, who uses it, and three ways to set it up on your own domain: a static file, an nginx map and a short PHP script that follows RFC 7033.

Questions to the Joplin Community: how do you sync your notes. Do you run a dedicated Joplin sync server, do you use Nextcloud as backend or maybe a plain webdav server like nginx with webdav mod?
What are the advantages using the dedicated Joplin server?
Till now i sync it via Nextcloud, but i dont know if i stick to nextcloud because it can do many things i never need.
#joplin #selfhosting #webdav @homelab
Hey selfhosting bubble could you recommend a service which tests my mail server for good practice regarding DKIM, SPF, DMARC, Connectivity etc. so the only problem remaining when sending E-Mails are the opaque spam filters of Google, Microsoft etc. which are meant to kill small participants in the E-Mail ecosystem?
@homelab #selfhosting #email #dmarc #dkim #spf #bestpractice
Fun fact about me. Since 2010 I have owned dima@mail.ua, which is about as short and as Ukrainian as an email address gets. I grabbed it back when mail.ua was still a Ukrainian service.
In 2012 the company sold it to Mail.ru Group, the Russian giant that is now called VK. Then in 2022 the Ukrainian side put the mail.ua domain on hold, and since then DNS simply does not resolve it. No delegation, no MX records, no incoming mail.
The funny part is that the domain keeps getting renewed, five years in a row now, and stays on hold every single time. I can still log in, and tens of thousands of my old emails are sitting in there. I just cannot receive a single new one, so I lost access to a bunch of services that still send their password resets to that address.
I have been running mail on my own domains since 2009, so it is not a real loss. Still annoying to watch a beautiful Ukrainian address slowly turn into a museum piece.
#Email #DNS #Ukraine #SelfHosting #FunFact
Alt...
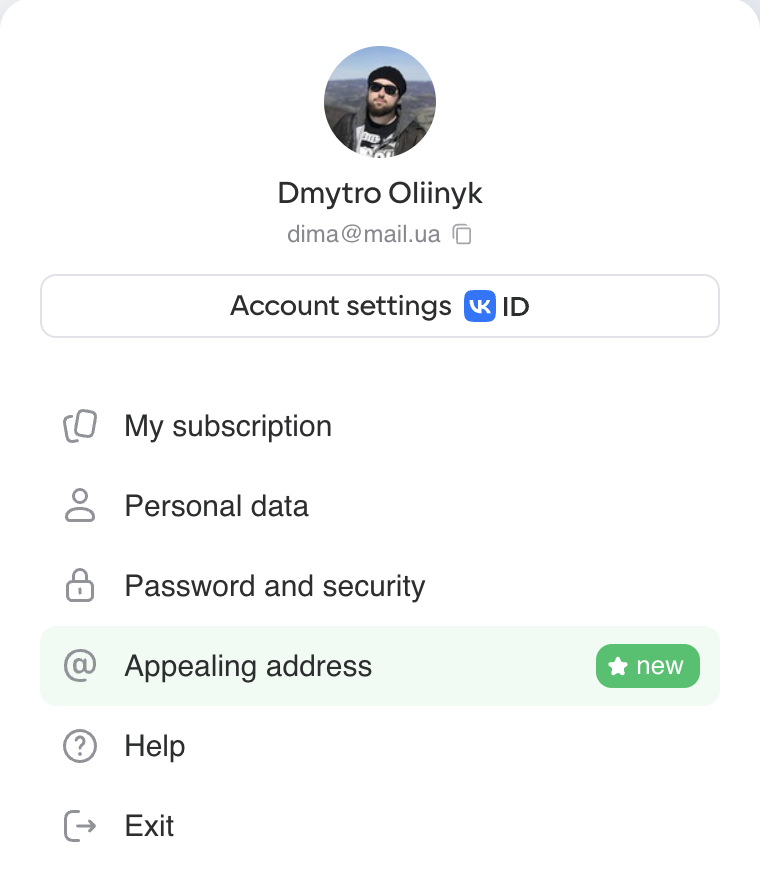
The account menu of a Mail.ru-style webmail service showing the name Dmytro Oliinyk and the address dima@mail.ua, with a VK ID badge next to Account settings and menu items for subscription, personal data, password and security, help and exit.
Linux and self hosting microblog update (which contains no Linux and little about self hosting):
I've routinely paid a quick oil change shop for their services for the past couple of decades - until this year.
This year, one of them made a serious mistake, which cost me an engine rebuild.
Yesterday, I changed my own oil.
I'm not more trained to protect my engine. I am simply more motivated to protect my engine.
This is why I now self-host my own email servers.
Engine oil changes and hosting email aren't a huge deal, but can be incredibly expensive when done wrong. It is scary to do it myself, but this year it became much scarier to trust someone else.
There's someone(s) out there I could trust for either, but finding them is more work, stress and risk than just doing it myself.
There's hundreds of companies who could do a good enough job for a fair price.
But zero of those companies have lately convinced me that they care about the harm that could come to me from mistakes, the way I care. Much less that they would lift a finger to make me whole if I was harmed by their mistake.
So, now, I do it myself, instead of working on something more interesting.
#devops #selfhosting #linux #oilchange #carrepair #righttorepair