Search results for tag #opensource


If any of my work on #OpenBSD, or my highlight posts here (or elsewhere) has been helpful in the past, a small recurring monthly donation would be extremely appreciated. 
https://brynet.ca/wallofpizza.html
https://dir.floss.fund/view/@brynet.ca
https://bsd.network/@brynet/114458997143046937

it was a fun challenge creating last week' app icon for @cjk's Gitte! "A simple Git client for @gnome"
check out all my recent app icons here:
https://planetpeanut.studio/icons
and if you want to help sponsor the effort:
https://planetpeanut.studio/sponsors
thank you. 😊
#linux #gnome #app #icon #design #foss #opensource #git #programming

Alt...
The new icon for Gitte in GNOME style on a brown background. A vibrant yellow bell with edged in markings going around it looking like a Git commit graph.
happy May!
these were the #FOSS app icons contributed in April: BitRitter, SparkleShare, Kotoba and Gitte.
delighted how these turned out! :)
also still looking to gain a sponsor this week to keep this flow going, any amount helps: https://planetpeanut.studio/sponsors
thank you.
#linux #gnome #opensource #app #icon #design

Alt...
4 app icons in a coloured grid. See the previous posts in this thread for detailed descriptions.
this week's app icon is for Nexus: "A simple and user-friendly Matrix client" by @QuadRadical
added to the list!
https://planetpeanut.studio/icons
#linux #gnome #opensource #app #icon #design #chat #matrix #android

Alt...
The new icon for Nexus in GNOME style on a dark blue background. A rounded rectangle with diagonal rainbow pattern. A circular white chat balloon with a blue ">" pops out of the middle of it.
last week's app icon is for Wardrobe: "Prettify your desktop effortlessly" by Nathan Perlman.
based on an existing sketch by @jimmac
https://flathub.org/apps/io.github.swordpuffin.wardrobe
#linux #gnome #opensource #app #icon #design #chat

Alt...
A pile of 3 socks (green, striped orange and blue) on a pink background.
app icon for Hex Colordle: "Find the color" by @krafting
#linux #gnome #opensource #app #icon #design
Alt...
The new icon for Hex Colordle in GNOME style on a vibrant blue background. A purple sheet passes through a wide golden device with three "???" on it. On the other end separate red/green/blue components come out.
week 23's app icon is for ChiPass: "a fork of KeePassXC" by @whitequark
https://planetpeanut.studio/icons
#linux #gnome #kde #opensource #app #icon #design
Alt...
The new icon for ChiPass in GNOME style on a green background. Three key cards held by a small ring in the top right corner. The front one has a "****" password field, some small text and a "chi" χ symbol.
week 26's app icon is for Lockpicker: "Recover passwords from their hash" by @sstendahl
check out all my recent app icons here:
https://planetpeanut.studio/icons
and if you want to help sponsor the effort:
https://planetpeanut.studio/sponsors
it really helps. 🌱
#linux #gnome #opensource #foss #app #icon #design #security #cryptography #password #hacking
Alt...
An unlocked purple padlock on a teal background with a light gold hairpin sitting diagonally in front of it.
week 27's app icon is for KawaiiFi: "Wi-Fi scanner and analyzer" by Zach Leytus
check out all recent icons here:
https://planetpeanut.studio/icons
and if you want to support an-app-icon-a-week:
https://planetpeanut.studio/sponsors
it really helps! 🌱
#linux #gnome #opensource #foss #app #icon #design #wifi #security #cute #kawaii
Alt...
A rounded rectangular wifi router with two blue antennas sticking out from the sides. the top has a Wi-Fi symbol, the from a "O v O" face.
week 28's app icon is for Stencil: "Rename batches of files" by @renef
check out all recent icons here:
https://planetpeanut.studio/icons
#linux #gnome #opensource #foss #app #icon #design
Alt...
A yellow square stencil with symbols "A B C *" overlaying a paper sheet on a green background.
week 29's app icon is for Metamorphosis: "Edit metadata" by @deimoshall
check out all recent icons here:
https://planetpeanut.studio/icons
#linux #gnome #opensource #foss #app #icon #design #flatpak #flathub

Alt...
A beige file paper with text lines folded into an origami butterfly on a red background.
week 30's app icon is for Era: "Manage your time" by @titouan_real
check out all recent icons here:
https://planetpeanut.studio/icons
#linux #gnome #opensource #foss #app #icon #design #flatpak #flathub #calendar #office
Alt...
A vertical/portrait wall calendar showing some highlighted week rows below and subtle cropped illustration of a solar system. Teal background.
week 31's app icon is for Ratio: "Validate color contrasts" by @markwyner
check out all recent icons here:
https://planetpeanut.studio/icons
#linux #gnome #opensource #foss #app #icon #design #flatpak #flathub #a11y
Alt...
A circular icon containing four vertical bars decreasing in lightness and saturation on a subtle grey'ish pink background/
week 32's app icon is for Haystack: "Edit OpenQA needles" by @jwh
check out all recent icons here:
https://planetpeanut.studio/icons
#linux #gnome #opensource #foss #app #icon #design #flatpak #flathub #calendar #opensuse #openqa #testing
Alt...
A rectangular yellow stack of hay. Some sprigs stick out from all sides. A purple magnifying glass is overlayed and reveals a tiny if you look really hard.
week 34's app icon is for Liferea: "Keep up with your feeds" by @lwindolf
check out all recent icons here:
https://planetpeanut.studio/icons
and if you want to sponsor an-app-icon-a-week:
https://planetpeanut.studio/sponsors
every little helps! 🌱
#linux #gnome #opensource #foss #app #icon #design #flatpak #flathub #rss #feed #reader
Alt...
A retro style magazine rack made out of black metal wire holding 3 magazines/newspapers of various colours on a green background.
Codeberg becomes inaccessible after registrar NameSilo suspends its domain, leaving the open-source hosting platform awaiting an explanation.
https://linuxiac.com/codeberg-domain-suspended-by-namesilo-disrupting-open-source-projects/
Alt...
Codeberg becomes inaccessible after registrar NameSilo suspends its domain, leaving the open-source hosting platform awaiting an explanation.
Package Installer 2.0 soll CachyOS einsteigerfreundlicher machen
Nach Octopi und Shelly wagt CachyOS den nächsten Anlauf. Der überarbeitete Package Installer soll Umsteigern von Windows den Weg ins Terminal ersparen.

🚀 RacksDB v0.8.0 is out: your datacenter in 3D!
🖱️ Explore your rooms, racks and equipment interactively in the web UI, with automatic camera rotation.
📦 Export them in the open glTF 2.0 standard with RacksDB metadata on every node: ready for digital twins, capacity planning and more.
Also new: collisions detection in diagrams.
Tails 7.17.1 entfernt uBlock Origin wegen Sicherheitslücke
https://linuxnews.de/tails-7-17-1-entfernt-ublock-origin-wegen-sicherheitsluecke/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Tails #uBlockOrigin #OpenSource

ICS[AP] updated CISA ICS Advisories Master File for 11/17/2026 & the following year's CSVs:
CISA_ICS_ADV_2026_11_17_26.csv
Available @ ICS[AP] GitHub:
https://github.com/icsadvprj/ICS-Advisory-Project/tree/main
Valve introduced screen savers to Steam Big Picture Mode, Steam Deck and Steam Machine back in October and you can customize it. Backlog is one to try out!
https://www.gamingonlinux.com/2026/11/backlog-is-a-seriously-cool-custom-screen-saver-for-steam-big-picture-mode-steam-deck-steam-machine/

Btrfs-Entwickler gegen „Neulinge ohne gesunden Menschenverstand“
Der Entwickler Qu Wenruo arbeitet am Dateisystem Btrfs und hat ganz offensichtlich die Behinderungen durch KI-Slop und unerfahrene Anwender „ohne gesunden Menschenverstand“ satt.
https://www.linux-magazin.de/news/btrfs-entwickler-gegen-neulinge-ohne-gesunden-menschenverstand/
#KI #AI #linux #opensource #Btrfs #Dateisystem #Entwicklung
Alt...
Das Bild zeigt eine Grafik mit einem Pinguin, der das Logo von Linux darstellt. Der Pinguin hat eine typische Linux-Design-Ästhetik mit einem schwarzen Körper, einem weißen Bauch und gelben Füßen.

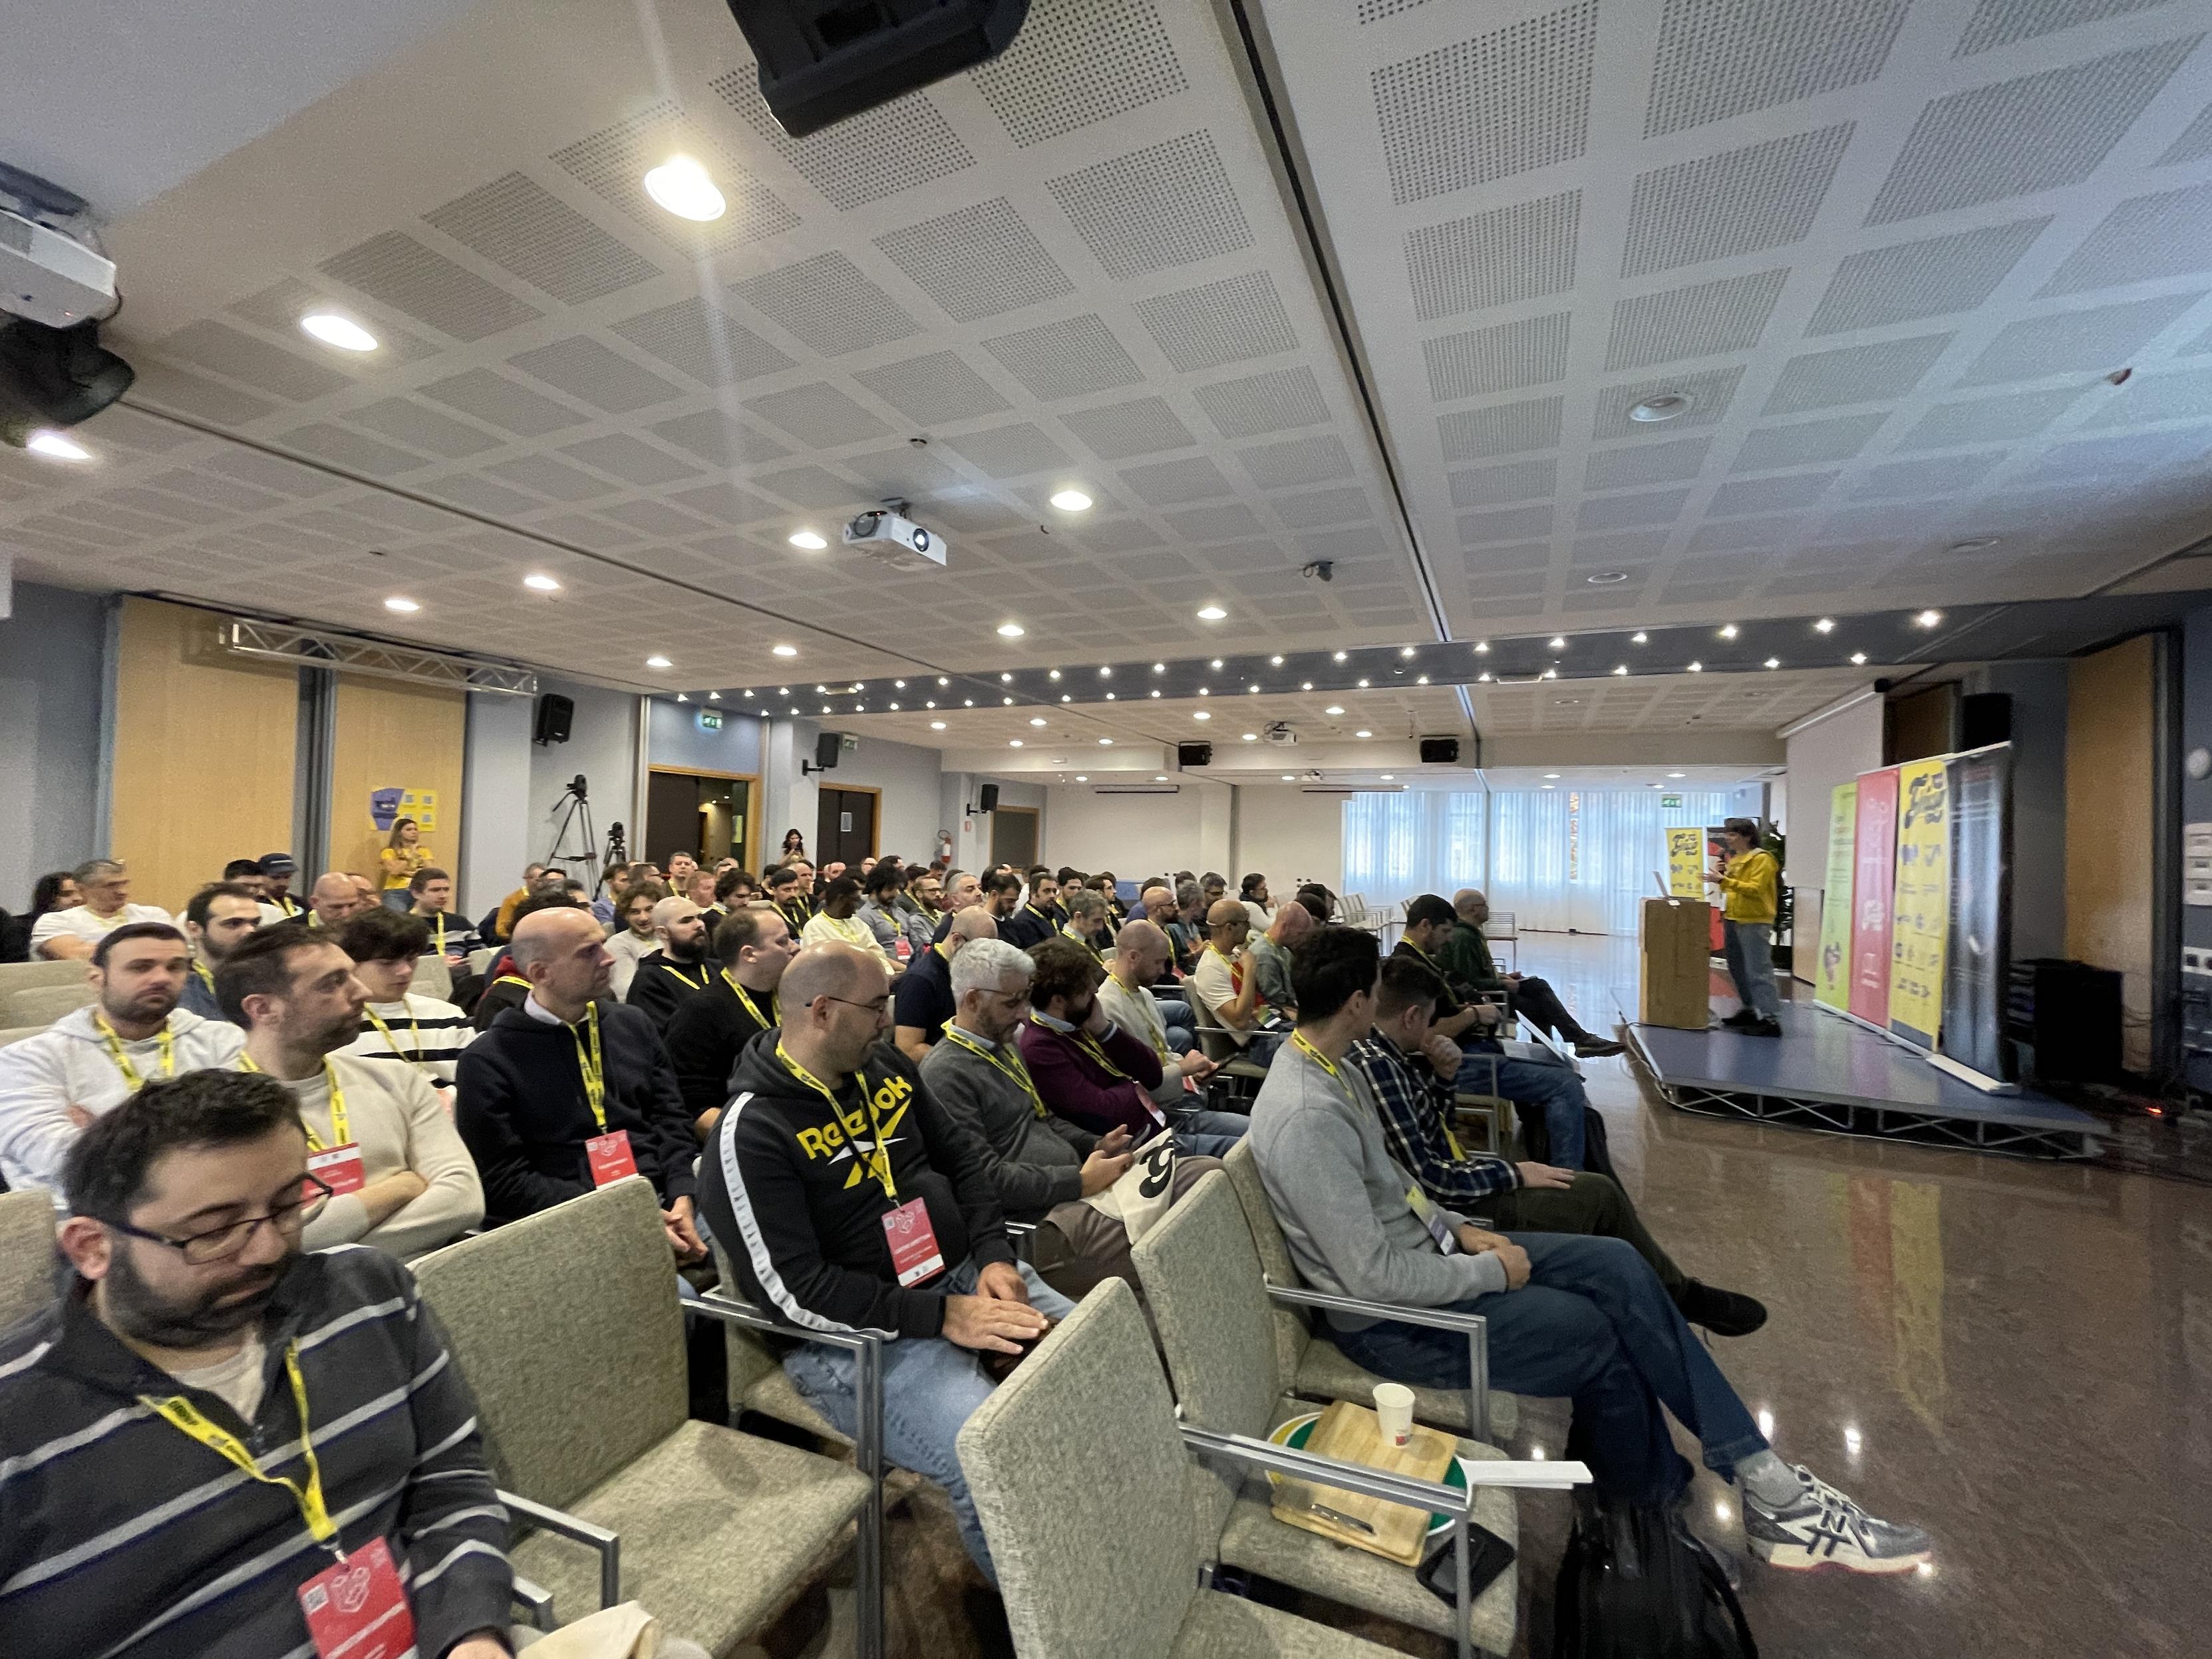
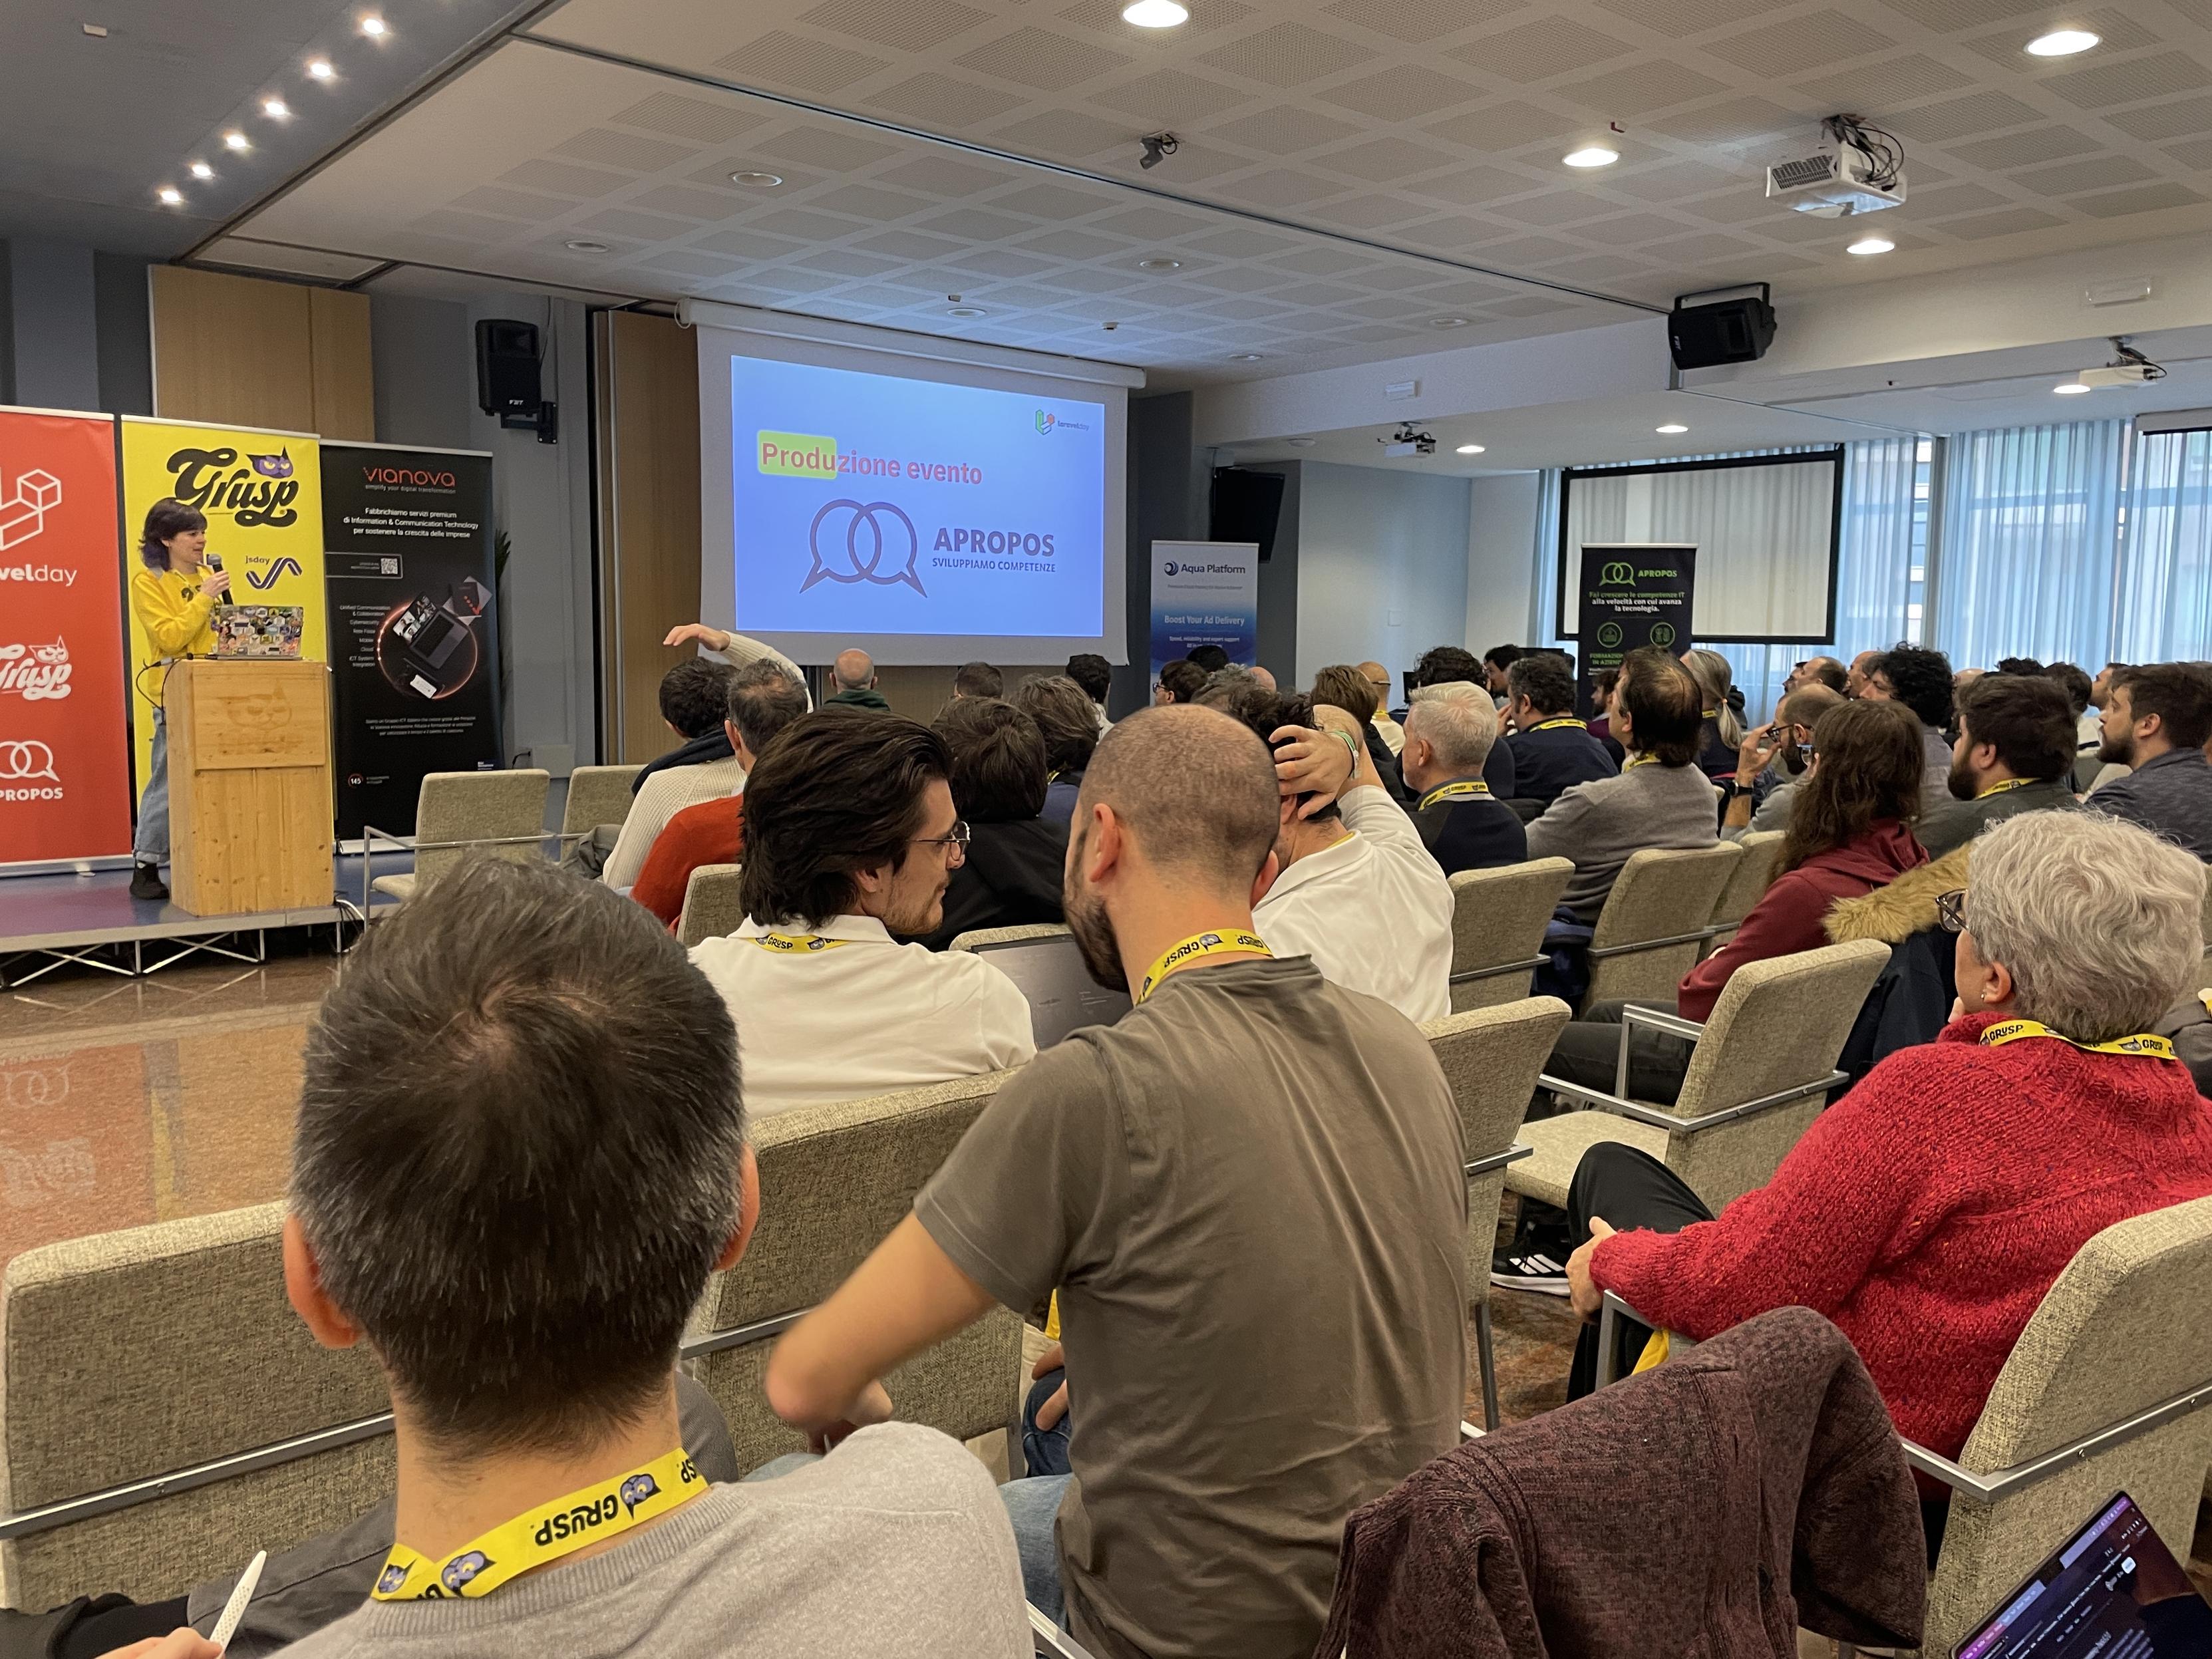
#laravelday 2026 è partita. ✨ Decima edizione a Verona con la community italiana di #Laravel e #PHP.
Sul palco oggi: agenti AI con MCP, AG-UI e A2UI, un’esigenza personale diventata progetto #OpenSource, un anno di architettura esagonale, un bug raccontato come un’indagine, da N branch a una codebase per SaaS multi-cliente, #observability, AI-readability e il panel sul futuro dello stack.
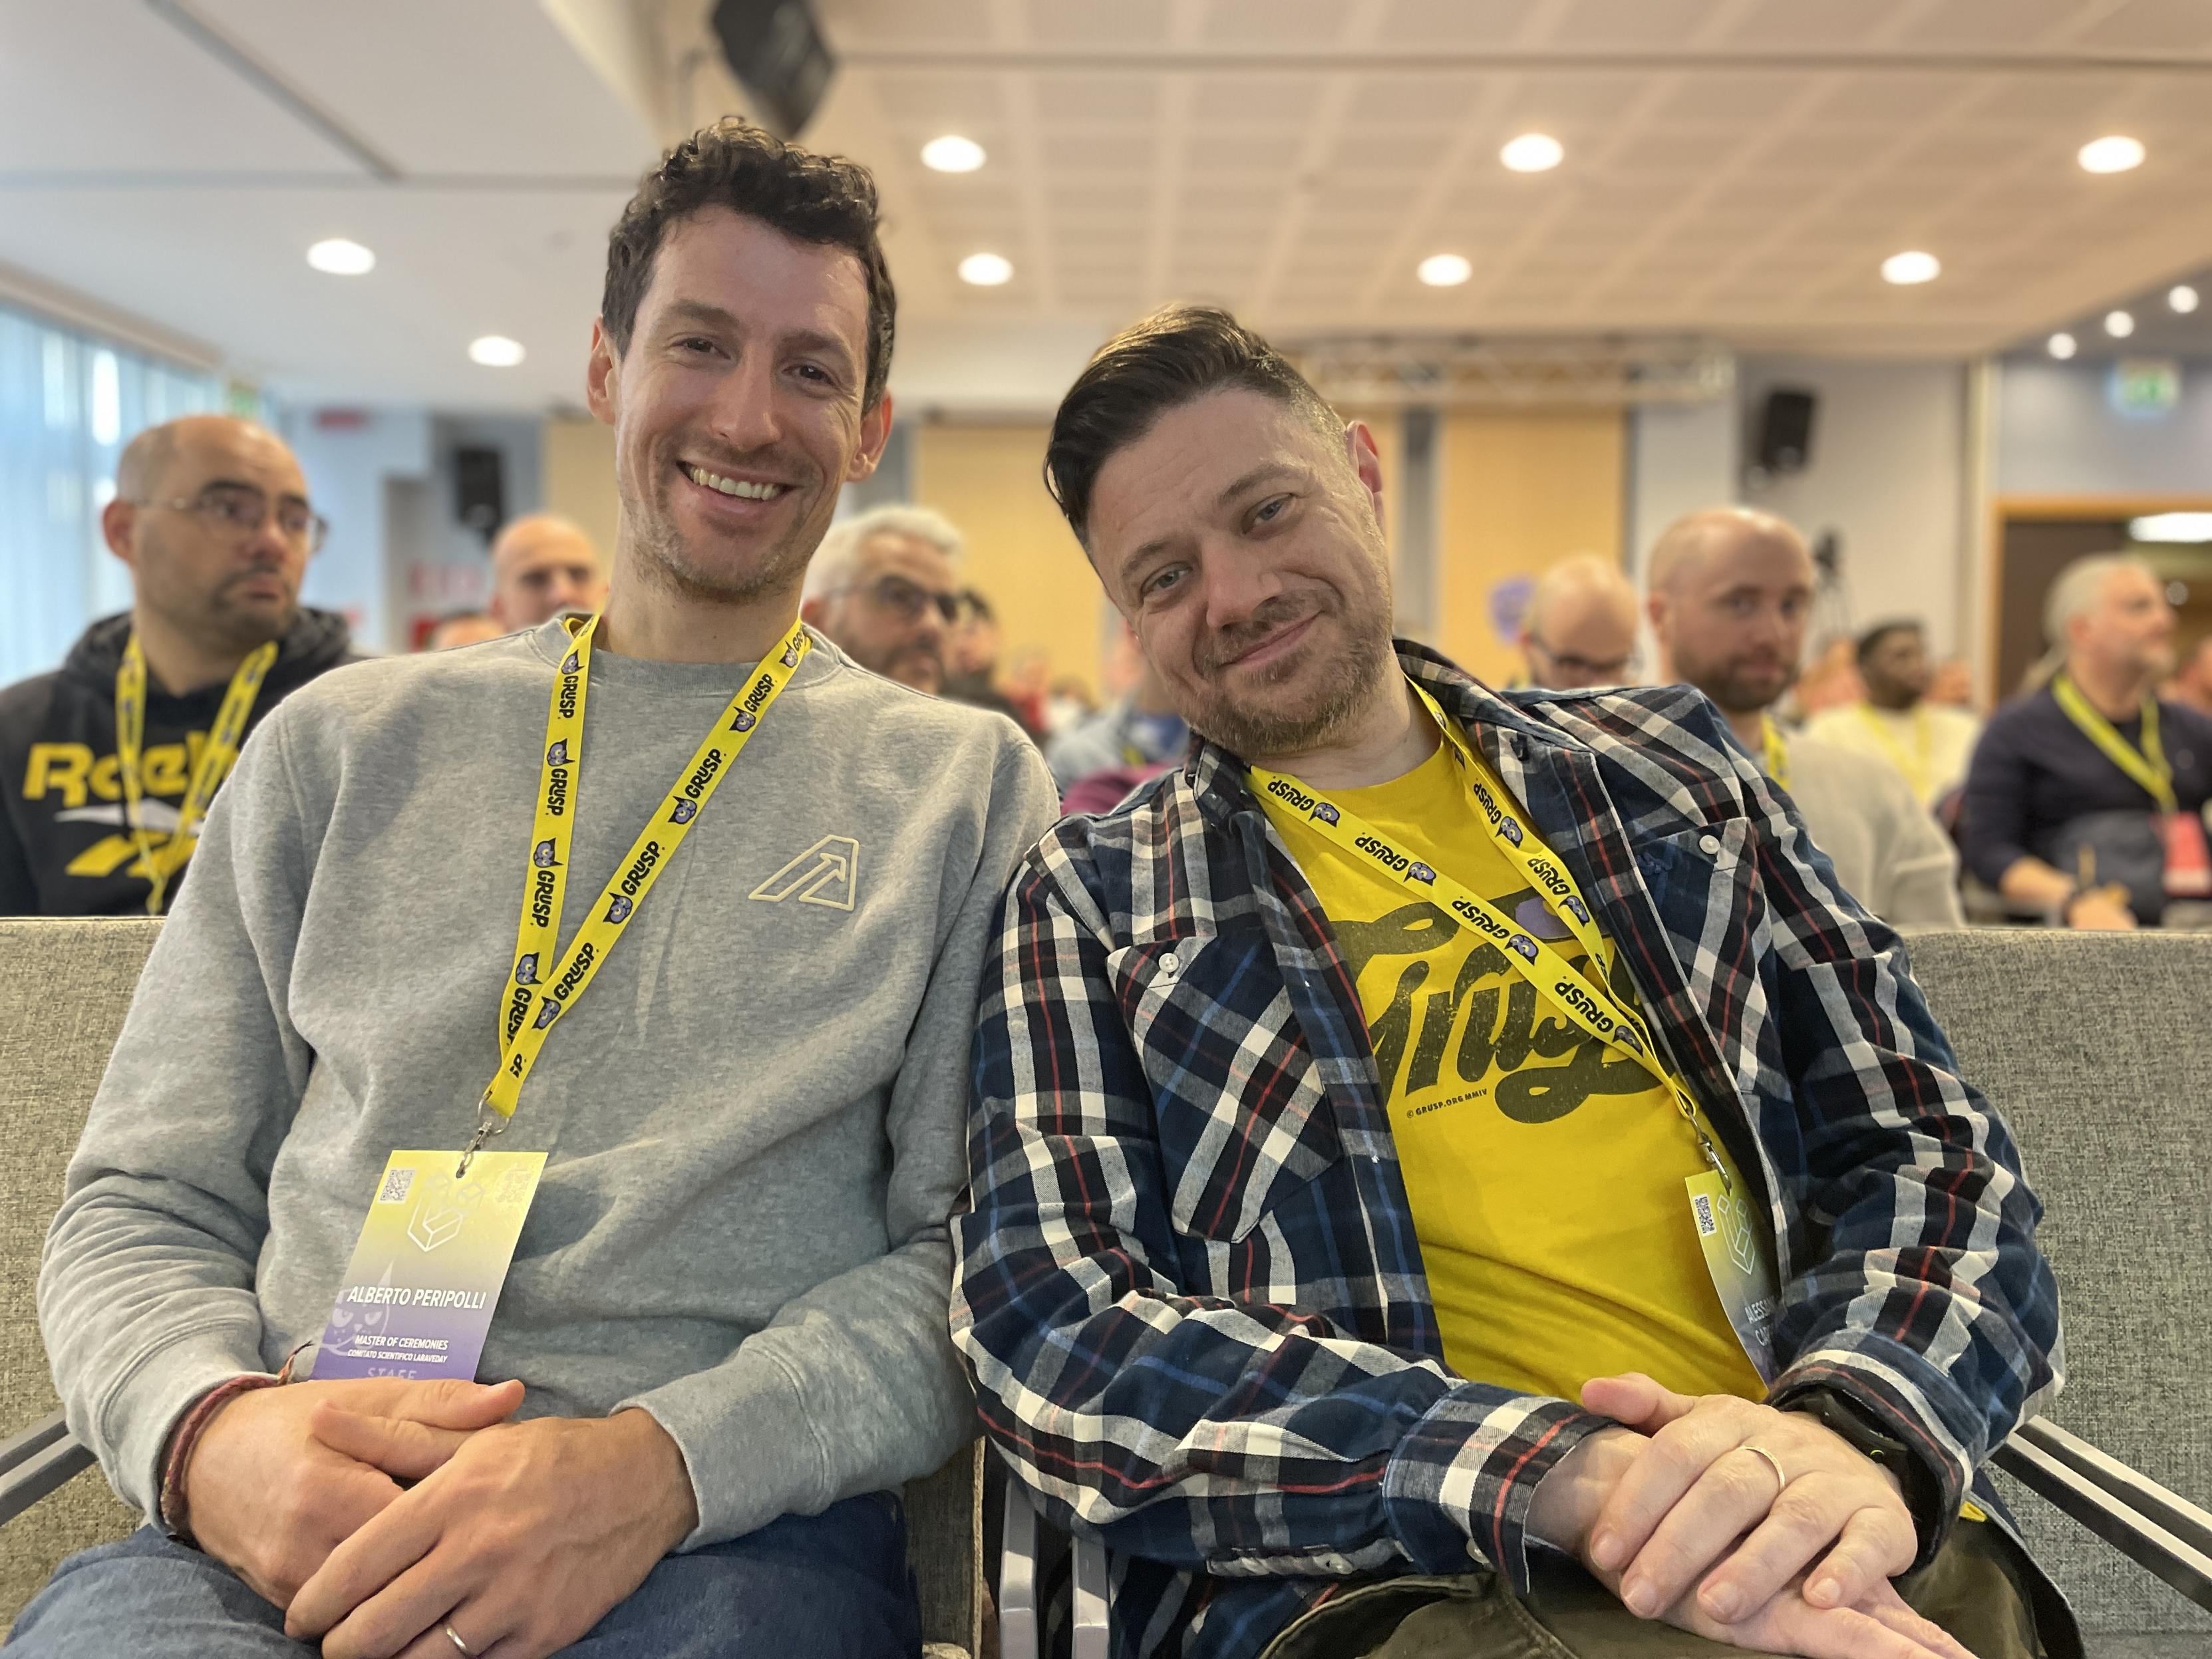
Conducono Alberto Peripolli e Alessandro Cappellozza.
Alt...
Alberto Peripolli e Alessandro Cappellozza
Alt...
Sala laravelday 2026
Alt...
Pubblico laravelday 2026

The Drop Times, das Drupal-Magazin, hat über Sites 1.0.0-beta3 berichtet, unsere Lösung für viele Websites unter einem Dach. Neu: Einzelne Websites können eine eigene Webadresse bekommen. Noch ist es eine Beta. Artikel auf Englisch: https://www.thedroptimes.com/node/73673
https://www.drupal.org/project/sites
#Drupal #OpenSource #Sites
Canonical introduced the Edge archive and Surge system, letting Ubuntu Pro users install Ubuntu Edge AI patches before full human review.
#Ubuntu #Canonical #Linux #Cybersecurity #AI #OpenSource #InfoSec #TechNews
https://securityonline.info/ubuntu-edge-ai-patches/?utm_source=mastodon&utm_medium=jetpack_social
The latest FreeBSD report is here, and the AI debate is ongoing : r/freebsd
Liam Proven at The Register has written one of the sharpest pieces on open source and AI that I've read in a while, and he's done it inside what looks like a routine quarterly report write-up.
On the surface it's a roundup of the FreeBSD Q3 2026 status report: 51 entries across 16 projects, including Sylve (a Proxmox-style GUI for FreeBSD virtualisation hosts) and AppJail (containerised app distribution, FreeBSD's answer to Snap and Flatpak). That part is clear, well chosen, and useful on its own.
The real value is how he handles FreeBSD's long-running argument over code written by LLM coding assistants. He doesn't just repeat the developer survey figures. He reads them closely and sees what they add up to. Nearly everyone wants a policy, plus human review, disclosure and accountability. Only a small minority want the stuff discouraged at all. Then he puts that next to NetBSD's 2024 ban (which, despite the doom-mongering, hasn't made NetBSD irrelevant), OpenBSD's open mockery, and Debian's recent vote, where even a Condorcet ballot full of refusal options ended up permitting the bots.
His conclusion is blunt and hard to argue with: FreeBSD will tell its developers to "be careful", and LLM-generated code will get committed anyway.
This is what good tech journalism looks like. He knows the history, knows the communities, makes the comparisons nobody else bothers to make, and is willing to say where this is heading even when the answer is unwelcome. If you're as wary of the LLM gold rush as he is, and as I am, read it. If you aren't, read it anyway.
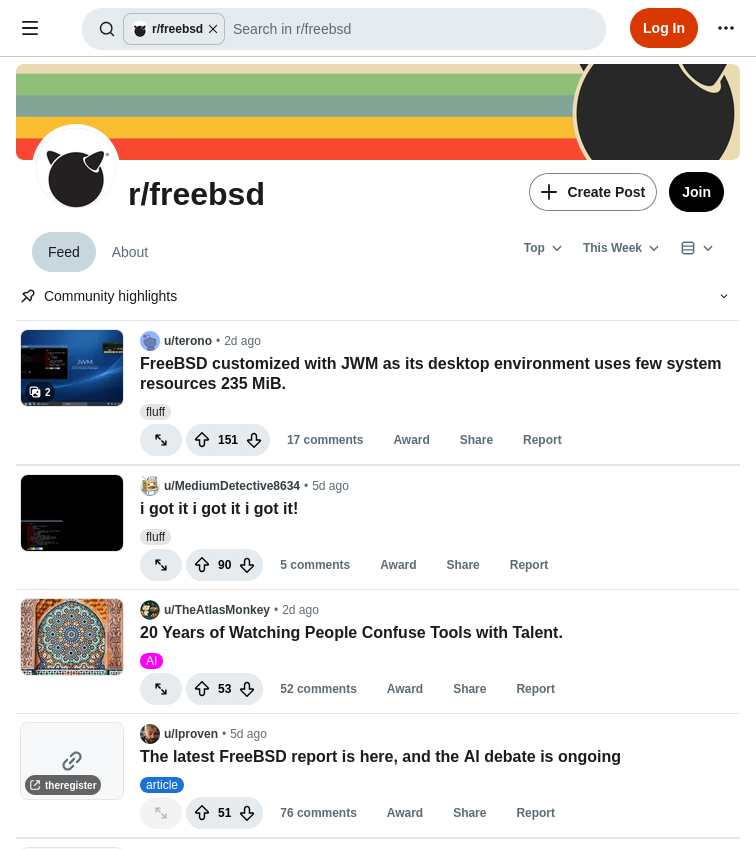
Here's the Reddit post through which he promoted the piece:
#AI #Anthropic #Claude #BSD #Debian #FreeBSD #LLM #LLMs #NetBSD #OpenBSD #OpenSource #Opus #Reddit #TheRegister
This week's number 1 article:
― https://www.reddit.com/r/freebsd/top/?t=week&feedViewType=compactView
Discussion in El Reg:
― https://forums.theregister.com/forum/all/2026/11/12/202610/
Alt...
Screenshot: this week's top four posts in the FreeBSD subreddit — https://www.reddit.com/r/freebsd/top/?t=week&feedViewType=compactView
Alt...
The Register's thumbnail for https://www.theregister.com/os-platforms/2026/11/12/the-latest-freebsd-report-is-here-and-the-ai-debate-is-ongoing/5309206 – a robotic hand at a computer keyboard.
Godot Engine continues pulling in more funding to help the cross-platform open source work, now with an AI company helping.
https://www.gamingonlinux.com/2026/11/ai-company-manus-becomes-a-godot-engine-platinum-sponsor/
Rust und Linux-Kernel: Torvalds pocht auf verständliche Syntax
https://www.pcgameshardware.de/Linux-Software-26761/News/Linus-Torvalds-Rust-Kritik-Lesbarkeit-C-Code-1560046/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Rust #Kernel #LinuxKernel #OpenSource

Open sourcing your hardware is very, very powerful and lifesaving if you are humble enough.
Someone named "4AGTE" on Reddit has pointed out that the polarized inductor on FramePico2 Expansion Card is placed wrongly on the PCB editor while it was true on the schematics. In fact I didn't believe them as it was just correct on the schematics, but then I realized it was somehow reversed on the PCB. This probably happened due to a software bug (or maybe a bit upset with an electron coming from space and hitting my PC), and it would pass my eyes if it wasn't for that person. We quickly fixed the design and realigned it on the prototypes we have. Thank you 4AGTE!
Our FramePico2 Expansion Card is fully open source hardware certified by @oshwassociation as TR000006, and its coming soon to @crowdsupply under our brand @riscfruit
#opensource #hardware #foss #pcb #kicad #crowdsupply


🚀 ndaal_public_auditd Update auf v0.9.3!
Unser Enterprise-Framework für Linux auditd wurde massiv ausgebaut: Fast 15.000 präzise b32/b64-regeln, vollständiges MITRE ATT&CK v19.2 Mapping, arc42-Architekturdokumentation und multinationale Doku in 5 Sprachen.

Digital Omnibus: The AI Act Has Already Changed, While GDPR and Cookie Rules Are Still Under Negotiation
The Digital Omnibus, the package through which the EU is changing the rules on artificial intelligence, the GDPR, and cookie banners, has only been partly approved.
https://vsx.global/digital-omnibus-ai-act-amended-gdpr-cookies-pending/
Video introducing the #Librem5 v2 by @purism.
The phone that frees you from #bigtech.
#mobilelinux #FOSS #digitalsovereignty #opensource #PureOS #riscv #phone #linux #l5v2

RT @SenseTime_AI: #SenseNova-Loop-9B ist offiziell da — jetzt #OpenSource!
mehr auf Arint.info
#AI #DeepLearning #Innovation #MachineLearning #OpenSource #TechNews #arint_info
Are you folks getting supported by Donald Trump?
Someone from @CoMaps says so:
https://codeberg.org/comaps/Governance/issues/184
#Signal #CoMaps #Scandal #Cringe #LibreSoftware #FLOSS #FOSS #OpenSource
LibreOffice remote code execution PoC for CVE-2026-104007 and CVE-2026-104692 is public: one opened spreadsheet runs code. Update to 26.2.7 or 26.8.2.
#LibreOffice #RCE #PoC #CVE #OpenSource #PatchNow #CyberSecurity #InfoSec
A Linux phone that can run Android apps without an emulator? That's what Denial OS is working on.
It's a Linux-based mobile OS designed as an alternative to Android and iOS, with its own Wayland compositor and native apps.
What makes it interesting is Droidloom, which runs Android apps directly on Linux, without a VM or emulator.
Other features include:
🔹Mobile data and SIM support
🔹Fingerprint unlock and gestures
🔹Haptics and screen rotation
🔹Desktop mode
Currently being brought to devices including the RedMagic 11 Pro, OnePlus 12R, Motorola Edge 70 and OnePlus Pad 4. Installation images and feature support vary by device.
One limitation: according to the developer, Droidloom doesn't currently pass Play Integrity, so some banking apps may not work.
Could this be a serious alternative for those looking to move away from Android?
Nachrichten lese ich gerne mal zwischendurch. Klar, eine Website ist schnell geöffnet, aber eine App kann mehr: Sie meldet sich, merkt sich Dinge und hält die Übersicht. Deshalb gibt es PlanetFOSS jetzt auch als Android-App, ohne Konto, ohne Google-Dienste und ohne Tracking.
Die APK liegt auf GitHub, für den Start bei Google Play suche ich noch Tester. F-Droid folgt bald. Was fehlt euch, damit so eine App auf eurem Handy bleibt?
https://linuxundich.de/planetfoss-android-app-linux-nachrichten/
#PlanetFOSS #Android #Linux #OpenSource

Alt...
Ein Smartphone mit der PlanetFOSS-App liegt auf einer Notebook-Tastatur und zeigt den Rückblick auf Woche 46.

[Stéphane HUC :: IT Log] nous offre la Traduction de l'article EN → FR 'Beyond Linux: A Journey Through the Open Source Ecosystem' - article de Stefano Marinelli promouvant la conférence donnée durant le Linux Day 2026 à Modène.
"Beyond Linux : Un voyage à travers l'écosystème open source"
NoisyTCP: Remote-Lücke im Linux-Kernel-TCP-Stack
Die Schwachstelle namens „NoisyTCP“ (CVE-2026-99288) steckt im Linux-Kernel und ermöglicht einen Remote-DoS-Angriff im TCP-Stack vor der Authentifizierung.
https://www.linux-magazin.de/news/noisytcp-remote-luecke-im-linux-kernel-tcp-stack/
#linux #opensource #Debian #NoisyTCP #CVE202699288 #LinuxKernel
Alt...
Das Bild zeigt eine Grafik mit einem Pinguin, der das Logo von Linux darstellt. Der Pinguin hat eine typische Linux-Design-Ästhetik mit einem schwarzen Körper, einem weißen Bauch und gelben Füßen.
Plasma 6.8: Der Abschied von X11 wirkt nach
https://linuxnews.de/plasma-6-8-der-abschied-von-x11-wirkt-nach/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #KDE #Plasma #KDEPlasma #X11 #OpenSource

This post was updated today.
Picus: ARTEX in the Wild: How Threat Actors Weaponize an AI Pentesting Agent https://www.picussecurity.com/resource/blog/artex-in-the-wild-how-threat-actors-weaponize-an-ai-pentesting-agent #infosec #opensource #espionage

🚀 Das App-Repo von Shlinker ist jetzt öffentlich – und auch ein erstes DEV-Paket!
Shlinker ist ein nativer Android-Client für selbst gehostete Shlink-Instanzen, lizenziert unter GPL-3.0.
Technisch funktioniert die App bereits, aber sie ist noch eine frühe Entwicklungsversion, kein fertiger Release. Es gibt noch etliche Ecken, Kanten und Kleinigkeiten zu erledigen – vor allem die UX steckt noch deutlich im „Entwicklermodus“. 🔧
Code & DEV-Paket:
https://code.awit.at/Shlinker/Shlinker_App
Noch ein Hinweis: Aus privaten Gründen wird es bei der Entwicklung vorübergehend ruhiger. Voraussichtlich ab Mitte bis Ende Januar 2027 geht’s wieder aktiver weiter. Kleinere Updates sind zwischendurch möglich, aber ohne Versprechen.
Reinschauen, ausprobieren und Feedback geben ist ausdrücklich willkommen – bitte mit Baustellenhelm und etwas Geduld bei Antworten. 🙂
#Shlinker #Shlink #Android #OpenSource #SelfHosting #BuildInPublic
🚀 Shlinker’s app repository is now public — and so is the first DEV package!
Shlinker is a native Android client for self-hosted Shlink instances, licensed under GPL-3.0.
It already works, but this is an early development preview, not a polished release. There are still plenty of rough edges and small things to finish — especially the UX, which is very much still in “developer mode.” 🔧
Code & DEV package:
https://code.awit.at/Shlinker/Shlinker_App
A little heads-up: personal commitments mean development will be quieter for a while. I expect to get back to more active development around mid-to-late January 2027. Smaller updates may happen in the meantime, but no promises.
Feel free to explore, try it out, and share feedback — just bring your hard hat and expect slower replies for now. 🙂
#Shlinker #Shlink #Android #OpenSource #SelfHosting #BuildInPublic
Paperless-ngx 3.5.0 veröffentlicht: Das ist neu
https://stadt-bremerhaven.de/paperless-ngx-3-5-0-veroeffentlicht-das-ist-neu/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Paperless_ngx #OpenSource
Linus Torvalds will Kernel-APIs mit KI außerhalb des Codes prüfen lassen
https://www.pcgameshardware.de/Linux-Software-26761/News/Linux-7-4-Torvalds-API-Spezifikation-KI-Pruefung-1560221/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Kernel #LinuxKernel #KI #OpenSource
Azure Linux erhält über 470 CVE-Korrekturen in einem einzigen Update
https://fosstopia.de/azure-linux-3-0-2022/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Azure #AzureLinux #CVE #OpenSource

From Clément Delangue, CEO of #HuggingFace (@huggingface), on #AI risks:
https://www.wired.com/story/wired-yearbook-2026-clement-delangue/
"I actually think that 95 percent of the risks are being created by a few companies that are pushing the frontier behind closed doors. And 95 percent of the protection or defense is going to be done by the #OpenSource ecosystem."

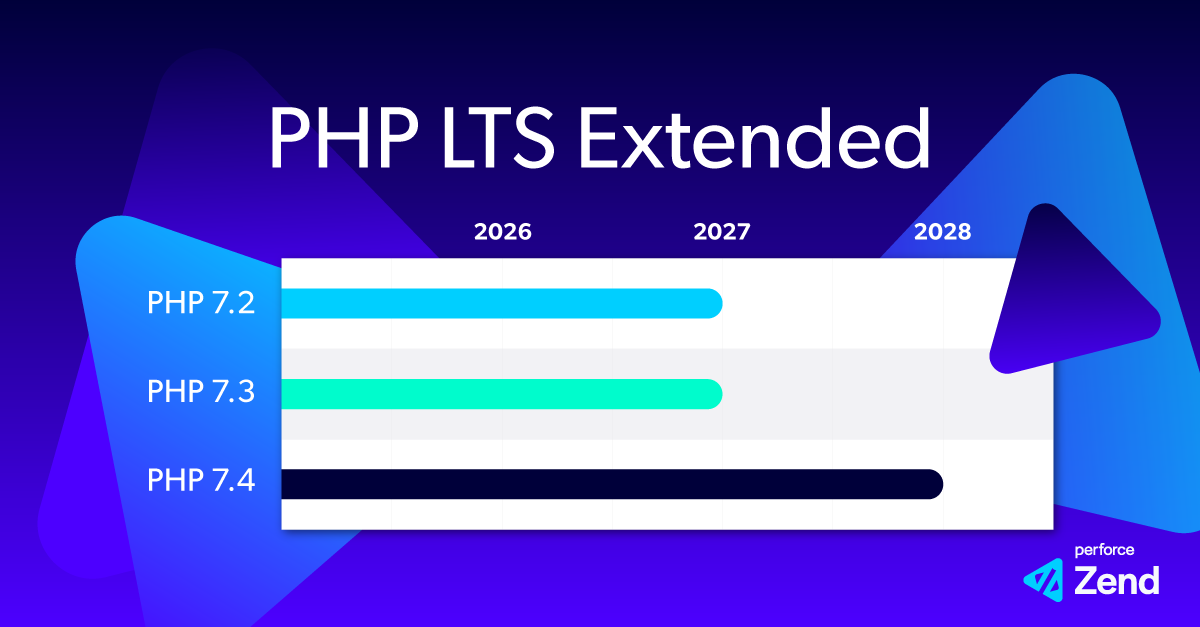
We're extending Zend PHP Long-Term Support:
🐘 PHP 7.2 and 7.3: supported through 2027
🐘 PHP 7.4: supported through 2028
Upgrading shouldn't mean rushing a migration or running unpatched in production. LTS keeps these versions secure with tested security fixes while you plan your move.
Details: https://ter.li/rl01jq
Alt...
The words PHP LTS Extended with a timeline showing support for 7.2 and 7.3 through 2027, and 7.4 through 2028. The Perforce Zend logo is in the bottom right corner.
Die Ästhetik der Beständigkeit:
Meine Erfahrung mit Debian 13 im Alltag.
https://krisu.eu/blog/die-aesthetik-der-bestaendigkeit/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Debian #Debian13 #OpenSource
RHEL & Co. 10.3: Warum Admins vor dem Update besser genau hinschauen
RHEL, AlmaLinux und Rocky Linux 10.3 sind da: Die Updates bauen Sicherheitsfunktionen aus, erfordern bei Grafana und Containern aber Vorarbeit beim Upgrade.
#Systemverwaltung #IT #Linux #OpenSource #RedHatEnterpriseLinux #news
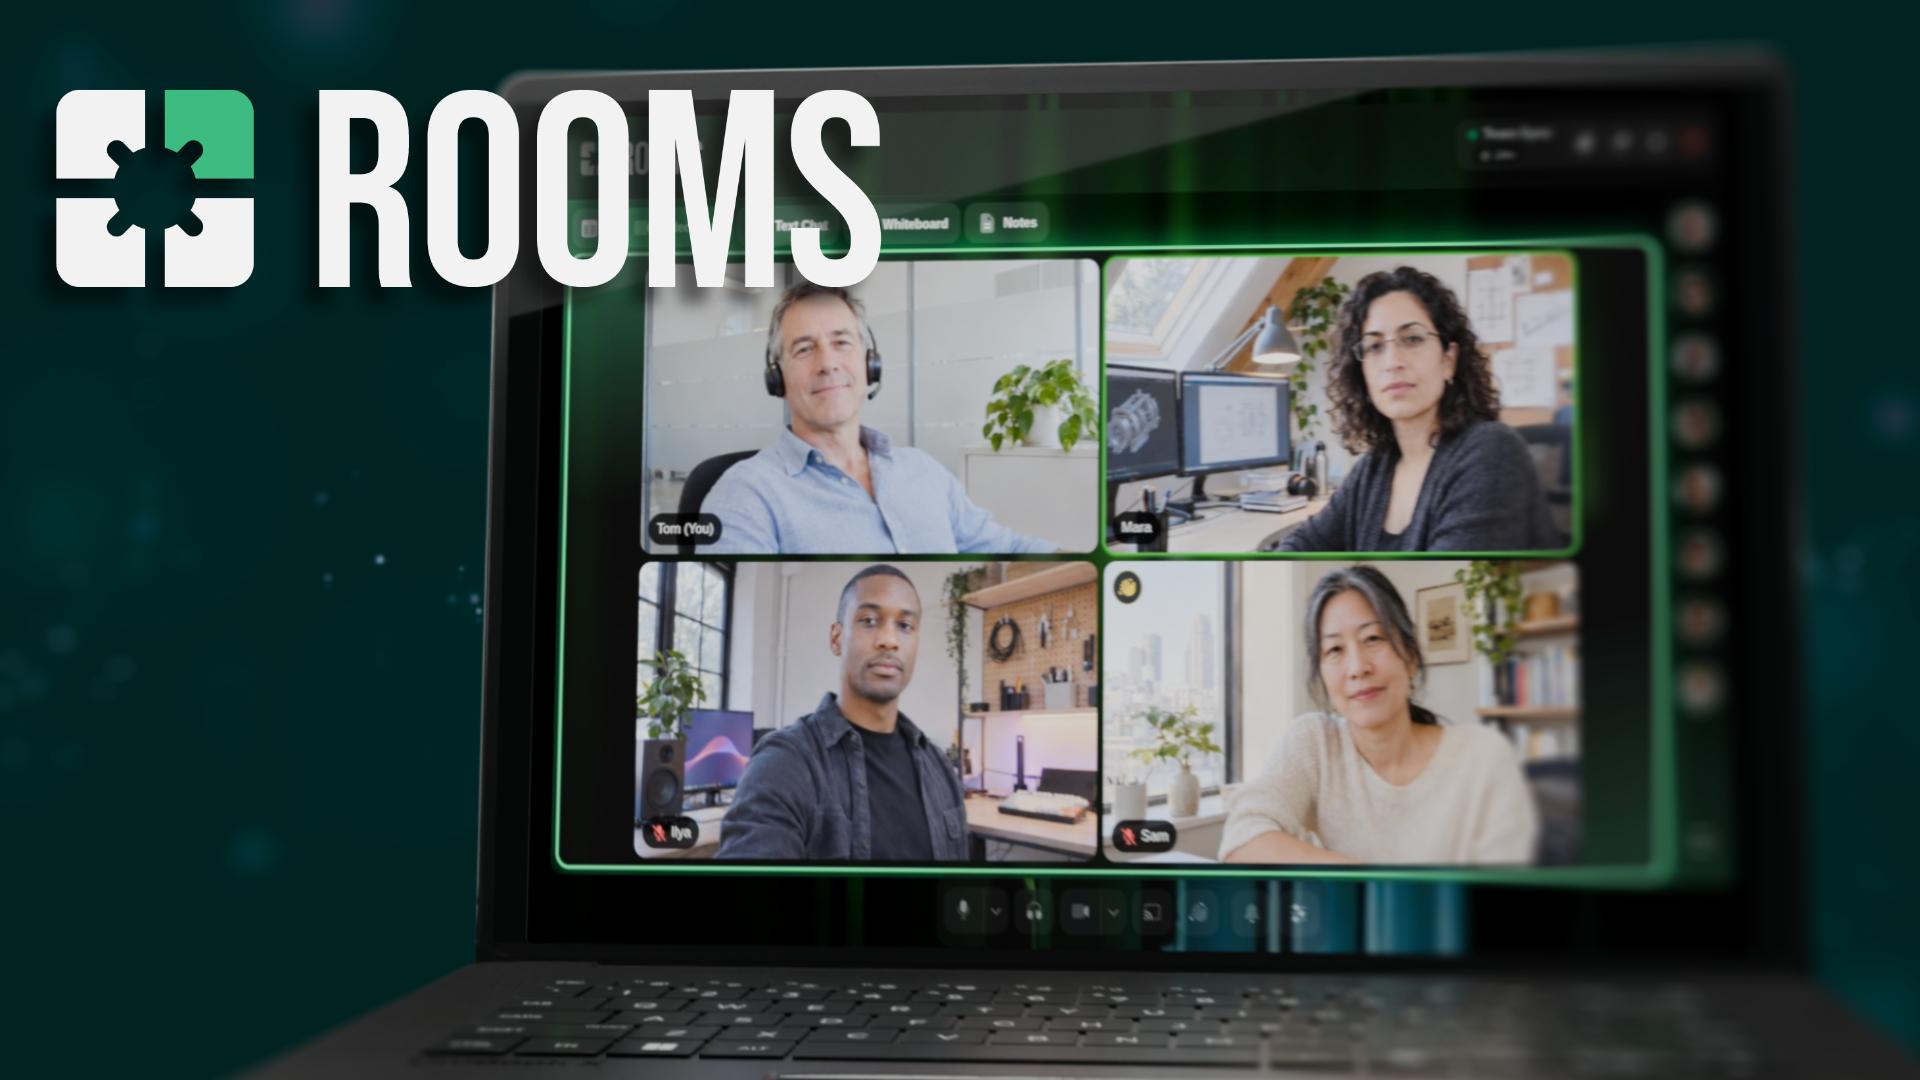
In eigener Sache: Golem Rooms – Souveräne Videokonferenzen aus Deutschland
Unser Schwesterunternehmen Golem bringt mit Golem Rooms erstmals ein eigenes Softwareprodukt auf den Markt.
#linux #opensource #GolemRooms
Alt...
Großer weißer Schriftzug „ROOMS“ mit vierteiligem Logo vor einem Laptop. Auf dessen Bildschirm ist eine Videokonferenz mit vier Personen in einem grün umrandeten 2×2-Raster zu sehen.

Xbox-PC-Spiele unter Linux? 🐧
Ich stelle xTux vor: ein freies Community-Projekt auf Basis von Xodus, mit Launcher, Store-Katalog und Downloads für Microsoft-Store- und Game-Pass-Spiele.
Noch experimentell: Nicht jedes Spiel läuft. Gesucht sind Tester und Mitwirkende für Rust, Wine/GDK, Doku und Packaging.
Teste dein Spiel und teile dein Ergebnis oder hilf beim Entwickeln:
https://tux-force.github.io
Repo: https://github.com/Tux-Force/xTux
#LinuxGaming #OpenSource #Rust #FOSS #Proton #Wine #Xbox #Windows #Linux #SteamDeck #Gaming #gamepass
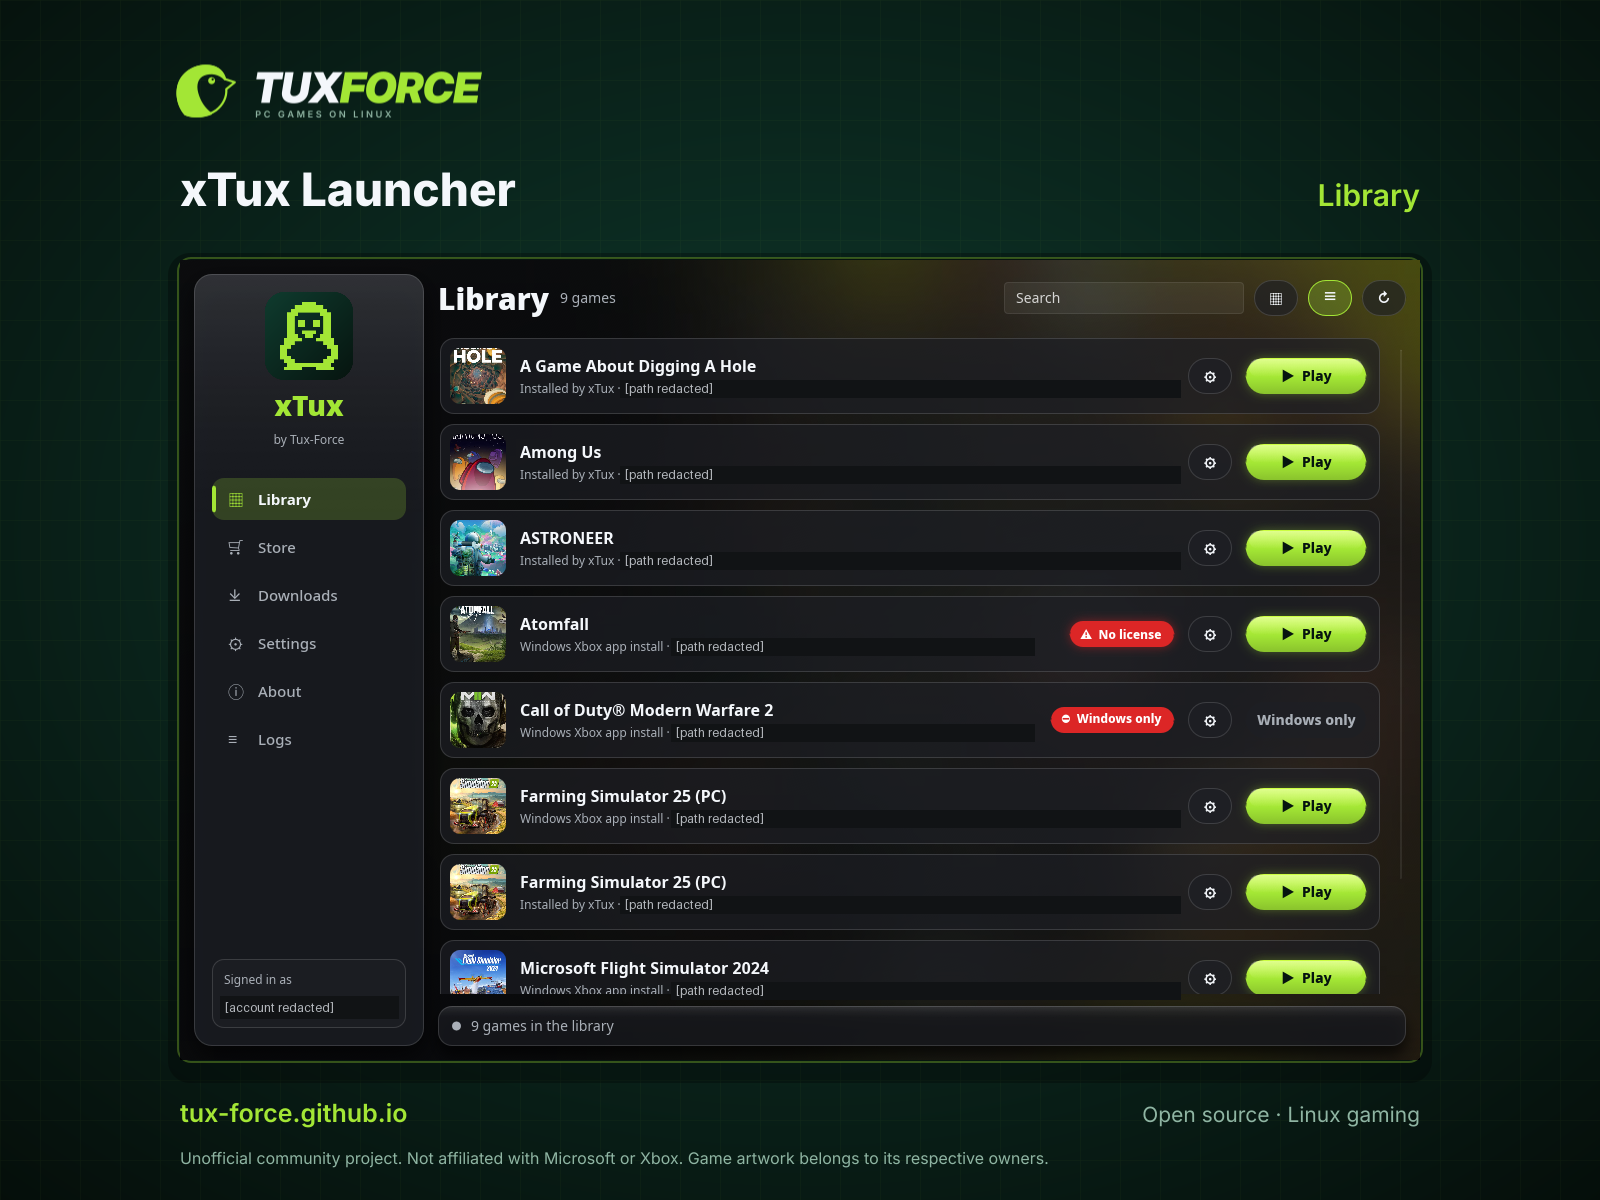
Alt...
Bibliothek Ansicht: xTux Launcher im grünen Tux-Force-Design. Der Store zeigt Spielcover und Filter für Game Pass, gekaufte und installierte Spiele
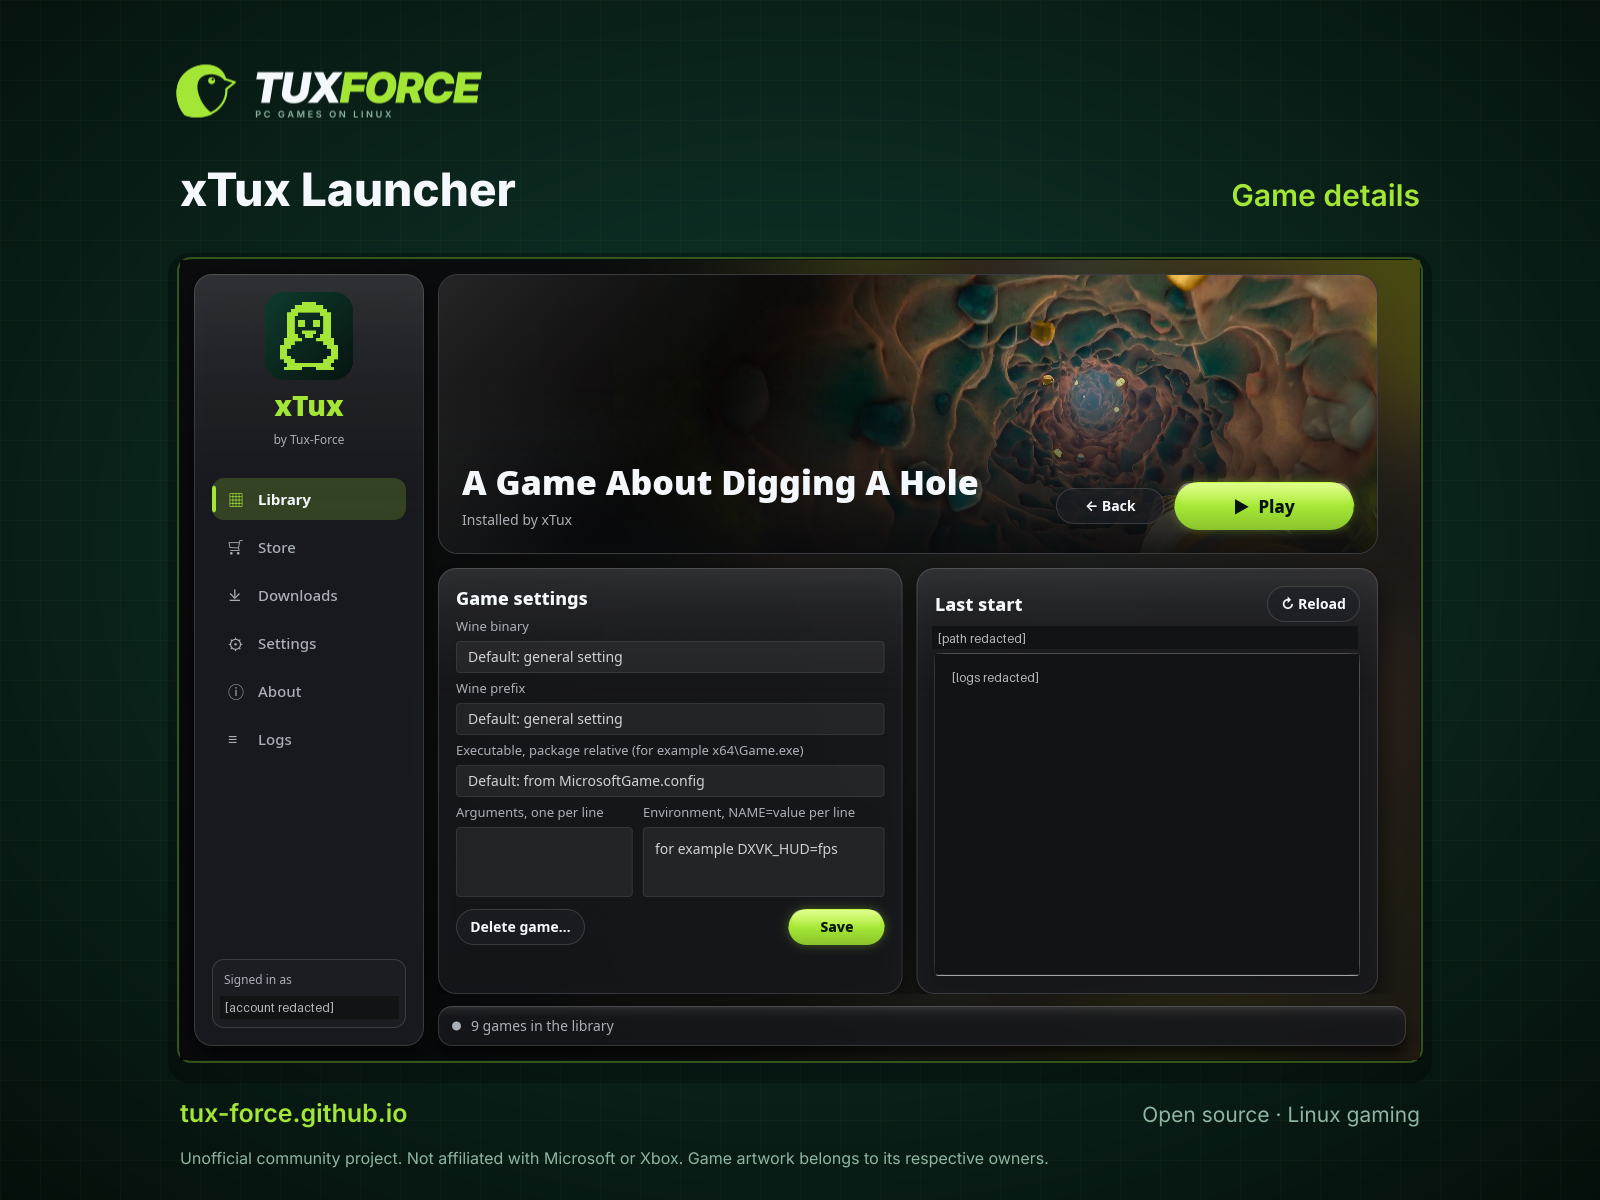
Alt...
Game Details Ansicht: xTux Launcher im grünen Tux-Force-Design. Der Store zeigt Spielcover und Filter für Game Pass, gekaufte und installierte Spiele
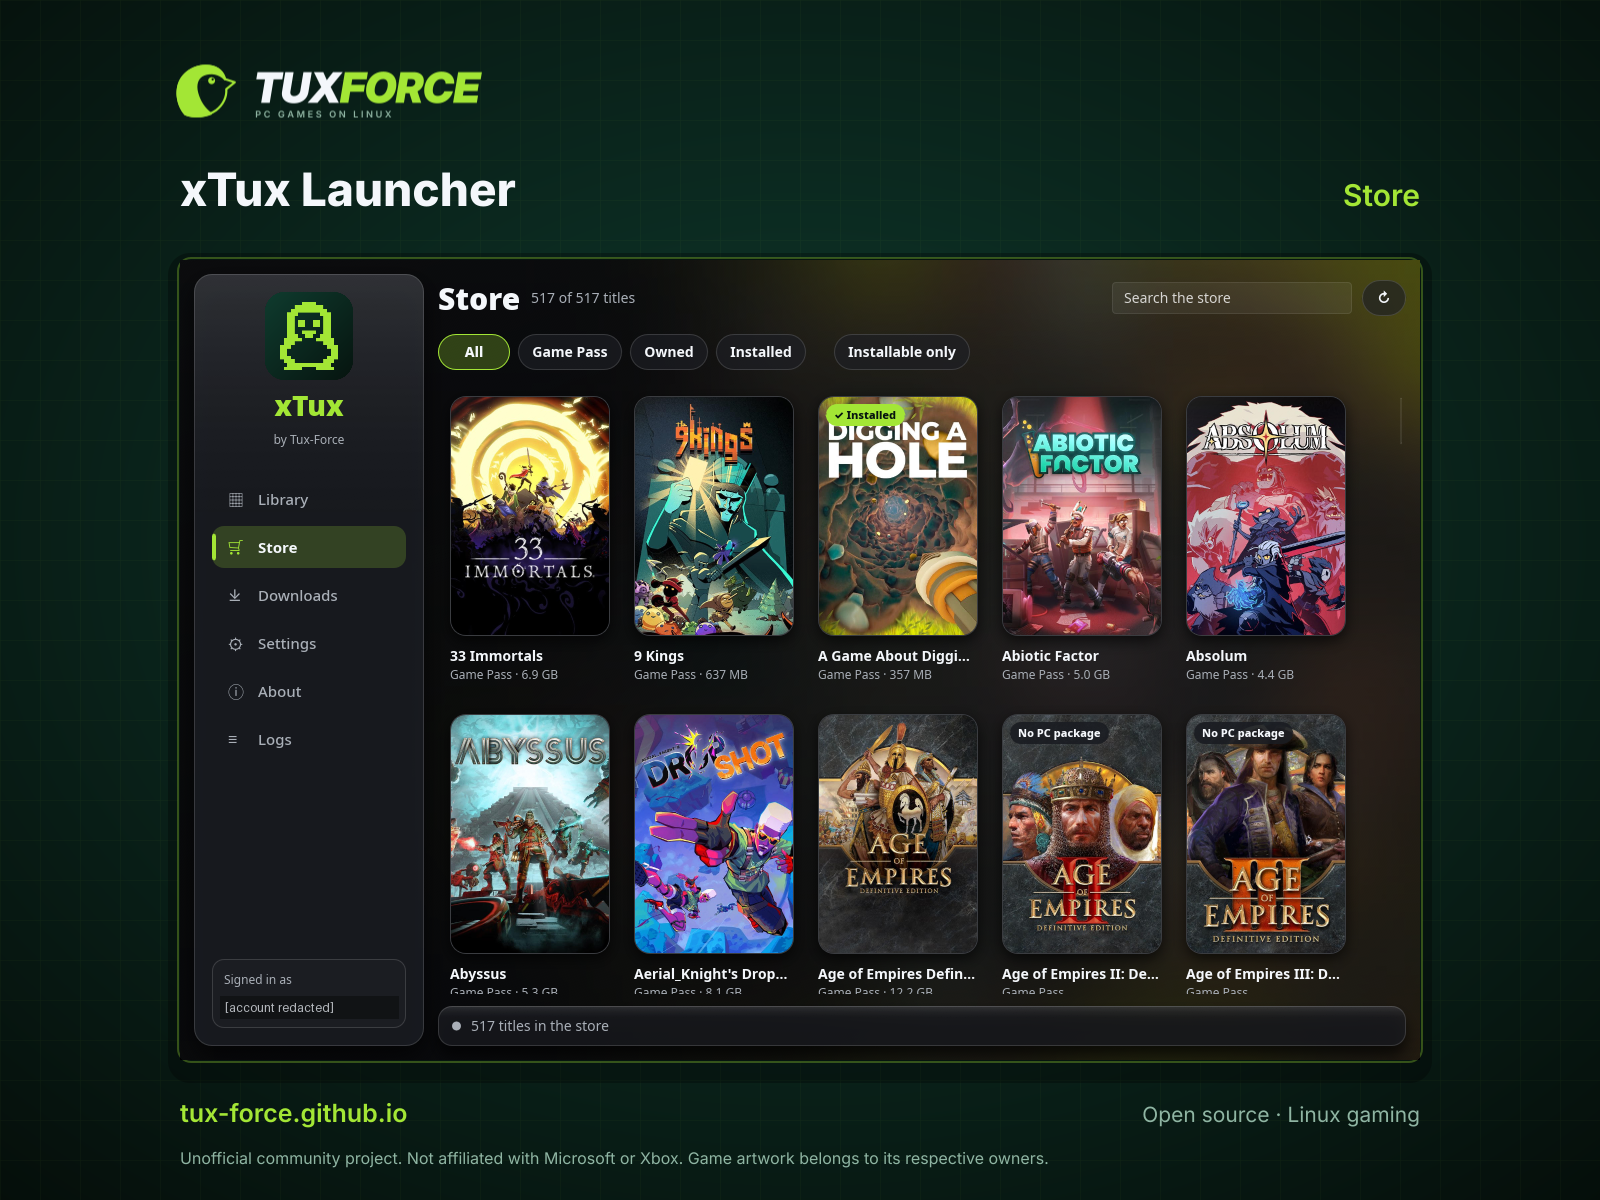
Alt...
Store Ansicht: xTux Launcher im grünen Tux-Force-Design. Der Store zeigt Spielcover und Filter für Game Pass, gekaufte und installierte Spiele

Wenn mein Freund Professor Harald Wehnes das sagt, was wir alle hier seit Jahren predigen tut das so gut.
"Wir nutzen Brücken die jedes Jahr einstürzen" - "Es war eine Misskonfiguration, kein Hack" - "Wiederholt"
#opensource #linux #microsoft #DigitaleSouveränität
https://www.br.de/radio/live/bayern2/programm/2026-11-13/3736746/#t=17:08:41
Manjaro-Projekt hat gemeinnützigen Verein gegründet
Die letzten Monate wurde diskutiert, jetzt Nägel mit Köpfen gemacht: Das Manjaro-Projekt kommt unter die Fittiche eines gemeinnützigen Vereins, der letzte Woche offiziell mit Sitz in Berlin…
https://www.linux-magazin.de/news/manjaro-projekt-hat-gemeinnuetzigen-verein-gegruendet/
#KI #AI #linux #opensource #Manjaro #gemeinnützigenVerein #Distribution
Alt...
Türkisfarbenes, abgerundetes Quadrat mit einem weißen, stilisierten geometrischen Zeichen.
Microsoft’s outage shows the importance of digital sovereignty, Canonical’s infrastructure struggles again, Ubuntu’s kernel fixes aren’t fast enough for some people but a firehose of AI updates is available, Anthropic’s Mythos was all hype, Asahi is moving to copyleft, and moving files to and from a Steam Frame.
https://latenightlinux.com/late-night-linux-episode-412/
Alt...
Late Night Linux artwork
GTA V: Simulation für die Klimaforschung
Grand Theft Auto V, eines der bekanntesten Videospiele der Welt, spielt im fiktiven Los Santos, dessen landschaftliche und städtebauliche Struktur Los Angeles nachempfunden ist.
https://www.linux-magazin.de/news/gta-v-simulation-fuer-die-klimaforschung/
#linux #opensource #GTAV #LosSantos #Klimaforschung
Alt...
Weißes „LINUX MAGAZIN“-Logo mit orangefarbenem „ONLINE“-Balken auf schwarzem Hintergrund.
We put our SIEM plumbing on GitHub, MIT-licensed: a dependency-free Python client, a Splunk lookup, Sentinel playbook steps, Elastic alert enrichment and an OpenAPI 3.1 spec.
One detail we nearly got wrong: the API returns indicators lowercased, so matching results on the raw input quietly loses the verdict for something like Evil.Example.COM. The client handles it.
https://github.com/reputio-dev/reputio-integrations
Write-up: https://www.reput.io/blog/open-source-integrations-and-openapi
Zweiteiliges Webinar: Verteidigung gegen php2shell & Co mit Wazuh
Mit Wazuh lassen sich Logs auswerten, aber auch ungestopfte Sicherheitslücken erkennen. Unser zweiteiliges Webinar zeigt, wo das Opensource-Werkzeug hilft.
AerynOS aktualisiert Kernel, Grafiktreiber und Systembasis
https://linuxnews.de/aerynos-aktualisiert-kernel-grafiktreiber-und-systembasis/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #AerynOS #Kernel #LinuxKernel #OpenSource

E-Rechnungen erstellen mit #Mustang
Über ein Jahr Produktivbetrieb mit Mustang, einer Open-Source-Library für #ZUGFeRD-Rechnungen in #Java: Stärken, Stolperfallen und unsere Empfehlung.
Mehr Informationen dazu in unserem Blogpost:
https://www.erras-it.de/blog/2026/2026-11-17_e-rechnungen_mit_mustang_erstellen/

The open-source movement wants Jensen Huang back
https://www.technologyreview.com/2026/11/16/1148624/the-open-source-movement-wants-jensen-huang-back/
An open-source petition calls for Jensen Huang's reinstatement as Nvidia CEO following his detention by Chinese intelligence agents last week.
#mix #ai #opensource
I wrote about building Playroom, a self-hosted app for my Steam, PlayStation and Xbox games: the unofficial PSN API, Xbox Game Bar noise, and a hardened read-only container.
https://dev.to/hexguardsec/i-built-a-self-hosted-app-to-see-all-my-steam-playstation-and-xbox-games-in-one-place-81l
#selfhosted #homelab #opensource
Europa in der Microsoft Falle
„Selbst schuld“ – so was soll man nicht sagen. Der Ausfall von Microsofts Office 365 in der letzten Woche lässt aber keine andere Reaktion zu. Alle, die jetzt jammern, hätten es besser wissen müssen. Während alle empört nach Redmond zeigten, wiesen drei Finger auf sie zu zurück – auf Europas Trägheit und Feigheit.
In der letzten Woche konnten nicht nur viele deutsche Firmen nicht mehr arbeiten. In Australien waren der Geheimdienst und die Polizei lahmgelegt. In Großbritannien traf es das Gesundheitswesen. Der Ausfall von Servern von Microsoft hatte weltweit katastrophale Auswirkungen.
Nun ist die Panne behoben. Ihre Folgen werden jetzt schon verdrängt. Bis zum nächsten Mal. Manche ignorieren es vorsätzlich. Wenige Tage vor dem Crash hatte die deutsche Heinrich Böll Stiftung ihre Systeme wieder komplett auf Microsoft umgestellt. Die Stiftung sie sollte es besser wissen. Sie arbeitet regelmäßig mit Oppositionellen und Nichtregierungsorganisationen in unzähligen autoritären Ländern zusammen. Diese müssen vor vor digitaler Überwachung geschützt werden.
Dabei wäre Zeit zu handeln. Es ist überfällig, dass sich Europa aus der digitalen Abhängigkeit der US-Techkonzerne befreit.
Ich habe leicht reden. Bei mir hat die Microsoft-Panne ein müdes Schulterzucken ausgelöst. Mail, Messenger, Videokonferenzen liefen. Als vor über zehn Jahren MS Office nach jedem Update erneut versuchte, meine Dokumente und Präsentationen auf die Microsoft-Cloud zu schieben, hatte ich es auf meinen Rechnern wie Handy und Tablet deinstalliert.
Seit Corona habe ich Linux Mint als Betriebssystem auf meinen Rechnern. Merkwürdigerweise ist To Do als einziges Programm aus dem Hause Microsoft noch auf meinem Handy. Zeit, es durch Tasks oder Joplin zu ersetzen. In unserem Haushalt läuft nur noch das Notebook meiner Frau unter Windows.
Als Autor und Redner schreibe ich viel. Gelegentlich fertige ich Präsentationen. In den letzten zehn Jahren habe ich MS Office nicht einmal vermisst. Obwohl es mich zuvor 30 Jahre begleitet hatte. Ich war für die Beschaffung von Word und Outlook in der grünen Landtagsfraktion verantwortlich. Ich habe damit als Bundesumweltminister wie als Bundestagsabgeordneter gearbeitet. Es sind gute Programme, intuitiv zu bedienen. Ihre Dominanz im Softwaremarkt geht auf ihre hohe Nutzerfreundlichkeit zurück. So wurden DOCX, PPTX und XLSX zu Standardformaten der digitalen Welt.
Doch seit Nine Eleven 2001 stand der Nutzerfreundlichkeit ein großes Aber entgegen. Mit dem verabschiedeten Patriots Act hat die US-Regierung das Recht, von jedem US-Unternehmen die Herausgabe der bei ihnen gespeicherten Daten zu verlangen. Das gilt auch für die europäischen Töchter von US Firmen – wie diese in Anhörungen vor dem französischen Senat bestätigten. Es nützt also nichts, wenn die Rechenzentren von Microsoft, Google, Amazon und Co in Europa stehen und sie dort ihre europäischen Daten speichern. Im Zweifel müssen sie die US-Behörden darauf zugreifen lassen.
Das konnten Microsoft-Nutzer so lange ignorieren, wie sie ihre Office-Dateien und Mails nur auf ihren Rechnern und Servern speicherten. Seit der Umstellung von Office 365 samt Outlook auf ein Cloud basiertes System ist das vorbei.
Es bedarf beharrlicher Arbeit, um zu verhindern, dass Dateien auf den Servern vom Microsoft landen. Besonders gravierend fiel die Umstellung bei Outlook aus. In der Standardeinstellung wird jede Mail auf der Cloud von Microsoft gespiegelt. Wer mit Office 365 kollaborativ arbeiten möchte, landet fast zwangsweise auf der Cloud von Microsoft, bei Teams sowieso.
Es gibt Menschen, denen egal ist, was mit ihren Daten passiert. Auch wenn manche das bei der Einreise in die Trump-USA schon bitter bereut haben. Aber es ist ihr Risiko, es sind ihre Daten.
Anders verhält es sich mit Behörden, Verwaltungen und Firmen. Sie verarbeiten die Daten Dritter. Sie müssen diese Daten schützen – auf der Basis des europäischen Rechts. Mit ihm ist der Patriots Act unvereinbar. Die Speicherung von Bürgerdaten auf Servern, die dem Kriegsrecht der USA unterliegen, ist rechtswidrig und gefährlich.
Die USA spionieren nicht nur. Sie sanktionieren auch – unter Missachtung des Völkerrechts. In Trumps und Rubios Kampf gegen den Internationalen Strafgerichtshof verhängten sie Sanktionen. Die Richterinnen und Richter haben nicht nur keine Kreditkarten mehr. Das Gericht wurde von der Nutzung von MS Office abgehängt.
Diese Gefahren werden in Deutschland vorsätzlich ignoriert. Da lässt Niedersachsen die Bodycam-Bilder seiner Polizisten bei AWS – also bei Amazon – speichern. Unzählige Behörden mailen mit Outlook und schreiben mit Word. Will mich ein Unternehmen zu einer Videokonferenz einladen, wird wie selbstverständlich ein Teams-Link verschickt.
Der Serverausfall bei Microsoft ist nur die letzte Mahnung. Hört auf zu jammern – nutzt die vorhandenen Alternativen.
Die gibt es – und je mehr Behörden und Unternehmen sie nutzen, umso billiger und komfortabler werden sie. Die Nutzung von Open-Source-Software und europäischen Servern ist keine Geheimwissenschaft. Städte wie Nettetal, Länder wie Schleswig-Holstein, Armeen wie das österreichische Bundesheer machen es vor.
Deutschland sollte nicht warten, bis es wie der Internationale Strafgerichtshof von den USA gezwungen werden, andere System zu nutzen. Das Gericht arbeitet heute mit Euro Office – einer deutschen Entwicklung.
Es ist Zeit umzustellen. Nicht heute, sondern gestern.
Nun weiß ich ob des Schreckens jeder Systemumstellung. „Never change a running system“ ist bittere Administratorenerfahrung. Doch hier geht es um den Schutz von anvertrauten Daten bei Behörden und Unternehmen. Bequemlichkeit ist keine Rechtfertigung für den Bruch geltenden Rechts.
Es geht aber um mehr. In Zeiten hybrider Angriffe aus Russland und offener Erpressung durch die USA geht es um europäische Souveränität. Wer die digitale Souveränität gegen chinesische Mobilfunkanbieter und Wechselrichter mit robusten Verboten verteidigt, darf nicht US-Konzernen den Zugriff auf die Daten europäischer Bürger, Firmen und Behörden erlauben.
Technologische Souveränität beginnt damit, die Daten der Europäer auf europäischen Servern und unter europäischem Recht zu verarbeiten. Der Microsoft-Crash hat daran noch einmal schmerzhaft erinnert. Er hat die Versäumnisse der Bundes- und Landesregierungen wie der EU-Kommission noch einmal unterstrichen.
Nun wird diese Bundesregierung nicht einmal aus Schaden klug. Die kölsche Lebensregel „Et hätt noch immer jot jejange“ funktioniert nur bis zum nächsten Crash. Wer davor handeln will, hat reichlich Alternativen. Die Nutzung von selbst gehosteten oder von europäischen Firmen gehosteten Clouds meist auf der Basis von Nextcloud ist das eine.
Die Nutzung anderer Office-Pakete das andere. Ich arbeite seit zehn Jahren mit Softmaker Office aus Nürnberg. Selbst zu Zeiten, als ich daneben noch Dateien auf den Bundestagsrechnern mit MS Office bearbeiten musste, gab es nie ein Kompatibilitätsproblem. Anders als MS Office ist es für alle Betriebssysteme, Linux, Windows, macOS, iOS, Android voll umfänglich verfügbar.
Softmaker Office kostet – aber weniger als MS Office. Gratis ist Libre Office – hat aber eine Nutzeroberfläche, mit der ich fremdele. Bedienerfreundlicher und ebenfalls gratis ist Only Office samt seiner Forks wie Euro Office oder Nextcloud Office. Diese läuft – inklusive PDF-Bearbeitung – auf allen Betriebssystemen und zum kollaborativen Arbeiten auf der Nextcloud.
Das Mailproblem beginnt nicht bei Outlook, sondern beim Server. Unternehmen haben eigene Mailserver und damit Kontrolle und Verantwortung. Eine Speicherung in der Microsoft Cloud bringt keinen Funktionsgewinn. Einzelnutzer sind gut beraten, auf Anbieter wie Posteo oder Proton zurückzugreifen. Posteo kostet einen Euro im Monat, dafür bleibt mensch von den Spamwellen kostenloser Anbieter verschont. Die Mails sind komplett Ende zu Ende verschlüsselt.
Weder unter Android noch unter iOS macht die Nutzung von Outlook Sinn. Die gelieferten Mailprogramme erfüllen ihren Zweck. Auf dem Desktop gibt es mit Thunderbird eine vollwertige Alternative, die auf allen Betriebssystemen wie auf dem Handy verfügbar ist. Als alter Outlook-Nutzer nutze ich unter Mint lieber Evolution und mir fehlt nichts.
Es gibt Alternativen – im Großen wie im Kleinen. Für mehr digitale, mehr europäische Souveränität gilt: Machen ist krasser als wollen, spart aber Jammern.
Dieser Beitrag ist eine Übernahme aus dem Blog des Autors, mit seiner freundlichen Genehmigung.
Über Jürgen Trittin:
 Unter der Kennung "Gastautor:innen" fassen wir die unterschiedlichsten Beiträge externer Quellen zusammen, die wir dankbar im Beueler-Extradienst (wieder-)veröffentlichen dürfen. Die Autor*innen, Quellen und ggf. Lizenzen sind, soweit bekannt, jeweils im Beitrag vermerkt und/oder verlinkt.
"Too big to fail? Die Kette sitzt in den Köpfen" ⛓️🧠
Warum (fast) alle trotz des #MS365 Ausfalls bei #Microsoft bleiben werden - schmerzhaft plausibel erklärt:
https://chaos.social/@leisefuxx/117628247432117036
😓
Diese m.E sehr gute Betrachtung von @leisefuxx endet jedoch nicht negativ, sondern enthält u.a. eine positive Erwähnung der @landesregierung : "Das nördlichste Bundesland ist am weitesten" 👏
Da freuen sich sicher @CIO und @dirkschroedter ! 👋
👉 Danke @artwiseways für den Hinweis auf den Blogbeitrag 🙂
#SchleswigHolstein #linux #OpenSource #digitalesouveränität #office #libreoffice #outlook #toobigtofail #mindset #sla #Risikomanagement
Hello Mastodon! 👋
Thought I'd introduce myself!
I'm Mike, living in North Yorkshire, UK. By day I'm a Church of England vicar, but this account is mostly for indulging my geeky side!
I'm a Linux enthusiast, running an OMV home server with Docker, Nextcloud, Home Assistant, Immich and various other bits and pieces. I've recently moved to a Jolla phone running Sailfish OS, and I'm enjoying exploring life beyond Android and Google.
I'm interested in open source, self-hosting, privacy and digital independence. I enjoy tinkering, learning new things and occasionally breaking stuff before figuring out how to fix it!
#Introduction #Introductions #Linux #SelfHosting #OpenSource #SailfishOS #Jolla #OpenMediaVault #Docker #HomeAssistant #Nextcloud #DeGoogle #Fediverse
You Can Now Install Euro-Office on Your Computer: Nextcloud Releases a Free Desktop App
Nextcloud released the free Nextcloud Office Desktop app for Windows, macOS and Linux on November 13, 2026. It is built on Euro-Office, a European project derived from the open-source code of the ONLYOFFICE office suite.


From my small corner of the web: Review: Flare puts Bluesky and the fediverse in one timeline
I spent tonight looking for one app for Bluesky and the fediverse, and found Flare. It's free, open source, and mixes Mastodon, Misskey, Bluesky, Nostr and RSS in a single timeline, on phones and on the desktop. The developers did an excellent job.
https://pablomurad.com/review-flare-bluesky-fediverse-one-timeline/
#fediverse #bluesky #mastodon #OpenSource

Alt...
Review: Flare puts Bluesky and the fediverse in one timeline
Pretty much 98% of the "tips" we're getting to LWN now are projects that have been largely cobbled together using LLMs. Probably 75% of the project tips are for things that have existed for all of a week and have like 1,000 commits over three days.
I really wish that projects that are entirely human-created and involve multiple people were as eager to promote themselves as the people prompting Claude who want to brag that they "made" something.
Perhaps LLM-driven development is inevitable. I hope not, but perhaps. But even if it is... LLM-first projects will never be as interesting as actual community driven projects with real human work behind them.
It's like the difference between knitting your own sweater or socks versus buying some. If you have made yourself some unique fiber art clothing, I'm down to hear about how you did it and to admire it. I might even be a bit jealous, because some hand-knit clothing is just absolutely gorgeous.
If it's store-bought, though? Congrats. You ... picked something out and paid for it. Nice. It might be worth a "oh, nice sweater" but you don't get bragging rights.


"FBI says Artex AI open source hacking tool used to breach networks in ‘under three hours’"
"IT giant and the South Korean financial industry. The FBI says that the open source hacking tool was used in cyberattacks targeting a U.S."
🚀 shlinker.app ist online!
Die Website steht, Deutsch und Englisch sind am Start – und die ersten Besucher sind auch schon da. Also … vor allem Bots (noch) 😄
Einmal bei Google angeklopft, Bing Bescheid gesagt, und schon steht das halbe Crawler-Internet vor der Tür. Immerhin.
Schaut gerne vorbei:
👉 https://shlinker.app
#Shlinker #Webdev #SelfHosting #IndieWeb #BuildInPublic #shlink #opensource #android
Bundeshaushalt:
Kein Moos für Open Source
https://netzpolitik.org/2026/bundeshaushalt-kein-moos-fuer-open-source/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Bundeshaushalt #KI #OpenSource

I submitted a Pull Request to update MacPorts' Game of Trees to 0.131 here:
https://github.com/macports/macports-ports/pull/36796
Continuous Integration checks: 1 passed, the other is queued.
Presumably the second one will complete OK?
It's up to someone else with commit access to merge it if so.
#GameOfTrees #Got #VersionControl #OpenSource #DVCS #VCS #Git
Debian 13: /tmp liegt plötzlich im RAM – was sich beim Upgrade ändert und welche Folgen das hat
https://www.zulauf-online.de/4138/debian-13-tmp-tmpfs-probleme-loesungen/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Debian #Debian13 #RAM #OpenSource
«OpenSSH - Linux — Lange Passwörter öffnen gesperrte Konten:
Über CVE-2026-123158 akzeptiert OpenSSH auf Alpine Linux ohne PAM jedes Passwort mit 257 bis 1.024 Zeichen. OpenSSH 10.6p2 und Alpine-Updates beheben das»
Schade dass OpenSSH nicht aus seiner Kritik weg kommt. Klar ist es nicht simpel doch gerade Passwörter sollte doch geprüft werden und nicht nur deren Mindestlänge und Zeichensatz.
🐧 https://www.it-daily.net/shortnews/linux-passwoerter-gesperrte-konten
#openssh #passwort #linux #itsicherheit #alpinelinux #update #opensource
A OnePlus 9 Pro running Arch Linux ARM instead of Android. Yes, that's a real project!
The developer has managed to get a mainline Linux 7.3 kernel running natively on the Snapdragon 888, with the Phosh mobile interface.
Quite a lot is already working:
🔹 GPU acceleration (Vulkan 1.3)
🔹 Wi-Fi, Bluetooth and NFC
🔹 LTE, VoLTE, SMS and MMS
🔹 GPS, audio and hardware video decoding
🔹 Partial camera support
Android apps can even run through Waydroid (Android 13).
⚠️ This is an experimental project, not ready for everyday use. There's no prebuilt image or installer. You must build the system yourself, and installation wipes the phone.
Only the T-Mobile LE2127 variant has been tested so far.
Seeing Linux run natively on a Snapdragon 888 smartphone is pretty impressive.
Would you switch from Android to a Linux-based mobile OS like Arch Linux ARM?
https://github.com/LuCiLuna/oneplus9pro-arch

Bei uns findet der »Digital Independence Day« 14tägig statt: Jeden zweiten Montag, in ungeraden Kalenderwochen, treffen wir uns ab 19 Uhr in den Räumlichkeiten der Recyclingbörse in Herford. Bei uns sind alle netten Menschen willkommen, die gerne mitdiskutieren und Neuigkeiten austauschen möchten oder einfach unsere Hilfe beim Umstieg brauchen.
Schaut auch gerne auf unserer Homepage vorbei: www.glughf.de
#glughf #linuxusergroup #herford #linux
#Linuxhilfe #freifunk
#foss #floss #opensource
#diday #di_day
@herfordtoots
#endof10

🚀 A new milestone for Parch Linux ARM64!
The first Parch ARM64 (Parch Mobile) image has been successfully built without relying on Arch Linux ARM images.
As the next step, we're preparing to release pootstrap (ParchBootStrap), a new tool designed to build custom Linux images for different SoCs and hardware platforms.
This is another step toward making Parch more independent, flexible, and adaptable to a wider range of devices.
More details and the first public release are coming soon!
#ParchLinux #ParchMobile #LinuxARM #ARM64 #MobileLinux #Linux #EmbeddedLinux #SoC #OpenSource #LinuxDevelopment
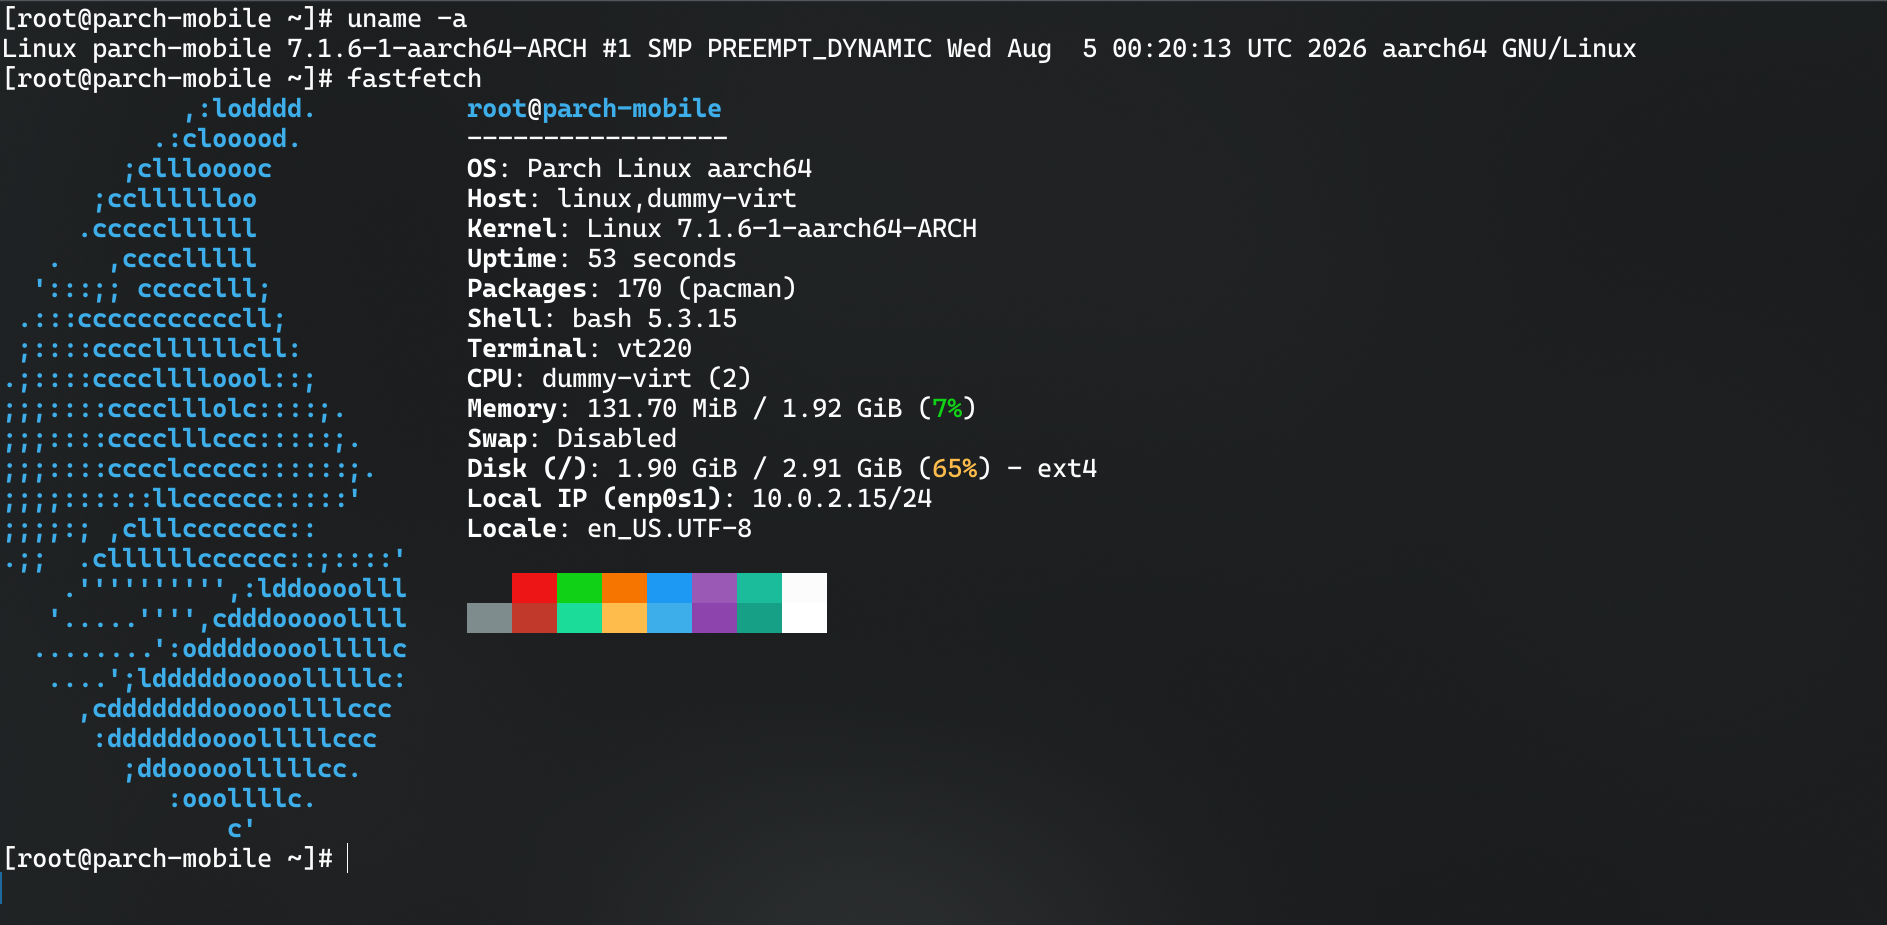
Alt...
Parch Linux Arm64 running in Qemu


We’re excited to share that Coop has been formally recognized as a Digital Public Good. 🎉
The Digital Public Goods Alliance has added Coop, our review and moderation tool, to the DPG Registry, alongside projects like @wikipedia and @openstreetmap.
KDE - Die Dokumentation
Wie kommt man dazu, eine Linux-Oberfläche zu entwickeln? Was sind die Schwierigkeiten auf dem Weg? Und war Qt böse?
Was mir sehr gefallen hat: Wie menschlich das alles ist. Da geht es nicht um Big-Business und Markt-Dominanz, sondern um eine gute Usererfahrung für die Menschen.
Schau es Dir an: https://peerseek.video/v/76dca815-c72e-49e3-af59-a6c3691865a1
Ubuntu Pro: KI-Sicherheitsupdates über neues Edge-Archiv
https://linuxnews.de/ubuntu-pro-ki-sicherheitsupdates-ueber-neues-edge-archiv/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Canonical #Ubuntu #UbuntuPro #KI #OpenSource
🚀 shlinker.app is online!
The website is available, German and English are at the start – and the first visitors are already there.
Once knocked on Google, Bing said, and already half the crawler Internet is at the door. After all.
Let's take a look:
https://shlinker.app
#Shlinker #Webdev #SelfHosting #IndieWeb #BuildInPublic #shlink #opensource
Daniel Stenberg zu 30 Jahre curl
Vor dreißig Jahren, am 11. November 1996, veröffentlichte der junge brasilianische Student Rafael Sagula den Quellcode für sein winziges HTTP-Download-Tool im Internet.
https://www.linux-magazin.de/news/daniel-stenberg-zu-30-jahre-curl/
#linux #opensource #curl #httpget #RafaelSagula #DanielStenberg
Alt...
Logo „curl“ in dunkelblauer Schrift, gefolgt von zwei Doppelpunkten und zwei schrägen, parallelen Linien in Dunkelblau und Dunkelgrün.

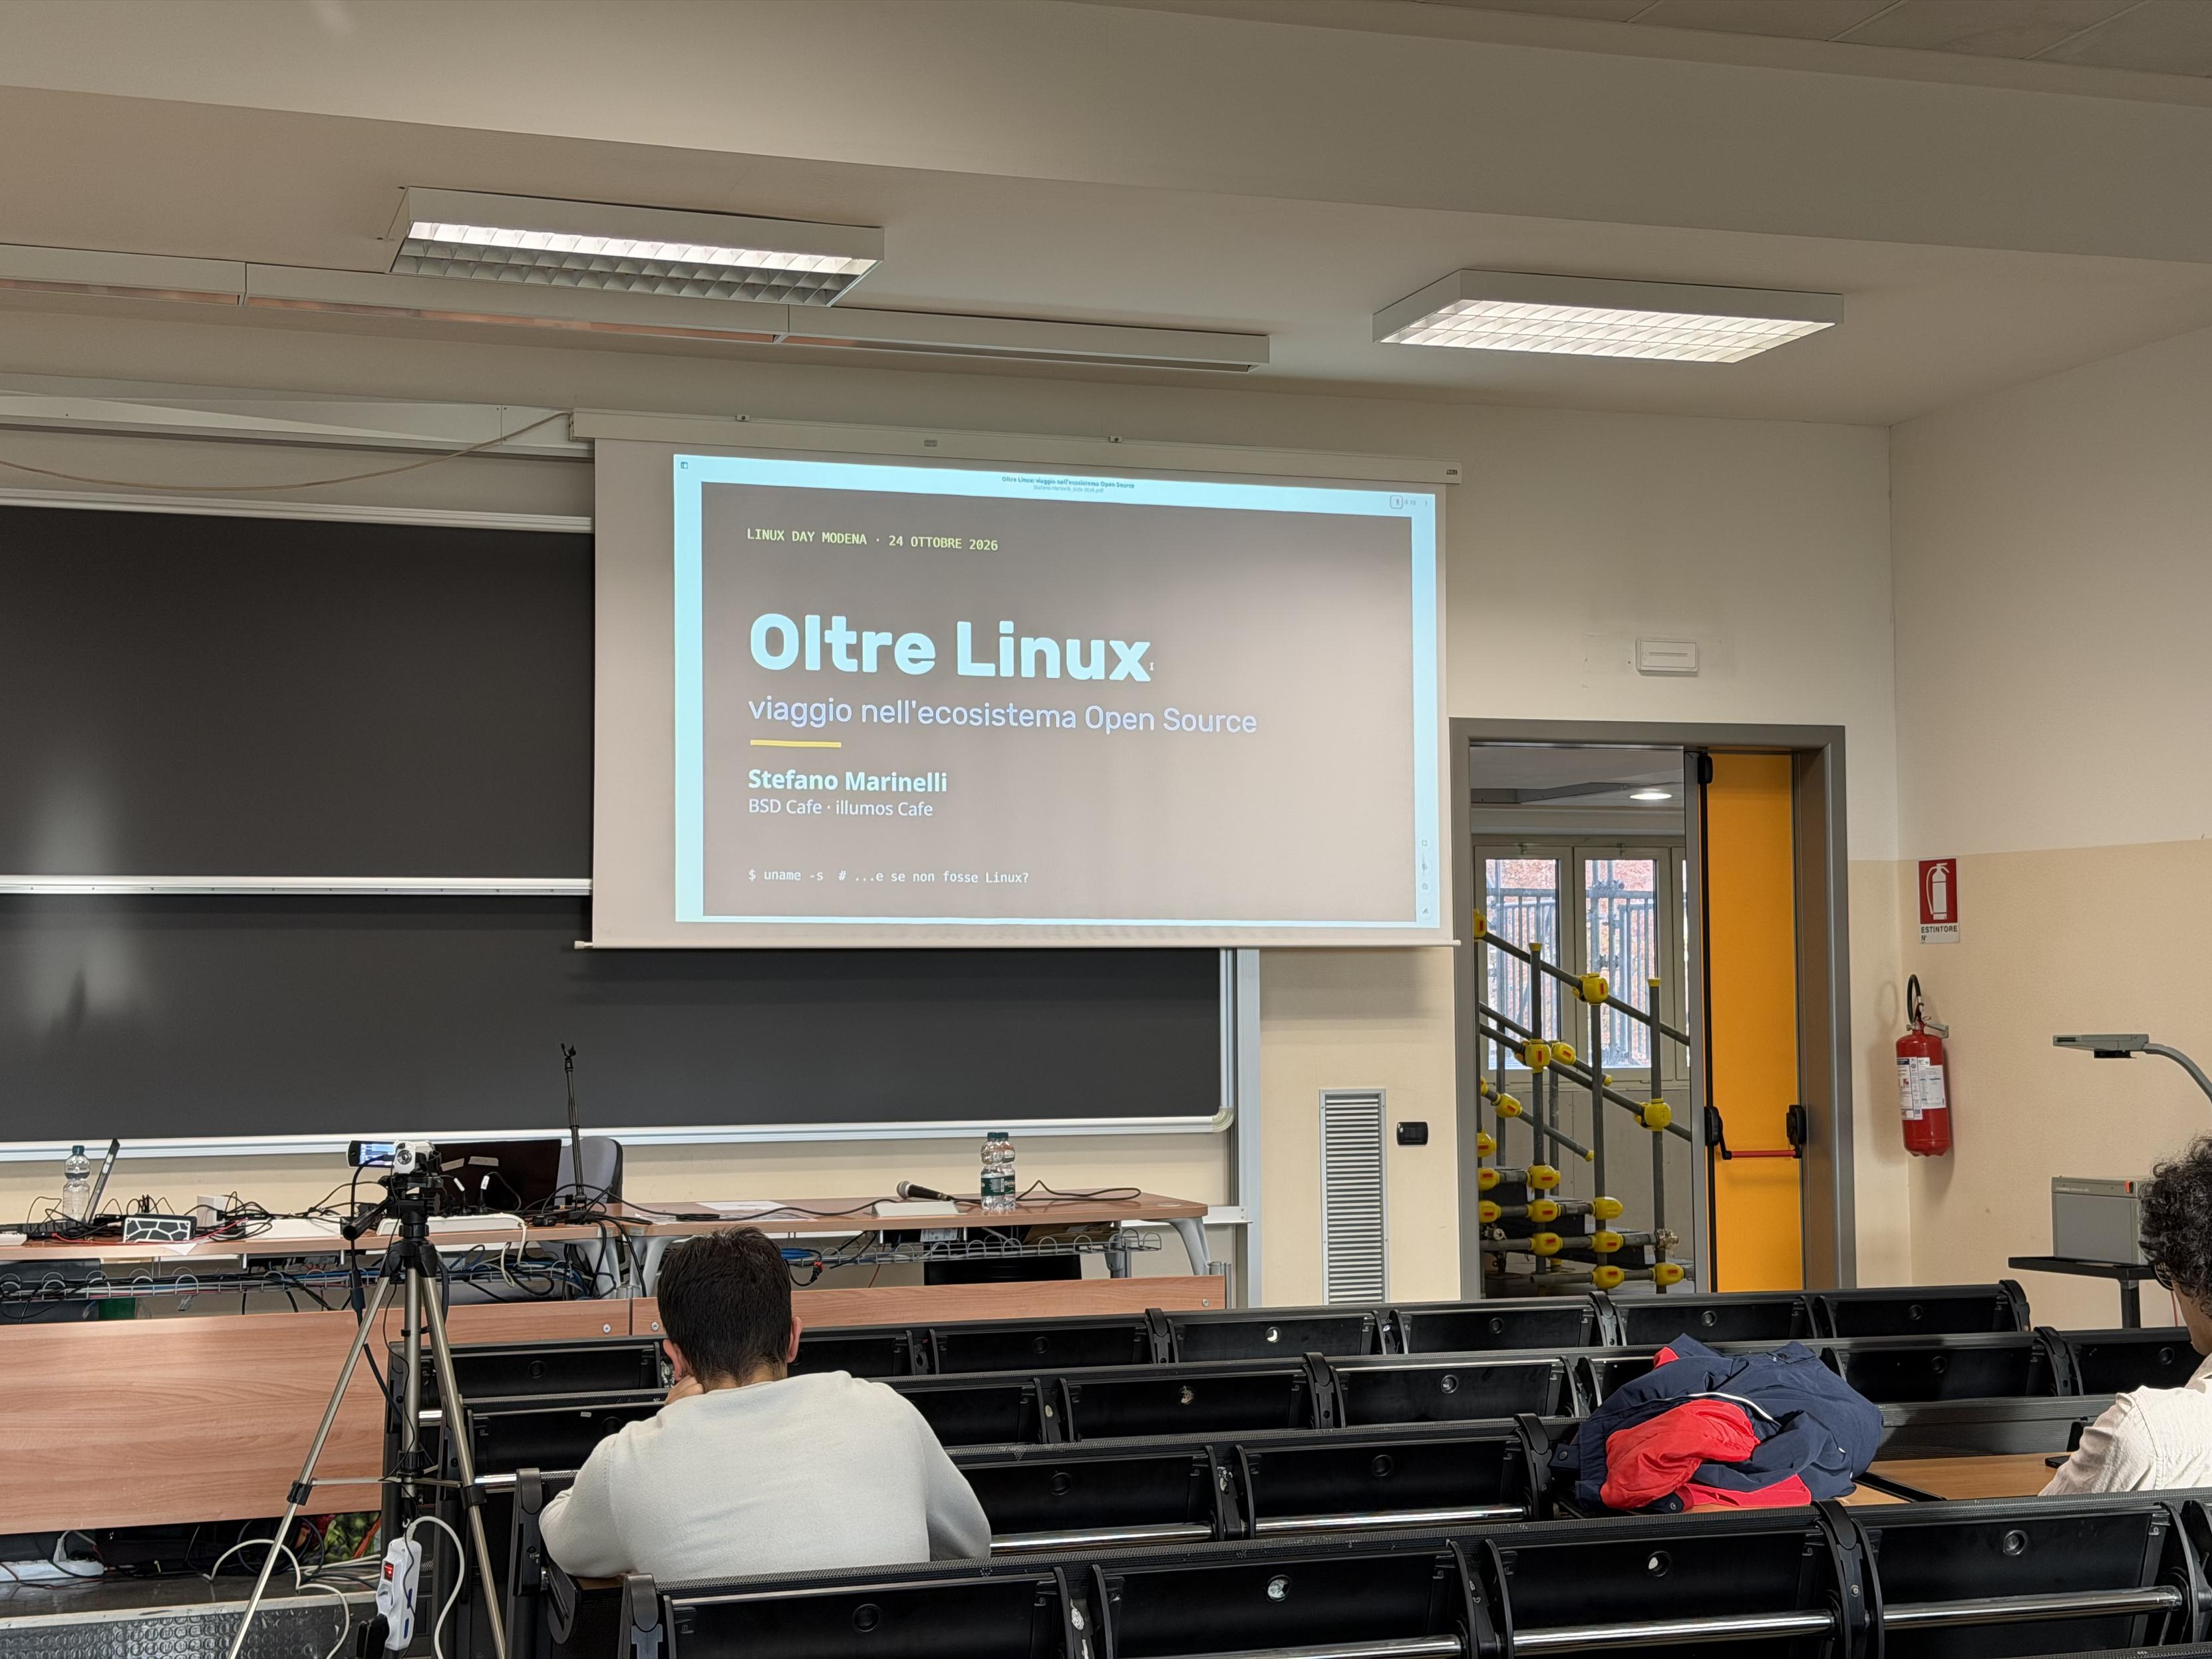
Getting the room ready before my talk at Linux Day 2026 in Modena, on 24 October: "Beyond Linux: A Journey Through the Open Source Ecosystem."
Tomorrow, on IT Notes!
#ITNotes #StayTuned #OwnYourData #AvoidMonoculture #FreeBSD #NetBSD #OpenBSD #illumos #RunBSD #Linux #OpenSource #FreeSoftware #BeFree
Alt...
A university lecture hall in Modena, Italy, shortly before a Linux Day 2026. Rows of black seats face a large projection screen displaying the opening slide of Stefano Marinelli's talk, "Oltre Linux: viaggio nell'ecosistema Open Source" (Beyond Linux: A Journey Through the Open Source Ecosystem). A few attendees are seated while the room is being prepared, with a camera on a tripod, microphones, cables, and presentation equipment visible near the front. The atmosphere is quiet and informal, capturing the moments before the talk begins on 24 October 2026.
TuxTalk: Offline-Diktierfunktion für den Linux-Desktop
https://linuxnews.de/tuxtalk-offline-diktierfunktion-fuer-den-linux-desktop/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #TuxTalk #Diktierfunktion #OpenSource

🔎 Meet Vigilo: CERT-EU’s open-source harness for AI-assisted security reviews.
Rather than relying on a single AI agent, Vigilo brings specialised agents together to inspect code and live applications, compare findings and challenge potential false alarms. Where source code is available, it can even suggest patches for maintainers to review. 🛠️
Curious how it works? Take a look 👇
https://www.cert.europa.eu/blog/vigilo-open-source
DSA-Verstöße: Keine Transparenz in Werbearchiven
Social Media-Plattformen und Online-Marktplätze müssen ein Archiv vorhalten, in dem jede ausgespielte Werbeanzeige mindestens für die letzten zwölf Monate gespeichert wird.
https://www.linux-magazin.de/news/das-verstoesse-keine-transparenz-in-werbearchiven/
#linux #opensource #DSAVerstöße #Transparenz #Werbearchive #SocialMediaPlattformen
Alt...
Logo der Verbraucherzentrale Bundesverband: weißes V in einem roten Kreis neben dem Schriftzug „Verbraucherzentrale Bundesverband“.

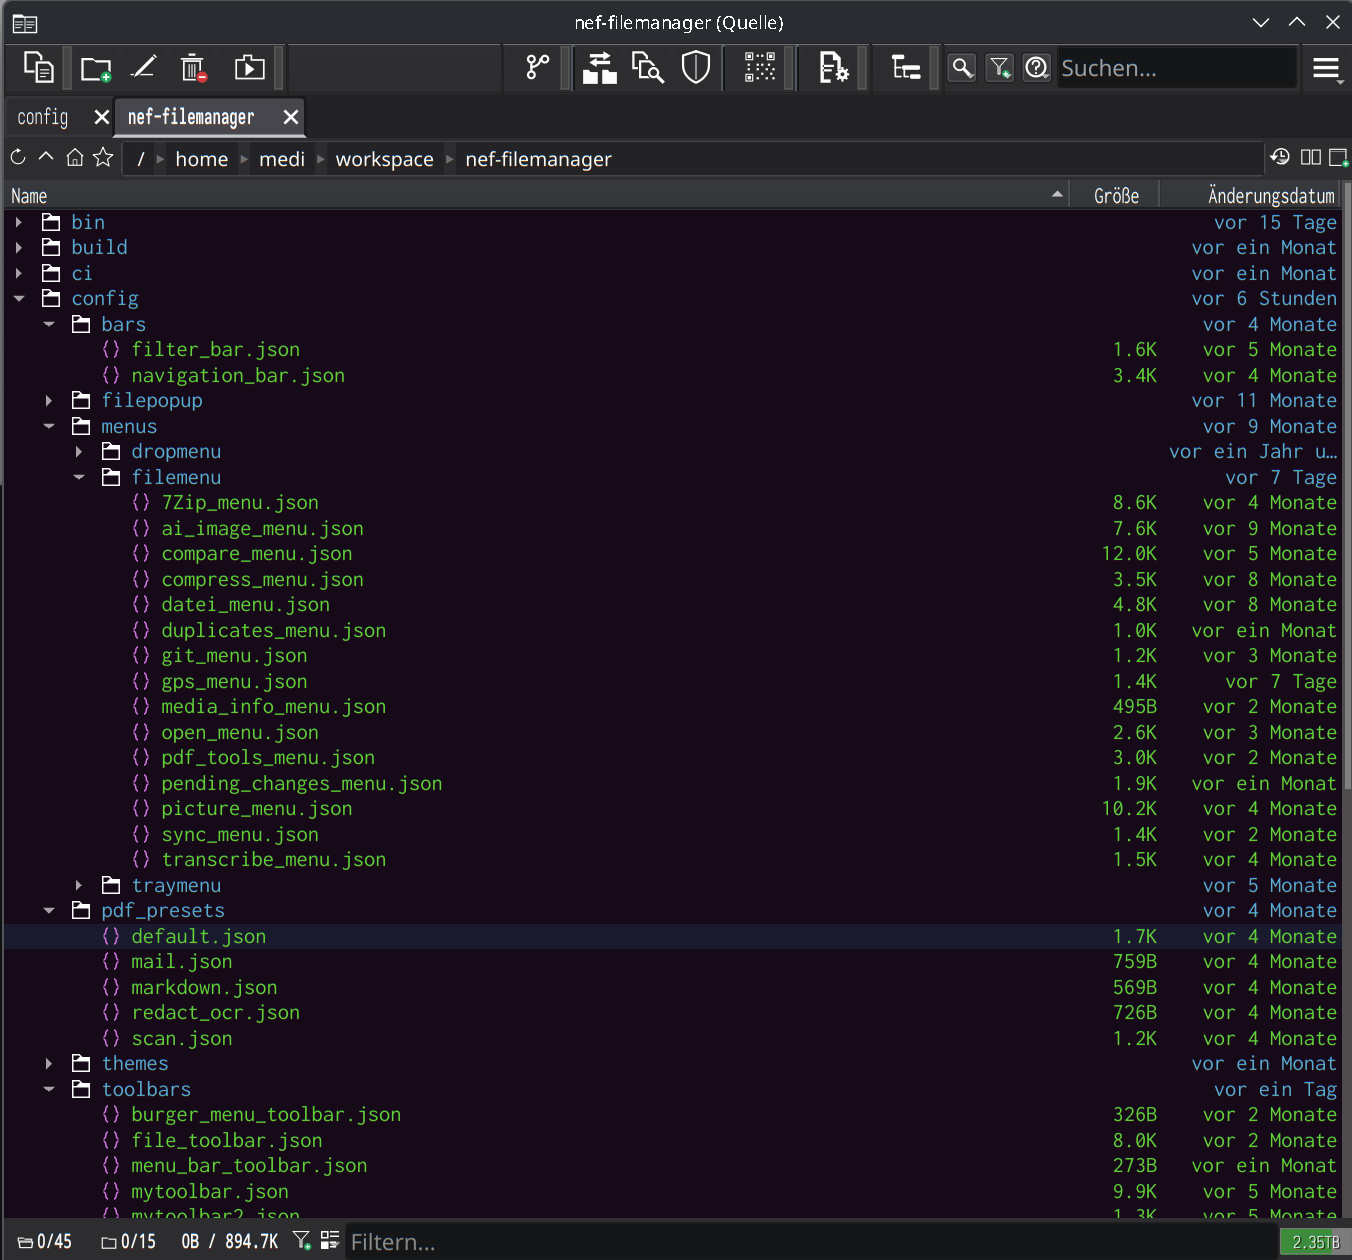
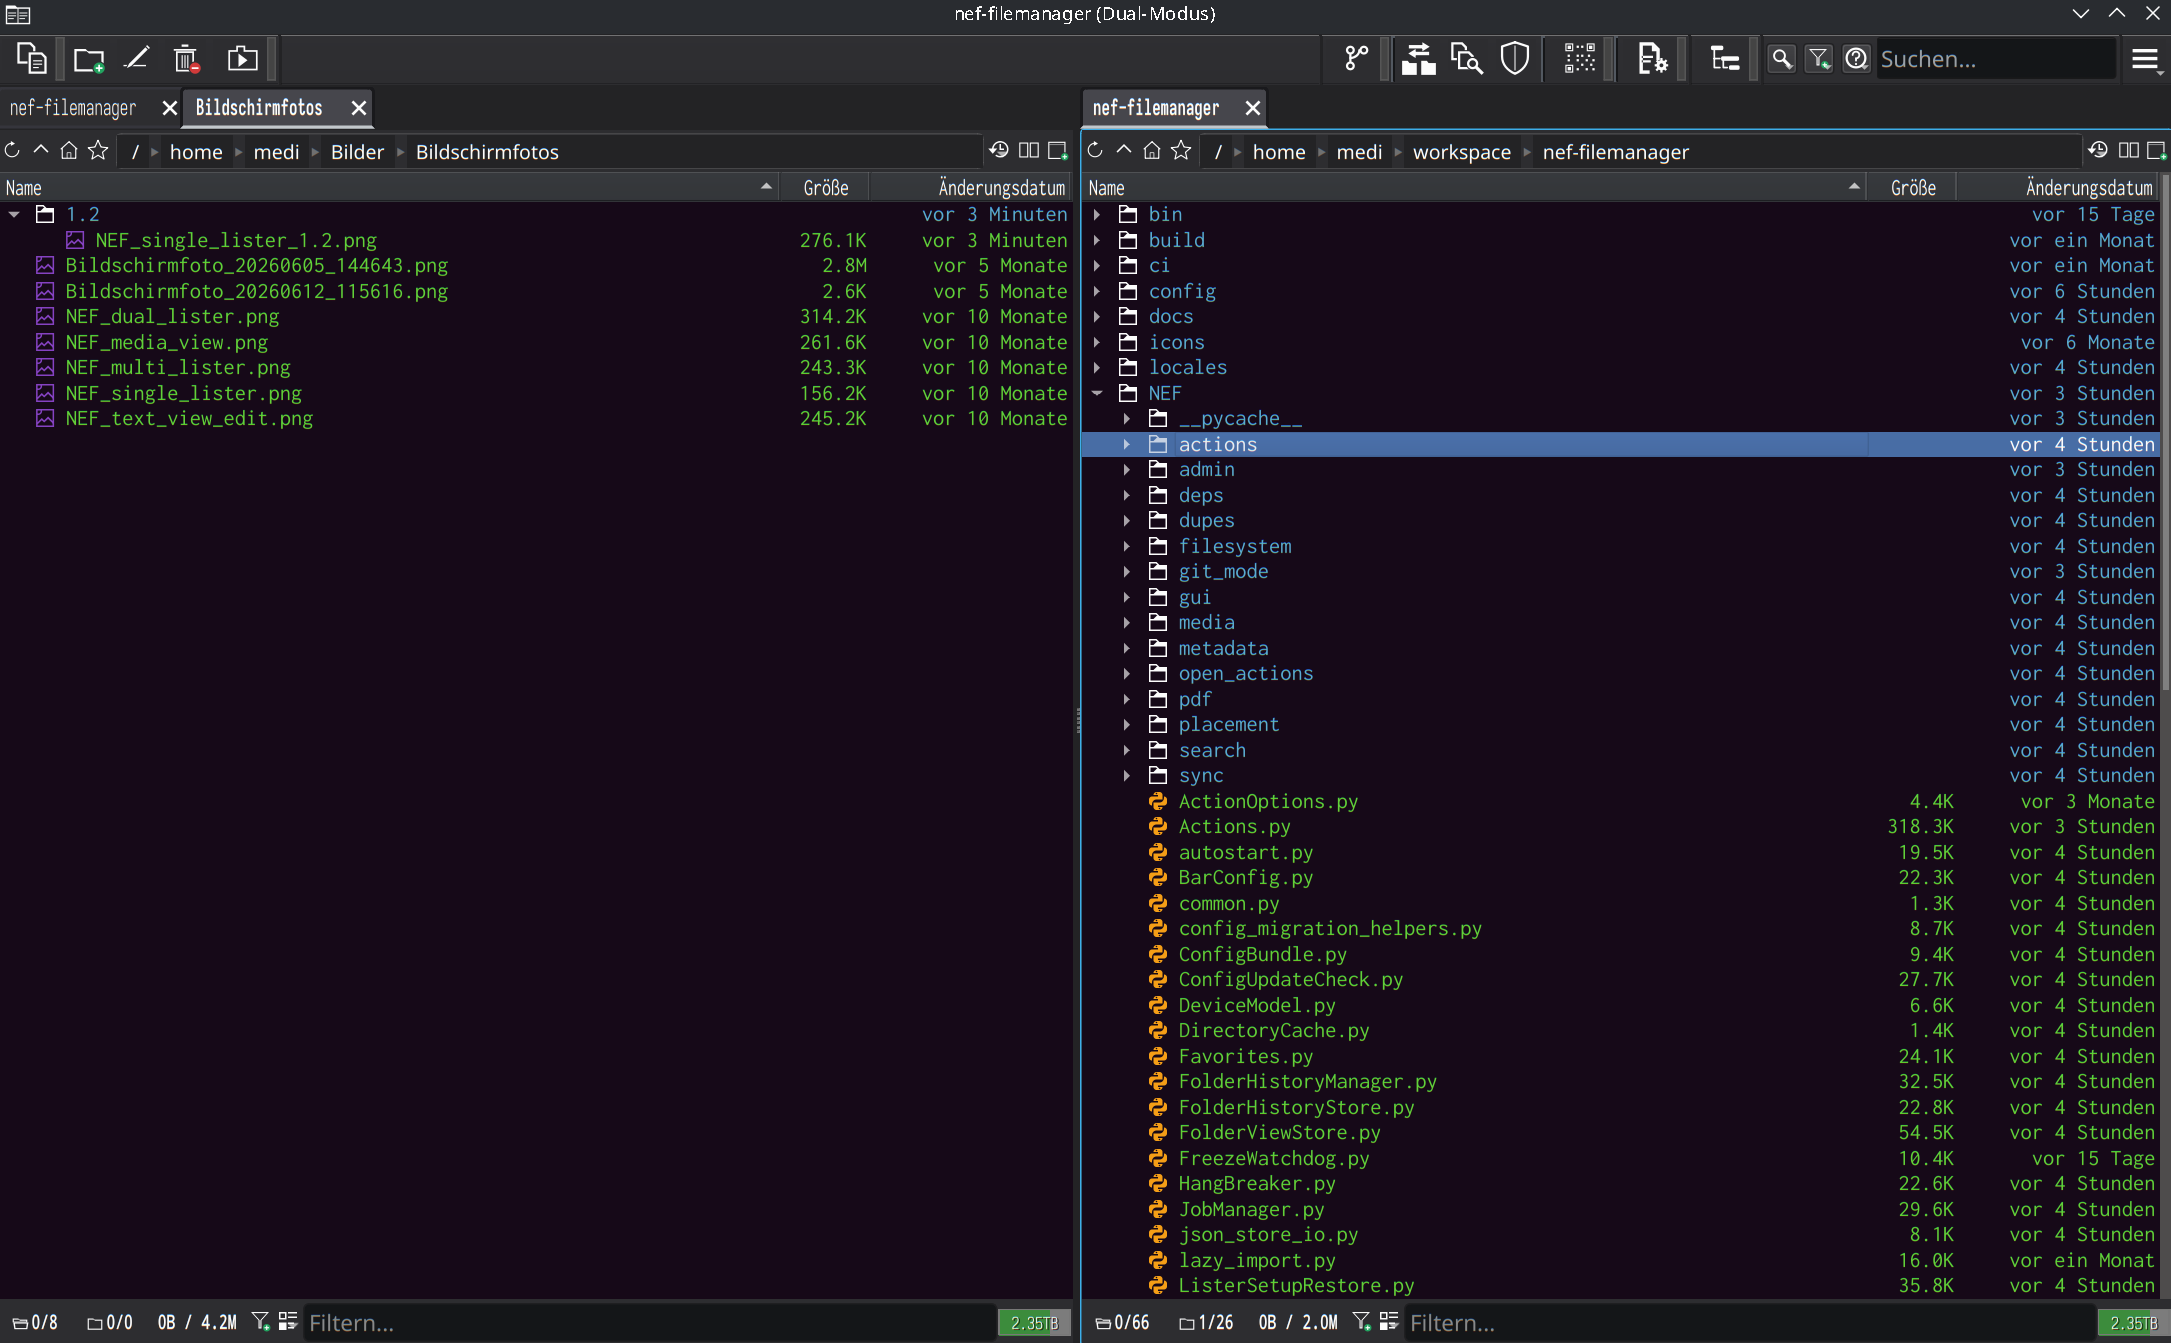
NEF File Manager 1.2 ist da! 🎉
Neu u. a.:
• Admin-Modus: ein Lister bekommt für eine Weile Root-Rechte
• Markdown- & Mermaid-Vorschau
• Flat View: Dateien aus allen Unterordnern in einer Liste
• PDF: Text markieren, durchsuchen, auf Seitenbreite zoomen
• Oberflächensprache in den Einstellungen wählbar
• Viele Fixes, besonders für Windows
https://codeberg.org/mEDI/nef-filemanager
#NEF #FileManager #Linux #OpenSource #Python #PyQt6
heise+ | Adblocker inklusive: DNS-Server #Technitium installieren und einrichten | c't Magazin https://www.heise.de/ratgeber/Adblocker-inklusive-DNS-Server-Technitium-installieren-und-einrichten-11439401.html #OpenSource #heiseplus #Adblock #DNS #Linux  #Docker
I have received the last prototypes of FramePico2 Expansion Card and its peripheral sensors at home today. This, along with our screwless 3D case for the card, will be the first and humble products of @riscfruit
Professional photos inside 3D case and @crowdsupply campaign coming soon!
#opensource #crowdsupply #risc_v #riscv #framework


🚀 Chronivaro 0.8.0 has been released!
Chronivaro is an open-source working time, absence tracking, and monthly period closing system.
📦 Release notes & downloads:
https://github.com/eitch/Chronivaro/releases/tag/v0.8.0

When I launched Cava Reader I said it was my first closed-source project. The app still is, but the part that does the actual cool stuff isn't anymore 
Meet CavaAlign v1. You give it a recording and its text, and it tells you when every single word is said. It's tiny, it's fast, and it's the model I made for read along in Cava Reader, and it's now open source! (under AGPL-3.0)
One 16 MB file, 35 languages, it can run on a phone's CPU. Numbers are in the image attached, and yes, that's a 16 MB model next to a 378 MB and a 967 MB one, doing better than them, I double-checked lol
It's made for books, so footnotes and the "this is a LibriVox recording..." intros don't throw it off, it’s able to just skip them.
The old engine in Cava Reader needed a 40 MB download for every extra language except English (which was bundled). This one is 16 MB for all 35, and it ships inside the app binary, the size of the whole app is a smaller size too
The model weights, a Python example aligner, a Kotlin port for Android, and a guide for mobile apps are all on Hugging Face so it’s easy to get started using it in your own projects:
https://huggingface.co/cava-reader/cavaalign-v1
It’s a standard ONNX model, so it runs anywhere the ONNX Runtime does: phones, desktops, servers, Raspberry Pis, and it should even run in a browser. No GPU needed, it's fully offline, and it handles recordings of any length with flat memory use. If you have audio and its text, it'll time every word.
if you build something with it, please show me!! <3
#OpenSource #MachineLearning #Accessibility #Audiobooks #AGPL #CavaAlign

Alt...
CavaAlign v1: word-level timing for any recording and its text. 16 MB, one file for 35 languages. 88.0% of English word starts within 50 ms, 0.3% more than 250 ms off or untimed. 86.7% within 50 ms averaged over all 35 languages.
Compared with other models (size, languages, within 50 ms, more than 250 ms off or untimed):
CavaAlign v1: 16 MB, 35 languages, 88.0%, 0.3%
wav2vec2-base (WhisperX): 378 MB, English, 84.4%, 0.4%
PocketSphinx: 10 MB, English, 83.8%, 8.6%
Vosk small-en: 71 MB, English, 80.4%, 12.7%
MMS-300m: 1.26 GB, 1,100+ languages, 77.0%, 7.2%
NeMo Conformer-CTC S: 46 MB, English, 67.3%, 5.7%
Whisper small.en: 967 MB, English, 48.3%, 10.8%
Benchmark: 70 LibriSpeech speakers, 12,195 English words, exact text given to every system, scored against Montreal Forced Aligner timings. Two independent reference alignments agree on 89.5% of words.

Wer von Outlook auf #Thunderbird umsteigt, vermisst die Kalender der Kollegen nebeneinander. Dafür gibt's jetzt TeamKalender – ein freies Add-on (MPL 2.0):
📅 Team- & Raumkalender nebeneinander oder als Zeitplan
🔎 Freie Zeit finden, auch mit Raum
🎥 Vorschau mit Teilnehmen-Button
🎨 Outlook-Look
Für #Nextcloud, #Mailcow & jeden #CalDAV-Server. Beta zum Testen:
https://github.com/Stefan2706/teamkalender
Ubuntu baut Zertifikatsprüfung mit Rust-Technologie aus
https://fosstopia.de/ubuntu-rust-zertifikatsprufung/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Ubuntu #Rust #OpenSource
Firefox 160 erweitert Bild-in-Bild-Funktion
Mozilla hat Firefox 160 freigegeben.
https://www.linux-magazin.de/news/firefox-160-erweitert-bild-in-bild-funktion/
#linux #opensource #Firefox #Mozilla #BildinBild #MiniWindow #Browser
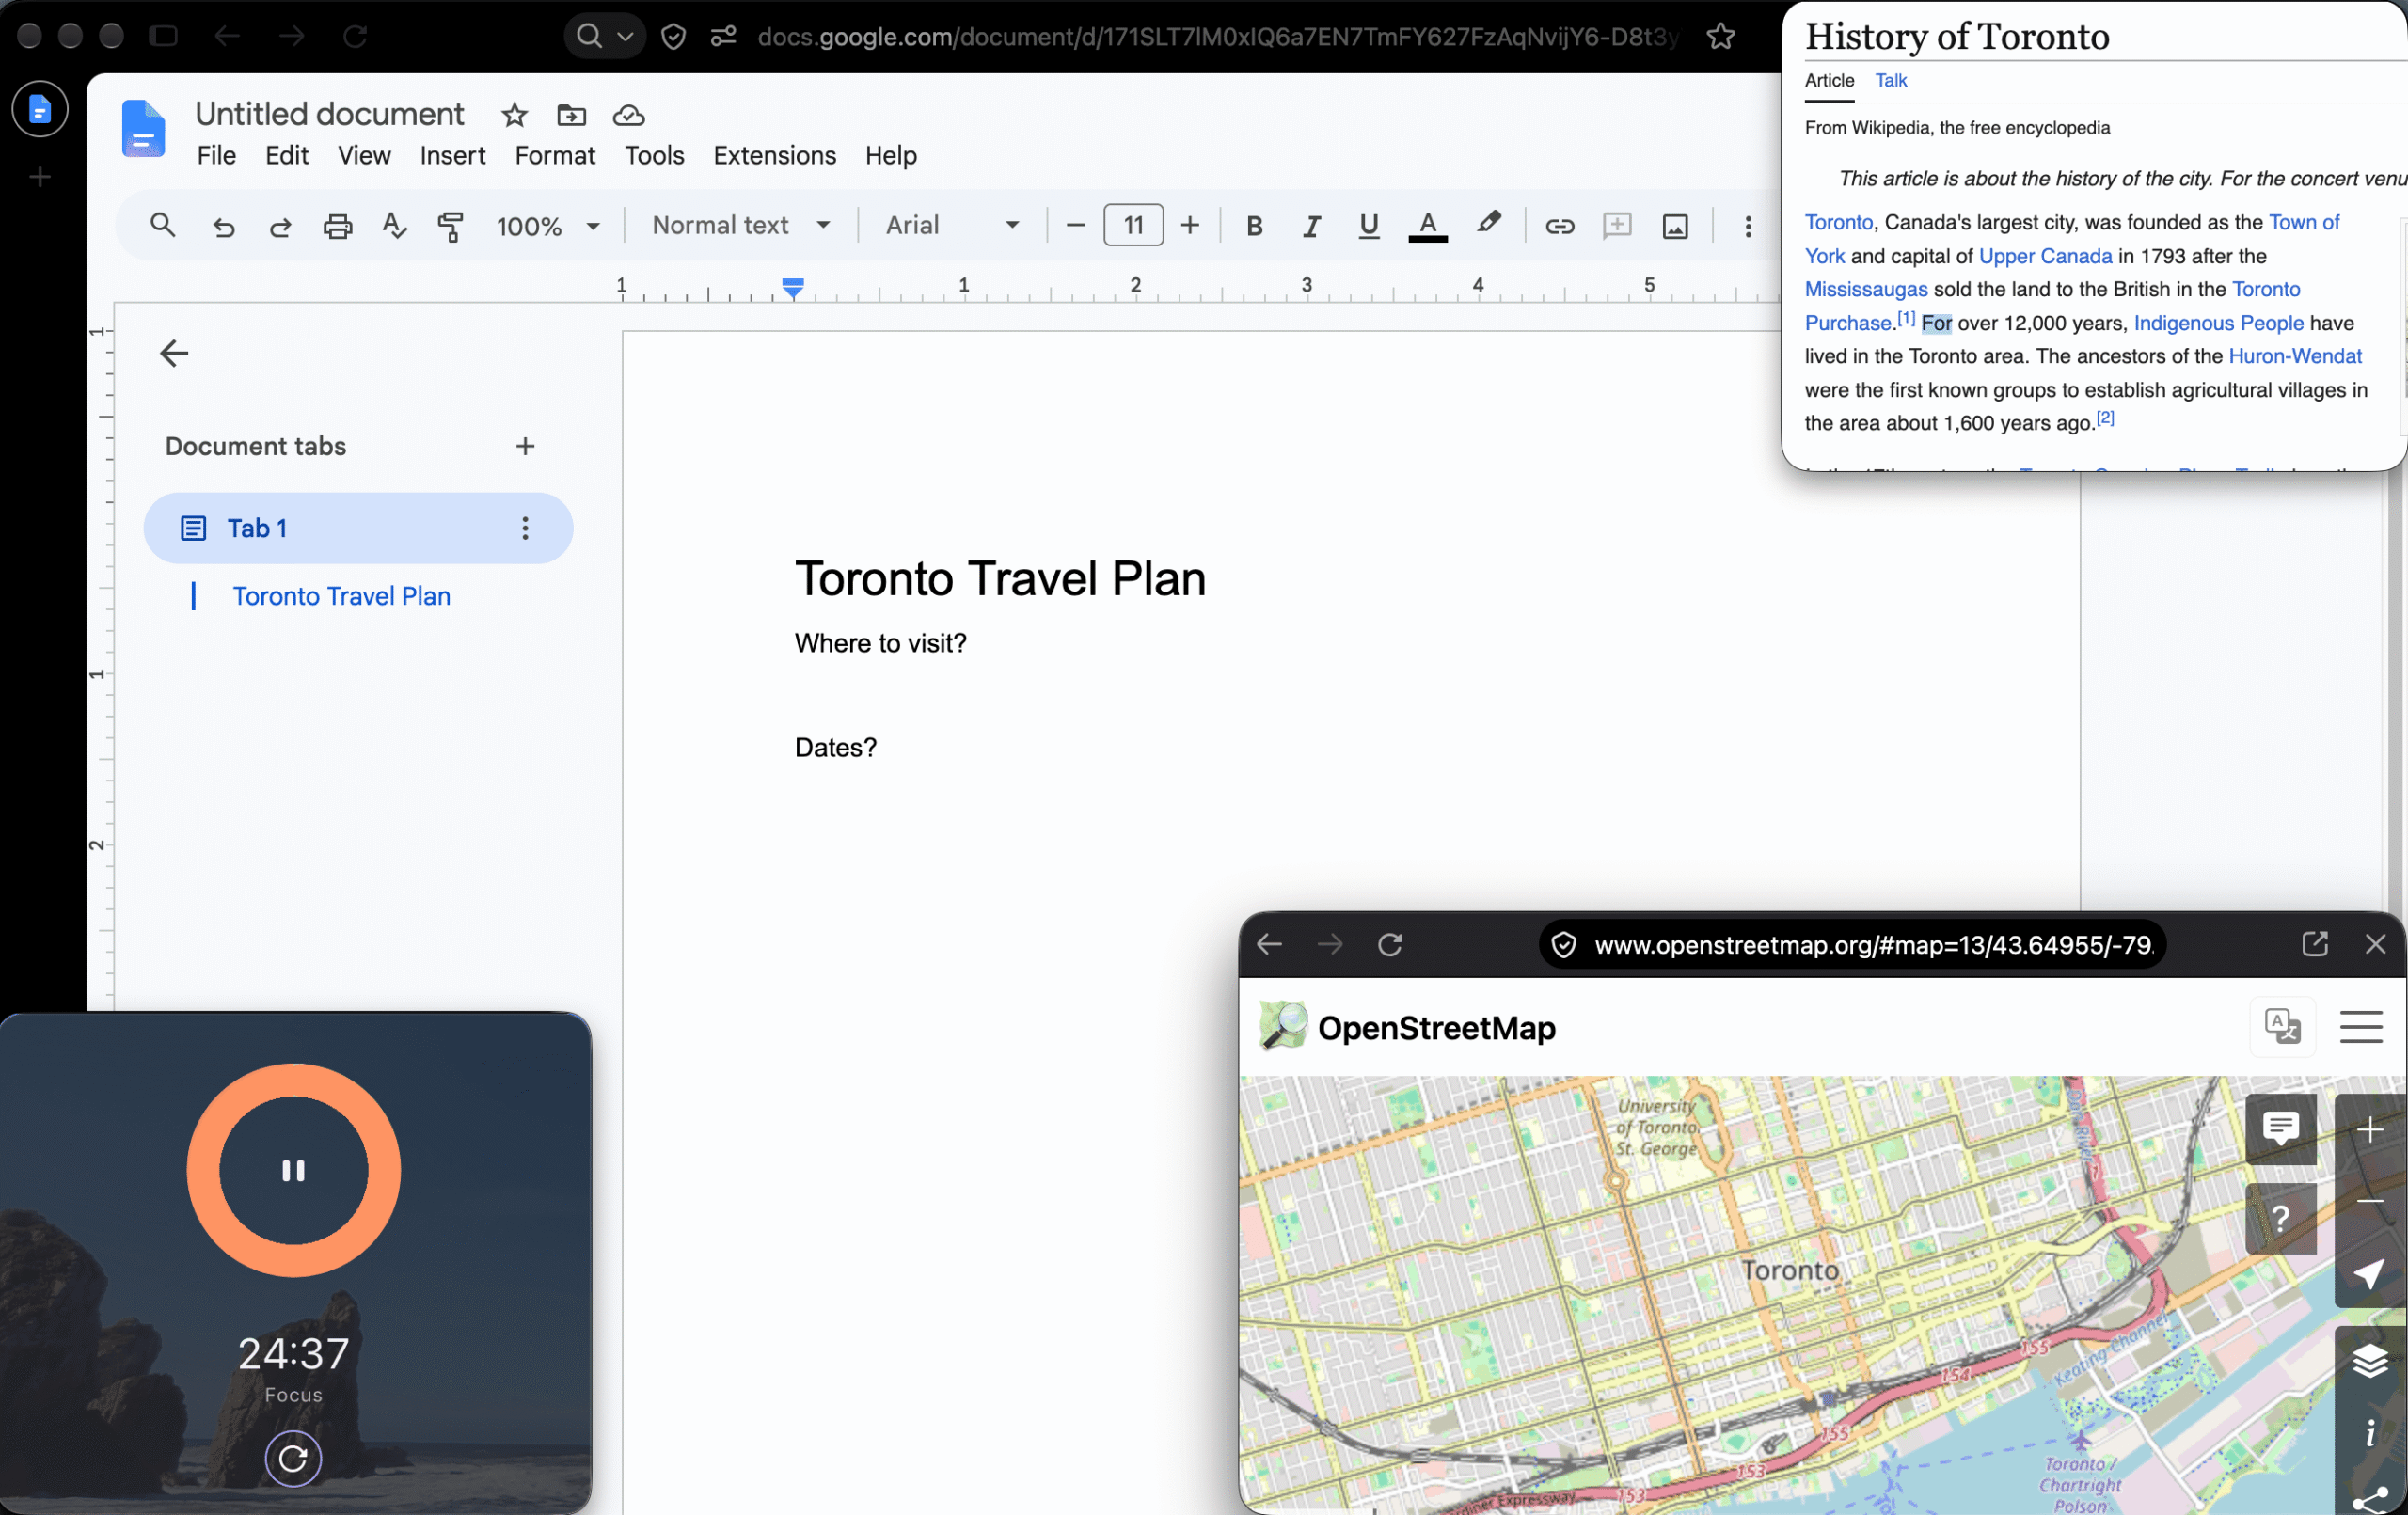
Alt...
Desktop mit geöffnetem Google-Docs-Dokument „Toronto Travel Plan“ und den Fragen „Where to visit?“ und „Dates?“. Darüber liegen Fenster mit einem Wikipedia-Artikel zur Geschichte Torontos, einer OpenStreetMap-Karte und einem Fokus-Timer.
Open Source Summit Europe 2026 - OSS Directory
Beteiligung statt blosser Nutzung
Am Open Source Summit Europe in Prag hat die Linux Foundation eine neue Studie zum Stand von Open Source in Europa vorgestellt. Wie das Linux-Magazin berichtet, standen digitale Souveränität, der Umgang mit KI-generiertem Code und die Erfahrungen der Stadt München mit freier Software im Zentrum.
https://www.ossdirectory.com/de/topnews/details/open-source-summit-europe-2026 #OpenSource #Linux

Soooooo. Got made redundant a few weeks ago. Boredom kinda set in while job hunting. So what did I do? Wrote an alternative to FreeLens that worked on mobile so I can keep an eye on my K8S clusters properly 🤷
Kubernetes-Integrationstests mit kind und Testcontainers
Ein erfolgreicher Test mit Mocks sagt wenig darüber aus, ob eine Anwendung im Cluster ihre Datenbank erreicht. Mit kind und Testcontainers lässt sich der Weg prüfen. Am Beispiel einer Bestell-API entsteht eine kurzlebige Testumgebung, die eine Anfrage bis in PostgreSQL verfolgt und bei Fehlern...
https://www.linux-magazin.de/ausgaben/2026/12/kubernetes-integrationstests/
#linux #opensource #Kubernetes #Docker #kind #Testcontainers
Alt...
Draufsicht auf 16 gerippte Frachtcontainer in Grün, Gelb, Blau, Grau, Weiß und Rot, die in vier Reihen auf einer grauen Fläche angeordnet sind und lange Schatten werfen.
DWProton that's popular for various Anime games on SteamOS / Linux has a new release out, to bring fixes for the latest Wuthering Waves updates.
https://www.gamingonlinux.com/2026/11/wuthering-waves-fixes-for-steamos-linux-in-the-new-dwproton-11-0-17-release/
#Steam #OpenSource #RPG #SteamOS #Anime #OpenWorld #Proton #Misc
Dolphin erhält die Miller-Spaltenansicht zurück
https://linuxnews.de/dolphin-erhaelt-die-miller-spaltenansicht-zurueck/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #KDE #Dolphin #OpenSource
Improvements and new features coming to #LibreOffice, from new contributors (with help from experienced mentors): JPEG XL import, better Writer test coverage, and OpenType MATH: https://blog.documentfoundation.org/blog/2026/11/16/libreoffice-and-google-summer-of-code-2026-the-results/ #foss #opensource #freesoftware
Mousam 3.0: Wettervorhersage mit ansprechendem Design
https://linuxnews.de/mousam-3-0-wettervorhersage-mit-ansprechendem-design/
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #Mousam #Mousam3 #Wetter #OpenSource
Editorial
Personalmangel im öffentlichen Dienst – kann KI ein Ausweg sein? In Bayern passt man schon ein Gesetz an, dass das möglich machen soll.
https://www.linux-magazin.de/ausgaben/2026/12/login/
Alt...
Porträt eines lächelnden Mannes mit grauem, gewelltem Haar. Er trägt einen grauen Pullover über einem weißen Hemd und sitzt vor einer hellen Holzwand.

🧭 Who Pays Your Bills? The Open Source Triangle
🧩 Open source software is everywhere, but few people ask the obvious question: who pays the people who build it? That’s exactly how the OPENGIS.ch ( (http://qgis.org/)) story began. “Who pays your bills?” was the first question its future CTO asked, back when the two founders didn’t even know each other. Years later, they co-founded a company that thrives on open source.
Today, OPENGIS.ch stands behind QGIS and QField and proves that open source is not just a philosophy, but a sustainable business model. It takes three things: sustainability, community and entrepreneurship. Only when all three come together can open source software flourish and its contributors make a living from it.
💡 In this talk, Marco Bernasocchi shares how OPENGIS.ch built a sustainable business around QGIS and QField, how the Spatial without Compromise · QGIS community works, and why open source is a real business opportunity.
🌍 Don’t miss it, a must for all international visitors!
🤝 A big thank you to OPENGIS.ch, our Gold Partner at DINAconCH 2026!
👉 Register here: DINAcon 2026 in Bern | Wissenschaft & Technik
https://eventfrog.ch/de/p/wissenschaft-technik/dinacon-2026-bern-7490308037581749165.html
#DINAcon2026 #CHOpen #OpenSource #DigitalSustainability #QGIS #QField #OpenSourceBusiness #GIS
Espressif und Bastler bringen reguläres Linux auf den ESP32-S31
Ein reguläres Linux läuft jetzt nativ auf dem ESP32-S31. Möglich macht das die Speicherverwaltung des neuen RISC-V-Mikrocontrollers.
Per Vibe-Coding: Kinoklip - DaVinci-Resolve-Klon für Linux mit allen Codecs, mehr Power auf schwacher Hardware
https://www.slashcam.de/news/single/Kinoklip---DaVinci-Resolve-Klon-fuer-Linux-mit-alle-20373.html
#Linux #LinuxNews #LinuxDE #LinuxNewsDE #EULE #EULEde #OpenSource #VideoEditing
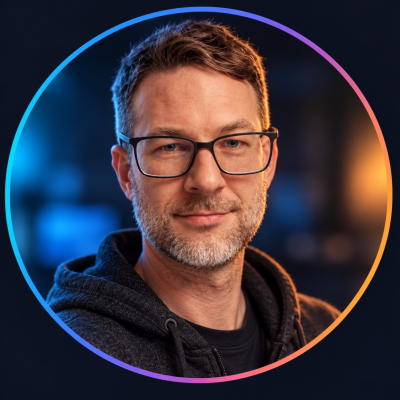
Our AI team's bottleneck moved.
In the first two weeks our agents merged up to 169 PRs a day. CI was the limit: we ran 5 extra CI servers.
Since 3 November, every PR needs reviewer approvals from several vendors, on the same head. Today: 2 approvals from 2 vendors that didn't write it. Now it's 25–60 PRs a day, the median from open to merge went from 0.7 to 3 hours, and 2 CI servers are enough.
Review is our pace now.

A new build of littleFedi (2026.11.16) is out!
The Little Computer People have been busy, and we're happy to share a new release of littleFedi!
Before reading the long changelog, there's something important we'd like you to know about upgrading.
⚠️ Important: Upgrading littleFedi
This release includes database migrations that run automatically on the first startup. Some of them may take a while, especially on larger databases or slower hardware.
Please read these instructions carefully before upgrading.
-
Stop littleFedi and make a backup.
Back up your database, configuration, and media files. Remember to save any encryption keys stored in the service environment, too.
See
docs/backup-restore.mdfor backup and restore instructions. -
Replace the binary.
Download the new binary for your operating system, CPU architecture, and database/media backend. Replace the old binary and start littleFedi using your existing configuration.
No separate migration command is needed.
-
Allow the database migrations to finish.
littleFedi will automatically perform the necessary migrations on its first startup. One of these rebuilds SQLite indexes and may take considerable time on large databases, particularly when running from an SD card.
Make sure your service manager allows enough time for startup.
Do not stop or restart littleFedi while migrations are running.
-
Check that everything is ready.
Wait for startup to complete, then check the logs and the
/readyzendpoint before using your instance.Subsequent startups will skip migrations that have already completed.
Need to roll back?
Stop littleFedi and restore your pre-upgrade backup before starting the previous binary.
Never run an older binary against a migrated database.
What's new?
As with previous releases, many of the changes come directly from the people who make this project worthwhile: our friends on this instance, those who have started self-hosting littleFedi, and everyone who has taken the time to test, report bugs, suggest improvements, or review our code.
We've continued working on the things that matter to us: keeping littleFedi lightweight, efficient, reliable, and enjoyable to use, without unnecessary complexity.
And yes, we're still very much committed to making the Fediverse accessible even to the smallest computers!
Here's what's changed in this release:
Changelog
-
Account blocks now hide posts in profiles, search, threads, quotes and
streaming, and stop new follows, mentions, replies, favourites, reactions,
poll votes, boosts and direct messages in both directions. Blocked profiles
keep only the account's identity and block/report actions. Existing direct
conversations stay readable, and email and push notifications check for
blocks before sending. Other accounts on the same server remain reachable,
even when they share an inbox. Public posts remain available to anonymous
readers and other instances.
-
Static blog pages now leave out unlisted replies. Only replies with public
visibility are included. Rebuild existing blogs after upgrading to remove
unlisted replies from pages generated by earlier versions.
-
Content warnings now display apostrophes and other HTML entities correctly
in posts and notifications, instead of showing codes such as
'. -
Source builds now require Go 1.27.4. Updated the Go dependencies, bundled
Alpine.js and htmx, and the security tools used in CI. Rebuild existing
binaries to pick up the Go security fixes.
-
With
housekeeping.max_delete_per_run = 0, status pruning now keepsgoing in batches of 500 until no eligible posts remain. Previously, remote
pruning stopped after 500 posts and local pruning after 500 per account.
Positive limits still apply across local and remote posts. Failed deletions
are left for the next run rather than retried in a loop.
-
The inbox no longer fetches a key for an unknown actor's self-delete.
Requests with a Signature header are acknowledged with
202and droppedwhen the actor and deleted object are the same URI and the account is absent
locally. Domain blocks still apply; deletes of known accounts and posts
still need authentication.
-
Incoming HTTP signatures now have their timestamps and body digests checked
before fetching a public key or verifying the signature. Stale requests and
damaged bodies can be rejected without a network request.
-
Public instance counts on
/aboutand the v1/v2 instance APIs are cachedfor 30 seconds, instead of counting the database on every request. The
admin dashboard still reads fresh counts.
-
SQLite reply and quote indexes now leave out NULL entries. This reduces
their size and avoids a slow query plan when loading RSS feeds. Migration
007 rebuilds all four indexes at startup and can be slow on large databases,
especially on SD cards. Allow extra time for the first startup after
upgrading; later starts skip the migration.
-
The interface is now available in Catalan, thanks to Jolupa, who
translated it. It can be picked in the settings like the other languages,
and Catalan is also in the list of languages a post can be tagged with.
Strings added after the translation was made were filled in afterwards and
are the ones most worth a second look.
-
Boosts can be scheduled, to spread them out instead of filling followers'
timelines all at once. Hold the boost button for half a second, or open the
post, and pick a time under "Boost later". A quick press still boosts right
away. Scheduled boosts show up on the Scheduled page next to scheduled
posts and can be moved or cancelled there. If the post is deleted or
becomes impossible to boost before then, the boost is dropped. Mastodon
apps have no notion of a scheduled boost, so the API leaves them out.
-
Scheduled posts can now be edited, not just moved to another time. The
Edit button on the Scheduled page opens the post in the composer with
everything it had, including the time, and saving puts it back on the
schedule. Before, the only way was to cancel it and write it again. A post
that is already being published can no longer be edited.
-
Posts can be saved as drafts. The composer has a "Save draft" button next
to Post, and the new Drafts page lists them, newest first. Opening one
brings back the text, content warning, audience, language, attachments,
poll and expiry, and the post it replies to or quotes. Posting or
scheduling a draft removes it. Everything is a plain form, so it works
without JavaScript and in text browsers. Drafts live on the server and are
not shared with Mastodon apps, which have no API for them.
-
The image viewer can now move between the pictures of a post. Use the
arrows on screen, the left and right keys, or swipe on a phone. Before, each
picture had to be closed and the next one opened by hand. Without
JavaScript nothing changes: each picture still opens on its own.
-
In French the image viewer had no name for screen readers. The apostrophe
in "Visionneuse d'images" broke the expression that sets it. Translated
labels are now read from data attributes, so quotes in a translation can no
longer break the script.
-
The Roost theme works better on phones. Post actions fit on one row, the
back link is a flat row instead of a pill against the screen edge, the
profile banner and avatar no longer fill the first screen, and the bottom
bar marks the current page without a filled block.
-
Unread mentions and direct messages now stand out from the other unread
notifications. In Roost the mention colour was the same blue as the unread
mark, and in every theme their rows took the same background as any unread
row. Herd and Ink also get mention colours further from their accent.
-
Filters set to warn now work on the catch-up page. The filtered posts were
shown in full, without the filter notice. Filters set to hide already
worked there.
-
Direct message notifications have a magenta edge, an envelope icon and their
own label, so they stand apart from public mentions.
-
Boosts from a followed account can now be hidden from the home timeline,
with the "Hide boosts" button on their profile or the matching switch in
Mastodon clients. Their own posts still show up. Boosts already in the
timeline go away too, and come back if boosts are shown again. The
reblogsparameter of the follow API was accepted but ignored until now. -
Push delivery now follows up to three 307/308 redirects within the same
HTTPS origin. The Mastodon app relay redirects endpoints without a trailing
slash; those pushes previously failed after all retries.
-
Pushes for favourites, boosts and federated mentions now carry
notification_id. Those jobs were built before the notification was stored,so the ID was missing, and the official iOS app showed only the relay's
placeholder trumpet instead of the notification.
-
The bookmark button on boosted posts now stays in sync after refreshing
the home timeline. Before, it could appear inactive while the post was still
bookmarked, and clicking it again removed the bookmark.
-
Replies no longer show the previous post as unavailable after it has been
downloaded. Refreshing or reopening the reply now keeps the correct reply
target in timelines, boosted posts and Mastodon clients. The open thread
page also updates its reply label as earlier posts arrive.
-
Redrew the quote icon. The old one, two squared-off hooks side by side,
could be read as "SS". It now looks like a pair of quotation marks.
-
Logging in with toot from the command line now works. toot opens
/oauth/authorize/with a trailing slash, which returned 404. URLs with atrailing slash are now routed like the ones without, as on Mastodon.
-
With
require_approvalon, new accounts were created already approved: theycould sign in at once and never showed up in the approval queue. They now
wait for an administrator. Accounts registered while the bug was present
stay approved; check recent signups if the setting is on.
-
Filter keywords created from a Mastodon client with
whole_wordturned offwere saved with it on. Leaving
whole_wordout still means on, as inMastodon.
-
Mastodon apps no longer show littleFedi's own notification types (follow
accepted, unfollows, blocks, emoji reactions, blog rebuilds and others) as
broken entries, and their unread badge no longer counts them. A client can
still ask for them with
types[], which the notification endpoints nowhonour.
exclude_types[]=pleroma:emoji_reactionnow works too. -
The
user:notificationstream carries only notifications. Before, it alsosent home timeline posts, which some clients (Tuba) showed as empty
notifications.
-
The instance documents report
image_matrix_limitas a pixel count, takenfrom
max_image_pixelsandmax_image_dimension. It was 4096, which clientsread as 4096 pixels in total and used to shrink uploads to a thumbnail. The
video limits Mastodon's iOS app requires are there too.
-
New client API endpoints:
GET /api/v1/accounts?id[]=,
/api/v1/accounts/lookup,/api/v1/accounts/familiar_followersand
/api/v1/notifications/policy. Mastodon for iOS and Tuba call them. -
Push notifications now reach the Mastodon apps (Mastodon for Android and
iOS, Tusky, Ice Cubes, Ivory, Mona). Apps that don't ask for
standard: trueget the olderaesgcmencoding, which is the only oneseveral of them can decrypt, and every push now carries the access token
and a numeric notification ID, without which the apps drop it. Form encoded
subscriptions are accepted, and the subscription ID is a number as the apps
expect. Subscriptions made before this release keep the old behaviour:
turn notifications off and on again in the app, or sign in again.
-
Polls no longer break Mastodon for iOS and Android.
own_votesandemojisare always lists, and
expires_atuses Mastodon's date format. -
Deleting a post from an app returns the deleted post with its source
text,so "delete and redraft" keeps the text. Deleting it twice returns 404.
-
Timeline paging:
min_idreturns the page right after the cursor instead ofjumping to the newest posts, which made apps skip everything in between when
filling a gap. A cursor pointing at a deleted post keeps working, and an
unknown
max_idreturns an empty page instead of the top of the timeline.
min_idandsince_idwork for notifications too. -
Linkheaders are now absolute URLs and keep the other query parameters.Followers, following, blocks, mutes, favourites, bookmarks, lists and list
members send them too, so apps can load more than the first page.
-
Media sizes are reported under
meta.originalas well, and remote mediakeep their blurhash and size. Apps used them to lay out images before they
load.
-
Accounts without an avatar or header point to a placeholder image instead of
an address that returned 404. Accounts also report
uriand
hide_collections, and relationshipsrequested_byandlanguages. -
The default post visibility and language set in the profile are reported to
apps and used when an app leaves them out.
-
/api/v2/instancereports the VAPID key underconfiguration.vapidand
translation.enabled. Mastodon for iOS reads both. -
Loading images, avatars and emoji no longer counts against the rate limit.
Scrolling a busy timeline could hit it, and every API call after that failed.
An API request over the limit now gets a JSON error with
Retry-After, andunknown API routes return JSON 404 and 405 errors instead of HTML.
-
littleFedi now logs a warning when requests come from a local reverse proxy
that is not listed in
http.trusted_proxies. In that case every visitorshares the proxy's rate limit.
-
CORS preflight allows the headers the browser asks for (
Idempotency-Keyamong them) and exposes
LinkandRetry-Afterto web clients. -
Idempotency-Keyis honoured when posting: a retried request returns thepost created the first time instead of a duplicate.
-
Tokens from
client_credentials(the app's own token, before a user signsin) are treated as anonymous on public endpoints instead of being refused.
-
Filters:
keywords_attributesworks when creating and editing a filter, inJSON and form encoding, and the
/api/v2/filters/:id/keywordsand
/api/v2/filters/keywords/:idendpoints are new. -
New endpoints:
GET /api/v1/accounts/search,
/api/v1/statuses/:id/history,/api/v1/timelines/directand
/api/v2/notifications/unread_count. -
The streaming API accepts the token in
Sec-WebSocket-Protocol, as theMastodon web client sends it, and tokens limited to
read:statusesand
read:notifications. -
The "Clear all" button on the notifications page is now called "Delete
all", in every language, since that is what it does.
-
Profile fields: up to four label and value rows on your profile, edited in
Settings or from any Mastodon app, and shown under the bio on the profile
page. They are sent to other servers like Mastodon's, and the ones remote
accounts publish are now shown on their profiles. Remote accounts already
known get theirs the next time their profile is fetched again. Links work;
verified_atis always empty, as littleFedi does not checkrel="me"links.
-
Apps can mute a conversation (
POST /api/v1/statuses/:id/muteand
/unmute). Mentions, likes, boosts, quotes, edits and reactions in thatthread stop notifying you.
-
Apps can keep a private note on an account
(
POST /api/v1/accounts/:id/note). Only you see it. -
Followers can be removed from an app
(
POST /api/v1/accounts/:id/remove_from_followers). A remote follower'sserver gets a Reject of the follow, as from Mastodon.
-
Conversations can be removed from the list from an app
(
DELETE /api/v1/conversations/:id); a new message brings them back.
POST /api/v1/conversations/:id/readworks too. -
Saving the profile from an app with an empty bio or display name now clears
it. Before, empty values were ignored and the old text stayed. The default
post visibility and language set in an app are saved too.
-
MastoBlaster could not read its push subscription: the
alertsobject hadno
updatekey. It is now there, and apps can turn on pushes for editedposts. Renaming a list and changing push alerts from MastoBlaster failed
with 405, because it sends
PATCH; both endpoints now takePATCHas wellas
PUT, like Mastodon. -
Three database migrations run at startup. One adds the
standardand
access_tokencolumns topush_subscriptions. One adds
accounts.fields_jsonand thethread_mutes,account_notesand
hidden_conversationstables. The last adds
push_subscriptions.notify_update. All of them only add, nothing existingis changed, and all can be rolled back.
A big thank you to everyone who has been following this little adventure, testing new builds, sharing feedback, and helping us improve.
littleFedi is still a young project, and there's plenty more to do. But every release brings us a little closer to what we've wanted from the beginning: a federated social platform that's simple to run, easy to maintain, and doesn't require a powerful server just to participate in the Fediverse.
Small computers deserve a place in the Fediverse, too. ❤️
Happy upgrading, happy self-hosting, and stay tuned!
The Little Computer People
#littleFedi #Fediverse #SelfHosting #OpenSource OwnYourData


Schon interessant wie mein Institut mit ihrem Microsoft zu kämpfen hat. Unser IT Störfall geht sicher auch darauf zurück. 🙈
Meine Schatten IT lief immer reibungslos. Keinerlei Störfälle oder Downtime, während die offizielle IT immer mal wieder Schluckauf hat. 🙈
Aber ja. Ich musste auf Druck der offiziellen IT meine Schatten IT abschalten. Jetzt haben sie den Salat. 🤷🏼♂️
Meine Schatten IT hat ein Bruchteil an Kosten pro Jahr verursacht. 🥹
PyPI launched a redesigned project page with a new PyPI Security Tab displaying package provenance, digital attestations, and supply chain warnings.
#PyPI #Python #SupplyChainSecurity #Cybersecurity #OpenSource #TechNews
https://securityonline.info/pypi-security-tab/?utm_source=mastodon&utm_medium=jetpack_social

Hello #InfoSec!
I just released the open-source core of IJRAP Security (GNU AGPLv3), an offline-first forensic evidence sealer written purely in the #Python standard library (zero dependencies).
It binds audio, video, photos & text with UTC timestamps, GPS & hybrid hashing (SHA-256 + SHA-3-256) to protect #Journalism & #HumanRights field data.
Code & docs: https://github.com/ijrapmedia/ijrap-security-public
Security reviews and feedback are very welcome! #Forensics #OSINT #OpenSource
just released Baud, a terminal emulator I wrote in Rust.
It’s my daily terminal on Linux (Wayland, via my NixOS config) and macOS.
• Images, GIFs and video, right in the terminal
• Works out of the box: no config, fonts and icons bundled
• The core is a separate library other programs can embed
Named after Baudot’s 1874 telegraph code. The goal: draw every character a program sends, correctly and on time.
Try it: nix run github:baud-terminal/baud
https://github.com/baud-terminal/baud
#Rust #RustLang #NixOS #Nix #Linux #Terminal #CommandLine #OpenSource
WhatsApp Web audio/video calls in LibreWolf: mic cuts out, video also broken (fine in Brave)
cross-posted from: lemmy.ml/post/55341521
Hi all,
WhatsApp Web calls are unreliable in LibreWolf on Debian 13. Both voice and video calls have problems:
- The receiver sometimes hears nothing from me (mic works intermittently)
- Video calls also fail or glitch
- The same calls work fine in Brave on the same machine
Already tried:
- RFP disabled, fingerprintingProtection enabled (no change when disabled)
- media.peerconnection.enabled = true
- Mic/camera permissions allowed for web.whatsapp.com
Has anyone gotten WhatsApp Web calls working reliably in LibreWolf, and what did you change?
#Linux question for Linux people:
If I use this method to install a Brother printer driver on my computer (#Fedora / #Gnome), can I delete all the driver files afterwards?
If I can't, then I'd like to tuck them away in some out-of-the-way spot in my computer rather than leaving them junking up my Downloads folder. But if I *can* delete them, then I can do the installation from that Downloads folder, like the instructions recommend.
https://support.brother.com/g/b/faqend.aspx?c=us&lang=en&prod=dcpl2550dw_us&faqid=faq00100556_000
 [
A documentary on KDE, one of the best desktop environments out there: https://tube.kockatoo.org/w/76dca815-c72e-49e3-af59-a6c3691865a1
Instead of idolizing Jensen Huang who closed sourced his invention and inflated its value with AI bubble as CEO of a megacorp, why don't you look up to actual heroes like David Patterson who invented RISC architecture philosophy and shared it with the whole world which gave us ARM and MIPS, and eventually led to development of RISC-V as an ISA open for all of us to use around the world?
David Patterson deserves the same attention for his works and willingness to share his works with all of us openly.
Here is an episode of Computer Chronicles from 1986 where he is a guest talking about his invention: https://youtu.be/DIccm7H3OA0?si=8Zakf5pvHGr6_4Ok
#opensource #jensenhuang #ai #risc_v #riscv #risc #arm

Alt...
David Patterson attending a Computer Chronicles episode back in 1986. On screen is the "young" David, with his yellowish hair and old style glasses and suit, on screen is written DAVID PATTERSON Professor U.C. BERKELEY.
#skiek blbox 4
Damit das Skript automatisch beim Start von Linux Mint ausgeführt wird, muss es unter „Startprogramme“ richtig eingetragen werden.
Der Befehl im Beispiel lautet:
/bin/bash "/home/djtom26/ton/ton.sh"
Wichtig: „djtom26“ ist nur ein Beispiel für einen Benutzernamen und muss durch den eigenen Benutzernamen ersetzt werden. Auch der Ordnerpfad muss zum eigenen Speicherort passen.
So startet der kleine Signalton automatisch im Hintergrund. 😊
#LinuxMint #Linux #Bluetooth #OpenSource
Ex-Cyanogen-Chef McMaster stellt Linux-System #Kora vor | heise online https://www.heise.de/news/Kora-OS-Ex-Cyanogen-CEO-kuendigt-Linux-Betriebssystem-fuer-Desktops-mit-KI-an-11518988.html #ArtificialIntelligence #AI #Linux #OpenSource
Could you survive without Microsoft? Inside the costs of digital dependence
#Tech #AI #Microsoft #DigitalDependence #IEA #EWaste #DataCentres #DigitalSustainability #Environment #Internet #OpenSource #Cybersecurity #DigitalEconomy #Electricity #COP31 #Drought #The14Media
https://the-14.com/could-you-survive-without-microsoft-inside-the-costs-of-digital-dependence/

📅 Di.Day ist zurück, am 14.11.2026 schauen wir uns das Thema E-Mail an.
Du hast ein anderes Thema auf dem Herzen? Bring es gern spontan mit💡
🗓️ Samstag, 14.11. | 🕙 10 bis 12 Uhr
📍 @stabuebuedelsdorf , Zur Bücherei 3, 24782 Büdelsdorf
Vorwissen brauchst du nicht, nur Neugierde!
Fragen sind ausdrücklich erwünscht 🙂
Mehr Infos findest du hier 👉 https://events.diday.org/events/8e633d66-5a99-4a6a-9e99-c85ac12f55d6
#diday #dut #rendsburg #budelsdorf #email #fediverse #linux #opensource #oss