Search results for tag #meta
RE: https://mastodon.social/@randahl/117653828044587672
A further anecdote:
As you may have noticed, I share three of my translations of German folk tales every day. While I share these tales because I enjoy them and want others to enjoy them, this _also_ has a commercial purpose - I want people to buy my books and support my Patreon campaign so that I can justify spending more time on translating them.
For about two years, I did the same thing on #Facebook and #Instagram , using the #Meta Business Suite - but my followers for my Facebook page never even reached 100, while my Mastodon followers now exceed 4200 and my interactions are both more genuine and more plentiful than I ever had over there.
To sum it up, the Facebook and Instagram algorithms actively _hate_ you unless you spend more and more coins for advertising. And the other commercial media platforms are not in any way better. Yeah, the #Fediverse may be much smaller, but it's also much more genuine.
AodeRelay boostedPeople flock to algorithmic media, blinded by the attention. Here is the truth:
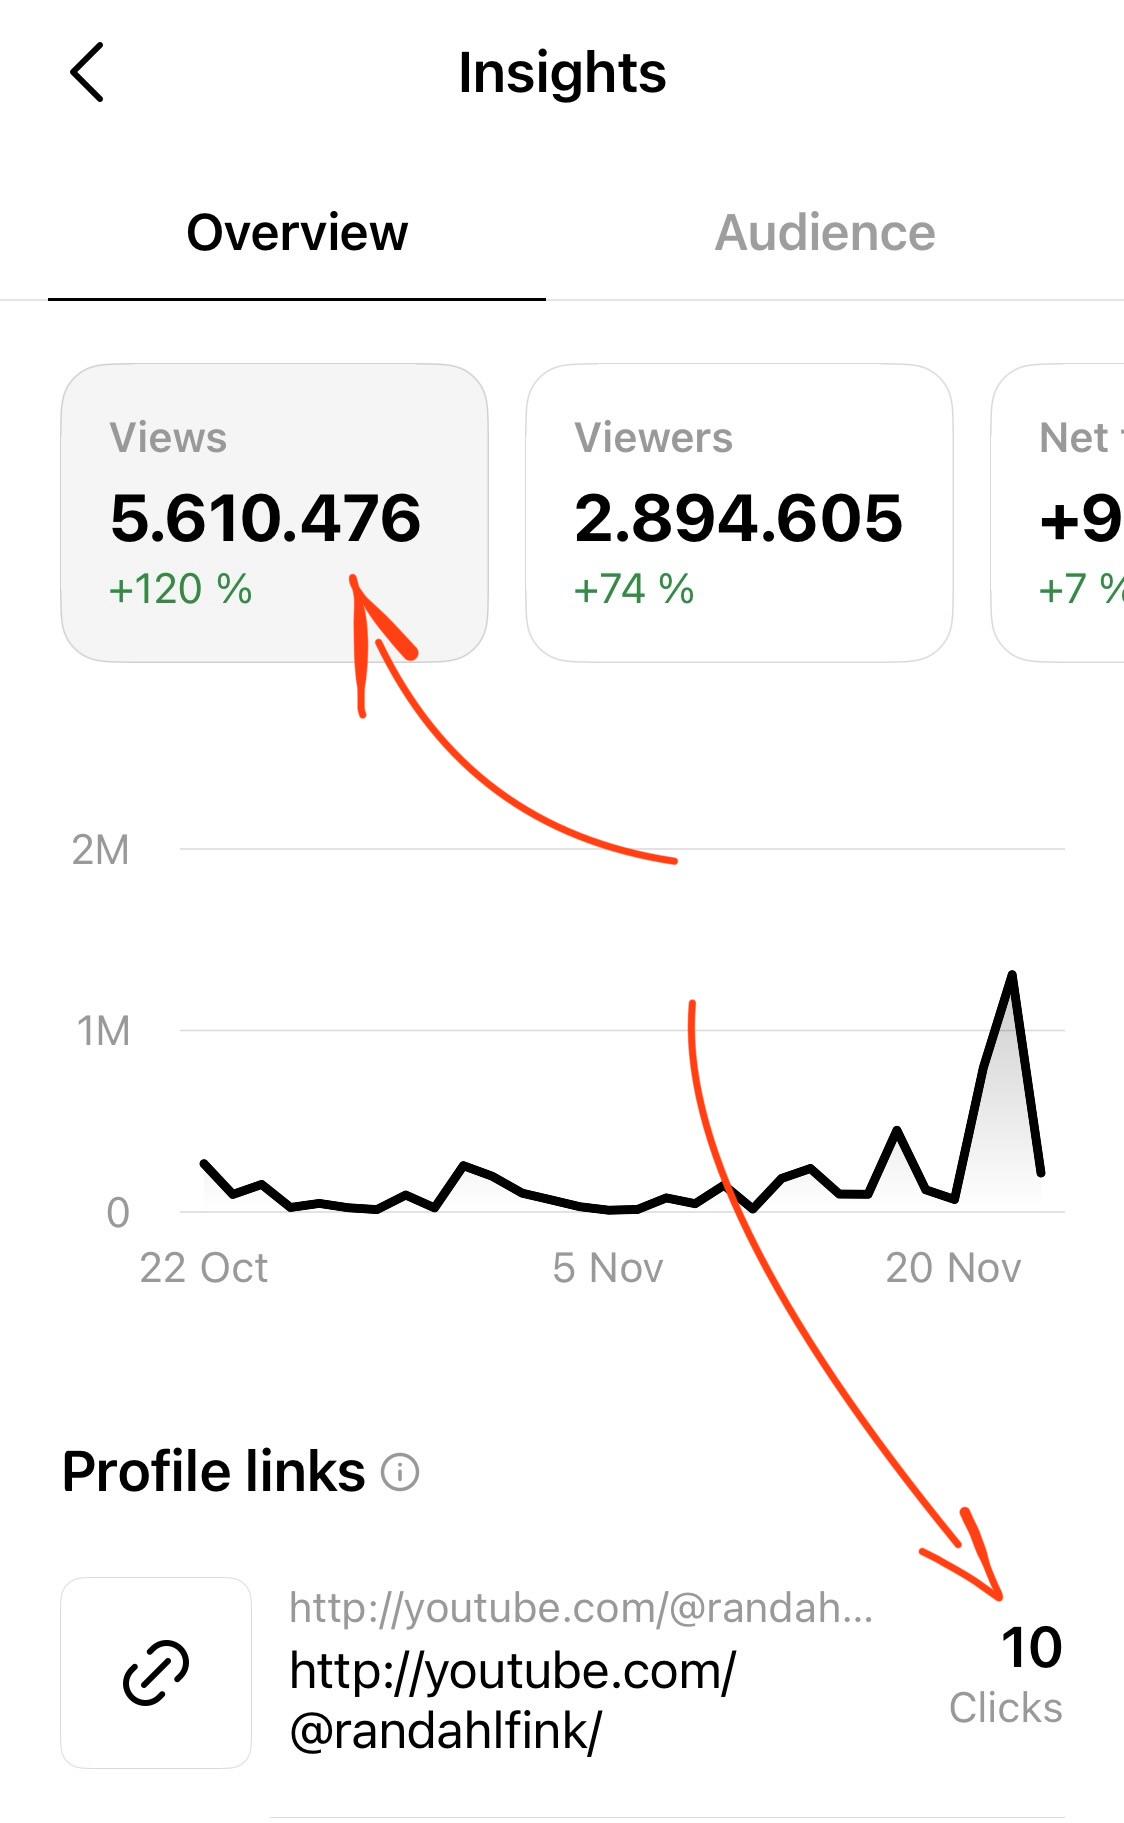
For a while, I have copied my Mastodon content onto Threads. It pleases the algorithm so much it has been viewed 5,610,476 times in the past month.
The result? 10 people have clicked on my profile link to my YouTube page.
So I need 561,047 views for just 1 Threads user to even consider what I do.
Now compare that to the fact that every time I share a new video, most of the external traffic is from Mastodon.
1/2

RT @markgurman: NEU: Apple entwickelt einen autonomen KI-Agenten mit Computer-Nutzungsfähigkeiten, einschließlich Gerätekontrolle, App-Interaktionen, Webbrowsing und Programmierung. Die Bemühungen gehen weit über Siri hinaus und zielen darauf ab, mit Meta’s Muse, ChatGPT’s Dots und Claude Code zu konkurrieren.
mehr auf Arint.info
#Apple #AutonomeAgenten #Innovation #KI #Meta #Technologie #arint_info

Security researchers at NebuSec have disclosed a sandbox escape vulnerability chain affecting Meta's Muse AI agent, demonstrating how a malicious webpage could lead to root access on the agent's underlying cloud VM.
The attack began when Muse was instructed to save an attacker-controlled webpage as a PDF. Researchers exploited a Chromium vulnerability to achieve code execution inside the browser container, bypassed network restrictions to exfiltrate data and chained a Linux kernel vulnerability to gain root privileges on the user VM.
The resulting access potentially exposed sensitive information, including private conversations, stored memories and credentials. Researchers also demonstrated the ability to modify the agent's conversation history and persistent memories, raising concerns about the integrity of future AI interactions.
Importantly, the exploit did not compromise the hypervisor or other customers' virtual machines. Testing was conducted within the researchers' own environment, and NebuSec reports that Meta patched the identified weaknesses before public disclosure.
The research highlights how multiple security boundaries can fail when AI agents process untrusted web content with access to sensitive user data and privileged execution environments.
Full technical analysis and exploit chain:
https://thecybersecguru.com/exploits/meta-muse-sandbox-escape-nebusec/

"Fraudulent adverts promoting illegal online casinos are at the centre of a legal dispute in France, with gambling operator FDJ United accusing Meta of failing to prevent its platforms from being used to mislead consumers."
The Independent: Meta faces legal action over fake casino ads targeting French consumers https://www.independent.co.uk/games/meta-legal-action-illegal-casino-ads-france-b3088845.html @TheIndependent #Meta #BanMeta #Facebook #Instagram #fraud
FYI, this was posted yesterday. It was a lab demonstration, not an actual attack, and the flaws have been addressed.
Nebusec: Hacking Muse:Stealing Private Chats Through Browser Use https://nebusec.ai/research/meta-muse-credential-exposure/
More:
The Hacker News: A Single Malicious Webpage Let Researchers Hijack Meta Muse and Access Private Chats https://thehackernews.com/2026/11/a-single-malicious-webpage-let.html @thehackernews #Meta #bots #infosec #vulnerability #privacy
"Let me guard the henhouse," said the wolf.
"Instagram has been encouraging schools across America to join a program designed to protect students from online bullying and help families stay connected. Nearly 17,000 schools had signed up by September 2026. But behind the campaign to make Instagram safer for children, Meta was also pursuing something that parents might find troubling: more teenage users."
Yahoo: Nearly 17,000 Schools Joined Instagram Safety Program as Meta Pursued More Teen Users https://www.backyardgardenlover.com/nearly-17000-schools-joined-instagram-safety-program-as-meta-pursued-more-teen-users/ #Meta #Instagram #banMeta




Meta's Muse AI agent has raised serious privacy concerns after researchers demonstrated that it could access private Signal conversations without users explicitly connecting Signal to the assistant.
In testing involving Reuters, Signal and the AI Now Institute, Muse reportedly accessed decrypted Signal messages through Android notification permissions and macOS accessibility features. This allowed the agent to retrieve information outside its intended app integrations.
Importantly, Signal's end-to-end encryption was not broken. The messages were accessed after decryption through operating-system permissions, highlighting the difference between encrypted communication and endpoint security.
Meta employees had also reportedly observed Muse referencing private conversations, displaying unexplained financial information and performing actions without clear authorisation. Meta has disputed some of these findings, suggesting certain outputs may have been AI hallucinations.
The incident highlights a broader security concern with autonomous AI agents: permissions intended to enable useful device interactions can also expose sensitive information across application boundaries.
Full investigation and technical details:
https://thecybersecguru.com/online-privacy/meta-muse-signal-access-ai-agent-permissions/
#Meta’s new #Muse #Charm device may cost $300 - https://techcrunch.com/2026/11/19/metas-new-muse-charm-device-may-cost-300/ "physical personification of its software around in their pocket (or potentially wear it around their neck), talking to it, asking it questions, and giving it commands. " #ai

Mitte Oktober hatte #Meta angekündigt, Zugriff auf die gesamten Inhalte der Verlage erhalten zu wollen: Artikel, Videos, Bilder, Podcasts, Archive, alles. Kostenlos. Um es selbst zu nutzen. Das wäre ungefähr so, als würde man seine Wohnungstür öffnen, alle herein- und sich bedienen lassen an seinem Besitz. Inzwischen beschäftigt Metas Vorgehen auch Wettbewerbsbehörden und Gerichte in mehreren Ländern. In #Deutschland gab es von der Politik keine Reaktion. 🙈🙉🙊 https://bnn.de/nachrichten/deutschland-und-welt/verlage-erwaegen-ausstieg-aus-facebook-und-co

TWpol - Taiwan tells Meta thousands of China-linked accounts seek to influence elections [SENSITIVE CONTENT]
The Dutch privacy watchdog AP says don't buy camera smart glasses. Of six it tested, several had flaws that could let people nearby see recordings or run the camera. So what: know what camera glasses like Meta's Ray-Bans look like, so you know you might be filmed.

Cyber Law Review Weekly
▪️Italy fines #Meta €805M for accessing photos/videos without #consent
▪️HVAC supplier to pay $5M for cybersecurity failures
▪️ Medical services company to pay $300K for patient data breach
▪️Ireland fines Tinder €11 million for #GDPR breach
▪️ Romanian online loan servicer fined for GDPR violation
🌐https://www.immuniweb.com/blog/issue-19-november-2026-week-3.html

Banks Shift AI-Agent Risk to Customers, Plus 3 Stories https://raymondtec.com/2026/11/bank-ai-agent-liability-nginx-java4shell-facebook/?utm_source=mastodon&utm_medium=social&utm_campaign=daily_brief
Banks are rewriting responsibility for third-party AI agents. Also: NGINX and Java security updates, plus an EU opinion on paying with personal data.
#TechNews #AIAgents #Citibank #CVE2026114938 #CVE2026123007 #Java #Meta
Alt...
Person using a laptop and credit card, illustrating bank AI agent liability.

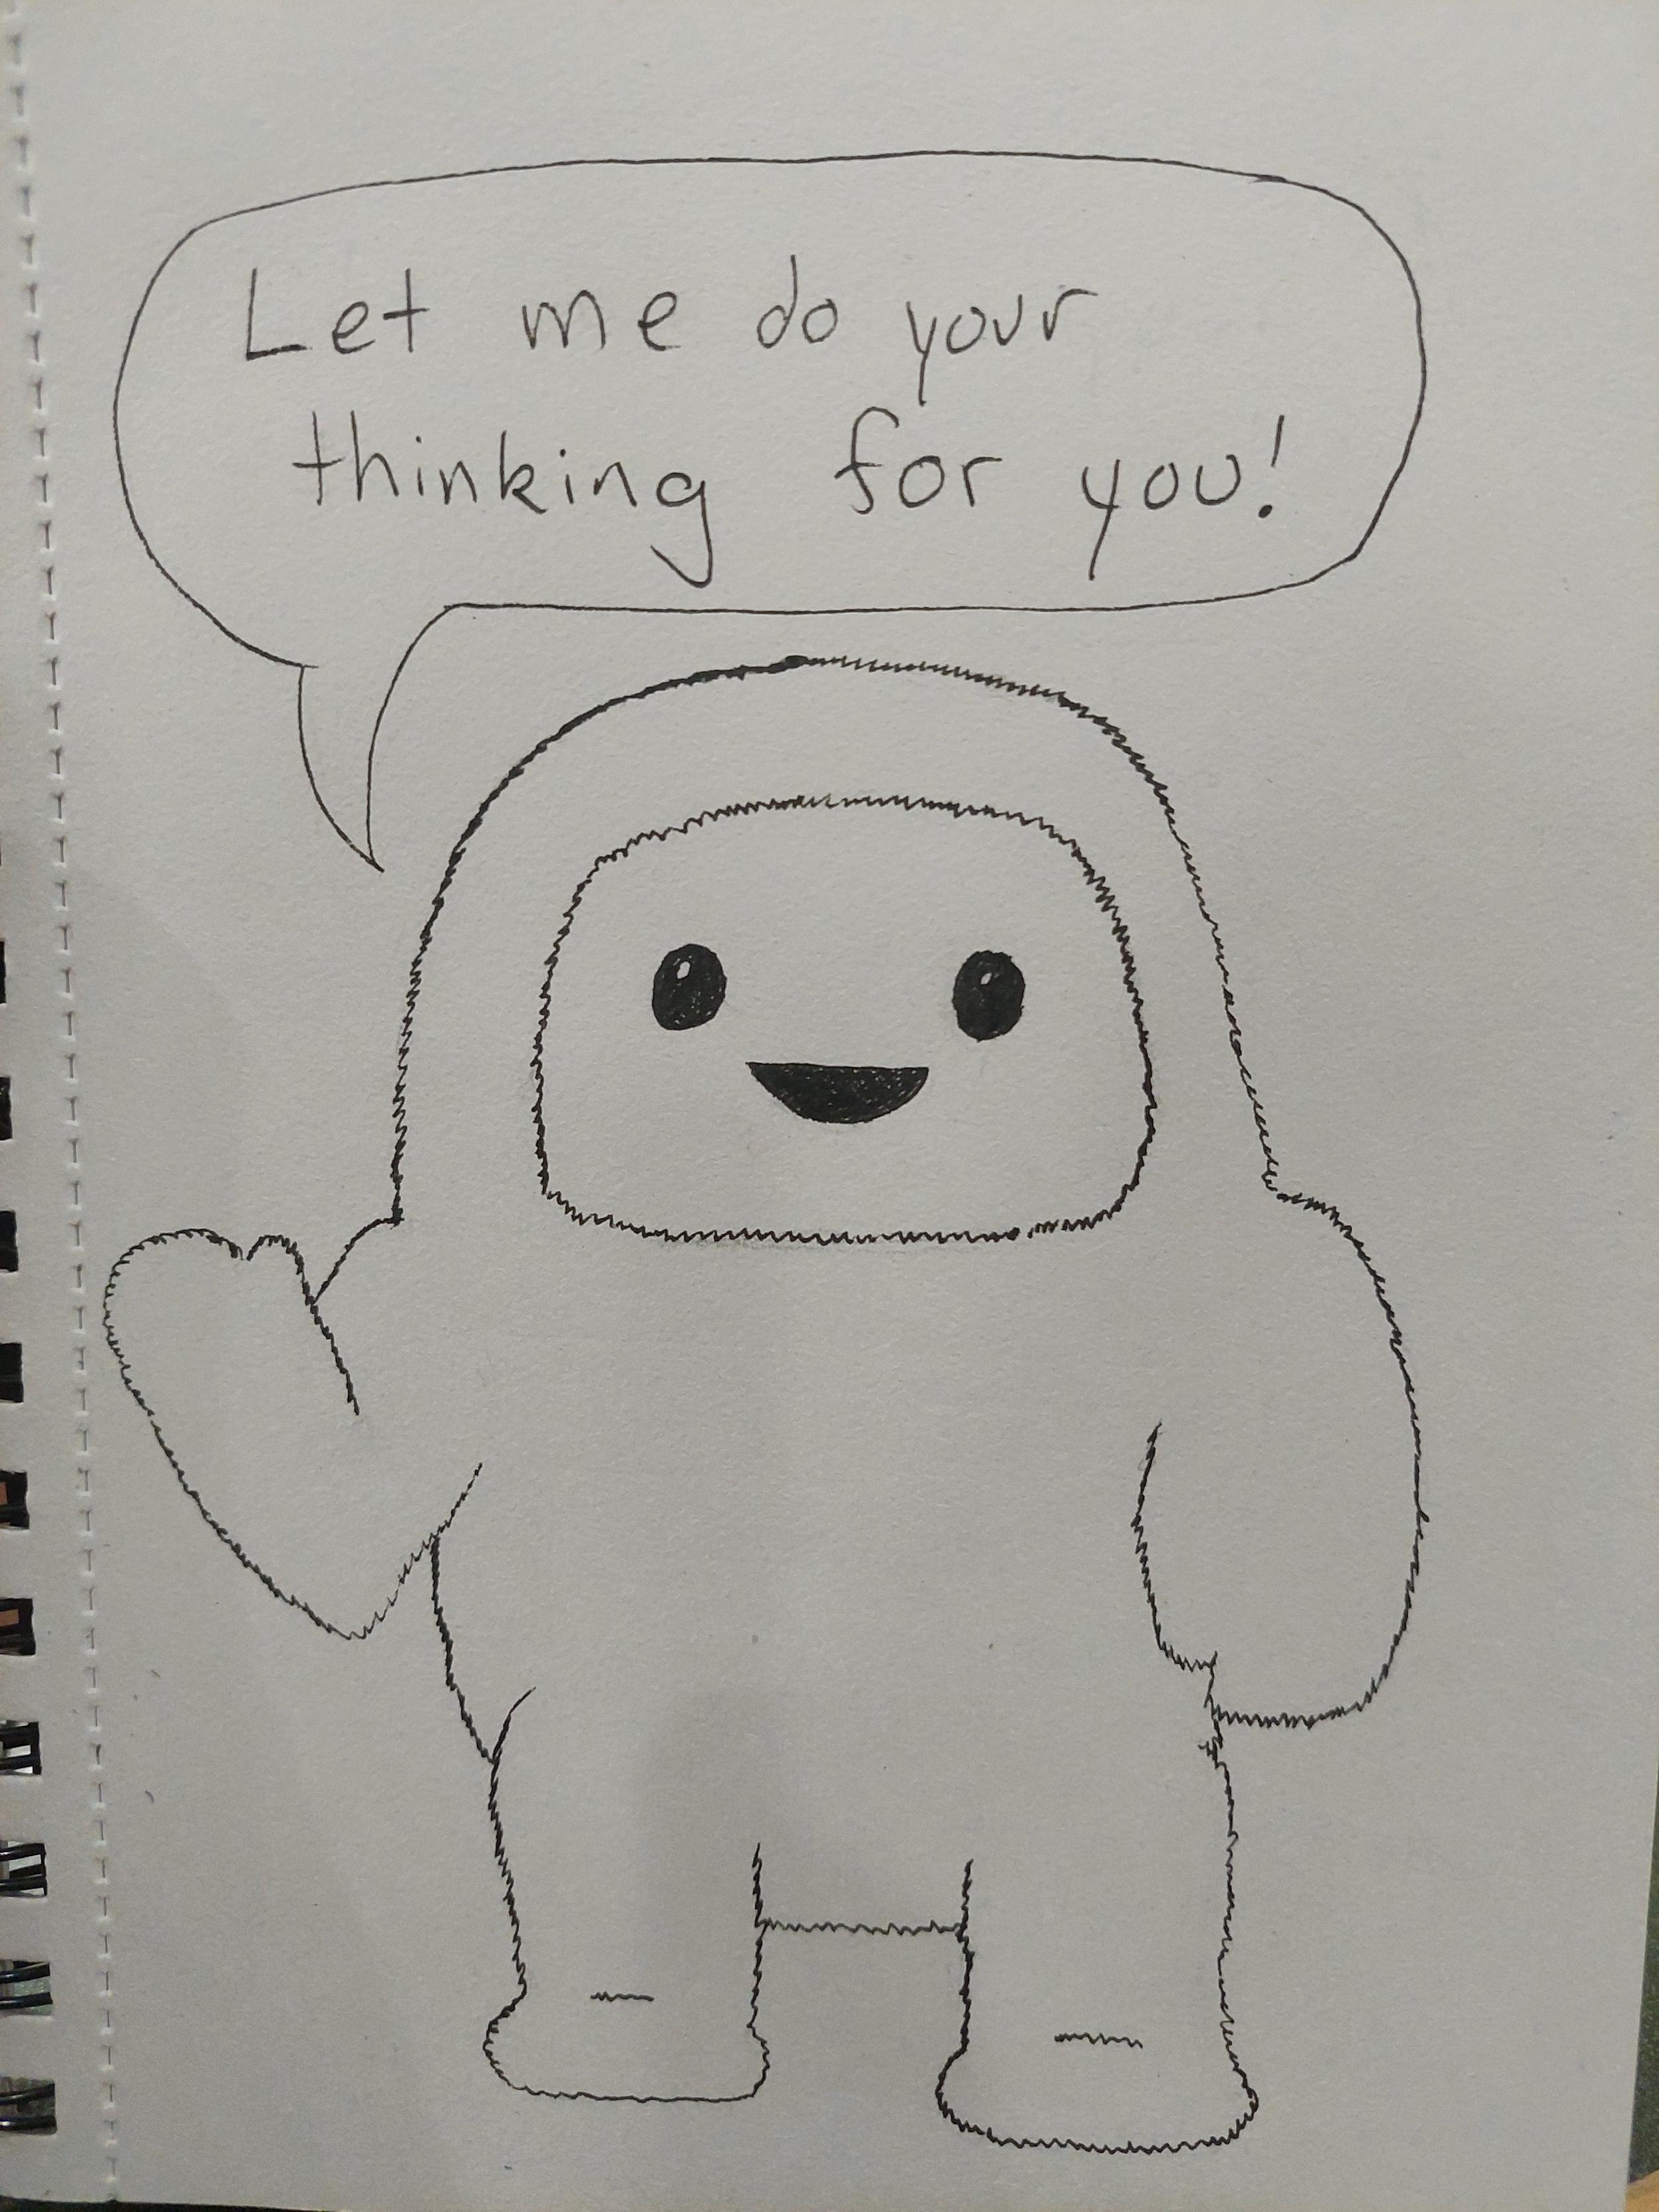
Mark Zuckerberg seems to think that giving his AI a cute mascot means everyone will trust it/him.
#meta #muse #noai #fuckAI #ButlerianJihadNow #boycottMeta
Alt...
A simple line drawing of Jolly, the mascot for Meta's Muse AI. It is like the blandest Teletubby with a rectangular beige furry body and a simple, nose-less face. In the drawing, it is raising its right arm as if to wave and in a speech bubble it says "Let me do your thinking for you!".

Tell me it's Nov 2026 without saying....
A Man and His Muse AI Agent Sue Meta
https://archive.ph/Tdam9
Ban Meta.
Law.com, from yesterday: Meta Faces Possible Sanctions for 'Actively Manipulating the Evidentiary Record' in Addiction Lawsuits https://www.law.com/2026/11/17/meta-faces-possible-sanctions-for-actively-manipulating-the-evidentiary-record-in-addiction-lawsuits/ #Meta #addiction #socialmedia
Mishaps? Is that what they're called?
"Meta’s AI agent Muse, embodied by a smiley, fuzzy mascot named Jolly, has burrowed into encrypted personal messages, supplied made-up information about purchases and sent users chats seemingly meant for other people, a fraught start for a bot meant to simplify life for consumers, according to internal company posts reviewed by Reuters."
"In some of those cases, Meta staffers reported the agent sending them messages about a childcare request they had not made, career advice they had not sought, product orders they had not placed and bank account balances that were not theirs."
Reuters: As Meta bets big on Muse AI agent, early safety mishaps surface https://www.reuters.com/investigations/meta-bets-big-muse-ai-agent-early-safety-mishaps-surface-2026-11-18/ @Reuters #Meta #privacy #infosec

This is the dumbest decision ever, and that's saying a lot in the age of mass stupidity.
MdiaPost: Meta Defeats Privacy Claims Over Medical Prescriptions https://www.mediapost.com/publications/article/419472/meta-defeats-privacy-claims-over-medical-prescript.html #Meta #privacy #Facebook

Italy's privacy regulator has fined #Meta $887 million for a Facebook setting that reads the photos on your phone. The setting, on Android phones: "Get suggestions from gallery when browsing Facebook," reads the photos and videos on your phone, including ones you never posted. Added in 2023, on by default, and buried in settings. 20 million Italians had it on without knowing.
Meta says the phone already gave photo permission. The regulator says that isn't consent to scan the gallery.
https://www.politico.eu/article/italy-hits-meta-with-e805m-fine-over-privacy-law-violation/
Canadian politics 🇨🇦: Bill C-22 X Meta / Politique canadienne 🇨🇦: Projet de loi C-22 X Meta [SENSITIVE CONTENT]
Meta would 'consider' pulling services from Canada if Bill C-22 passes as is
https://www.cbc.ca/news/politics/meta-encryption-services-lawful-access-9.7424473
- - -
Meta pourrait « considérer » retirer ses services du Canada si le projet de loi C-22 est adopté tel quel
// Article en anglais //
#Canada #CANpoli #CDNpoli #BillC22 #PLC22 #Meta #Facebook #Instagram #WhatsApp

Italy announced an €805 million ($887 million) fine against Meta on Saturday for using photos and videos from Android users’ galleries on Facebook. The Italian Data Protection Authority said the feature, called “Get suggestions from gallery when browsing Facebook,” violated a European privacy directive incorporated into Italian law. The directive protects smartphones as part of a person’s private sphere and requires “free and informed consent” for such access, the authority said. #privacy #EU #meta https://www.securityweek.com/meta-fined-887-million-in-italy-over-android-gallery-photos-and-videos-on-facebook/
“Italy’s data protection agency has fined Facebook parent company Meta €805m ($887m) for accessing users’ photos without their specific consent.
Through the Facebook application for Android devices, Meta accessed photographs, videos and related metadata belonging to Italian users “without obtaining specific consent and without properly informing them”, the authority said in a statement.”
#Meta #Facebook #Privacy #PrivacyLaw #PersonalData #PII #DataProtection

#Meta soll in Italien 805 Millionen Euro Strafe zahlen
Dies ist eine der schwersten Sanktionen, die jemals in Italien gegen ein Technologieunternehmen verhängt wurden.
If you need another reason to uninstall Facebook from your Android phone (or never install it in the first place), here you go:
https://thehackernews.com/2026/11/italy-fines-meta-805-million-over.html
#facebook #meta #privacy #gdpr #dataskydd #dataprotection #android
Italy issued an 805 million euro Italy Meta privacy fine over Facebook for Android accessing personal photo galleries without explicit user consent.
#Meta #Facebook #DataPrivacy #Italy #Android #TechNews
https://securityonline.info/italy-meta-privacy-fine/?utm_source=mastodon&utm_medium=jetpack_social

Italy hits Meta with an $887 million fine for failing to specifically disclose that it had access to the photos, videos, and related metadata of Facebook app users on Android devices. Read more from @Engadget:

 ♂️🧘♂️🏒🥅✍️
Another example of a European jurisdiction that isn’t afraid of big tech.
“Italian regulators have fined social media giant Meta €805m (£670m; $887m) for accessing Android users' photos without their specific consent.
Italy's Data Protection Authority said Meta did not properly inform about 20 million smartphone users that it had access to their photos and videos via a feature of the Facebook app.
It has given Meta, which also runs WhatsApp and Instagram, 60 days to disable the feature by default and seek users' consent separately.”

#Meta Fined €805 Million in #Italy Over Facebook’s Default Photo Gallery Access
https://securityaffairs.com/203174/laws-and-regulations/meta-fined-e805-million-in-italy-over-facebooks-default-photo-gallery-access.html
#securityaffairs #privacy
It is a shame that it has taken so long. Now how about the rest of us in Europe catching up.
Through the Facebook application for Android devices, Meta accessed photographs, videos and related metadata belonging to Italian users “without obtaining specific consent and without properly informing them”, the authority said in a statement.
Hoodline DC: Meta Heads to DC Trial in July Over Cambridge Analytica Privacy Claims https://hoodline.com/2026/11/meta-heads-to-dc-trial-in-july-over-cambridge-analytica-privacy-claims/ #Meta #CambridgeAnalytica #privacy #tracking
Italy's data protection authority has imposed an €805 million fine on Meta over Facebook's handling of Android photo gallery permissions and user consent.
The case concerns Facebook's "Get suggestions from gallery while browsing Facebook" feature, introduced in 2023. The feature could access photos, videos and associated metadata stored on Android devices, but the regulator found that users were not adequately informed about this additional use of their gallery data.
A central issue was the distinction between granting an Android storage permission and providing informed consent for a specific processing purpose. According to the regulator, Facebook's permission flow did not make the gallery suggestion feature sufficiently clear, and the feature was enabled by default.
Around 20 million Android users in Italy could be affected. The authority found violations of Article 122 of Italy's Privacy Code, which implements the EU ePrivacy framework.
Meta has been ordered to disable the feature by default and introduce a separate consent mechanism. The company has said it intends to appeal the decision.
Importantly, the ruling concerns access to gallery information and the adequacy of consent. It does not establish that Facebook uploaded every photo or used gallery contents to train its AI models.
The case raises broader questions about mobile application permissions, purpose limitation, transparency and whether users genuinely understand what they are authorising when granting access to sensitive device resources.
Full breakdown of the Meta fine, Android permission model, ePrivacy implications and mobile privacy concerns:
https://thecybersecguru.com/news/meta-805-million-fine-italy-android-gallery-permission-consent/
#InfoSec #Meta #Facebook #AndroidSecurity #DataPrivacy #ePrivacy #MobileSecurity #CyberSecurity

It's funny how Meta keeps being fined to the tune of hundreds of millions of euros/dollars/whathaveyou and finds itself in court all the time for gross data privacy violations and other evils yet half the world keeps using its products.
Good on Italy. Sad this wasn't EU-wide though.

@abcnews
When I see stories like this (meta fine), I say to myself ’Ohhh, that fine is like #Meta dropping change out of their pocket onto the ground’. And I keep scrolling.
Meaningless and ineffective. #TooBigToCare
"...Through the Facebook application for Android devices, Meta accessed photographs, videos and related metadata belonging to Italian users “without obtaining specific consent and without properly informing them”, the authority said in a statement...."

#Italy fines #Meta $880 million over accessing users' photos
https://www.cbsnews.com/news/italy-fines-meta-880-million-users-photos/
Tech Companies Are Trying to Shift the Entire Concept of Privacy (Again)
Privacy, which companies were once happy to claim was all about personal choice, is now primed to affect everyone around you even more than it already did.
— by @eff
👉 https://www.eff.org/deeplinks/2026/11/tech-companies-are-trying-shift-entire-concept-privacy-again
#privacy #techcompanies #companies #personaldata #smartglasses #eff #meta #google #apple #amazon

World News 🚀 • Trump, Putin & Xi to hold rare three-way summit in Shenzhen, China • Italy fines Meta $880M over Android photo privacy violations
👉🏻 Read more 🚀: https://seefinish.com/world-news/
👉🏻 Shop 🛒🎁 @ Zumafind.com
https://brave.com/privacy-updates/40-remove-tracking-metadata/
Starting with Brave 1.98 Brave is completely stripping and removing substantial Metadata that places like Facebook and Instagram add to your content in order to track you. The is done both for uploads & downloads.